CYFIRMA Reports N0n Extortion Group’s Maritime-Sector Targeting, With Breach Claims Unconfirmed
Summary
CYFIRMA says N0n posted 38 maritime-sector victim claims across 18 countries in October. No listed organization has publicly confirmed a breach, though KISA reportedly notified Korean firms and one acknowledged an intrusion notice.
Key points
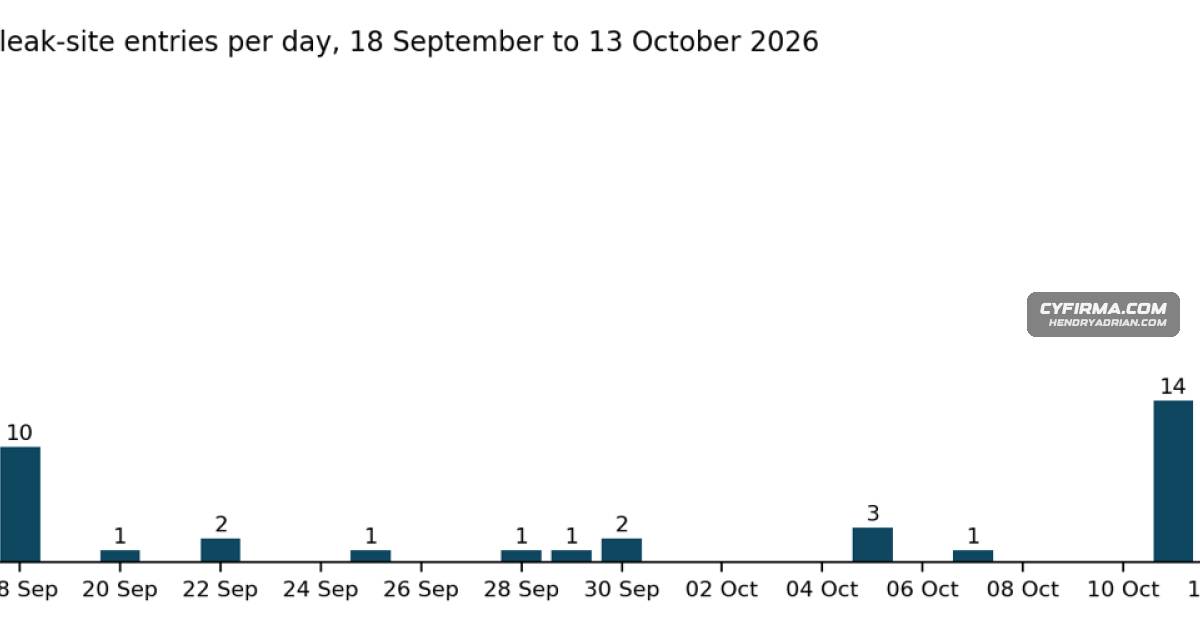
- CYFIRMA recorded 76 N0n leak-site entries through 13 October, estimating they represent 64–66 distinct organizations.
- The group posted 38 maritime and logistics entries across 18 countries within 23 minutes on 12 October; 26 were in Asia, including 12 in South Korea.
- No listed organization has publicly confirmed a breach. KISA reportedly notified Korean port companies, and one firm acknowledged receiving an intrusion notice.
- The report assesses N0n likely had access to at least some listed victims, but says claims of encryption, backup destruction, and network disruption remain unverified.
- N0n claims data including EDI archives, terminal-system material, invoices, and credentials; CYFIRMA has not validated the published data’s contents.
- CYFIRMA recommends reviewing links to listed parties, rotating shared credentials, enforcing MFA on remote access, and monitoring for the scheduled 19 October data release.
Article Details
- Publisher
- CYFIRMA Research
- Report Period
- Information collected through 2026-10-13; report published 2026-10-16
- Scope
- N0n leak-site activity and claimed victims from 2026-09-18 to 2026-10-13, with emphasis on the maritime supply chain.
- Sample Size
- 76 leak-site entries; an estimated 64–66 distinct organisations after deduplication.
- Key Statistics
- 38 maritime and logistics entries across 18 countries and territories were posted within 23 minutes on 2026-10-12.
- The 38 maritime entries include 26 organisations in Asia, including 12 in South Korea.
- CYFIRMA recorded 76 entries from 2026-09-18 to 2026-10-13, estimated to represent 64–66 distinct organisations.
- 52 of 76 entries (68%) were posted on 2026-10-11 and 2026-10-12.
- Recommendations
- Rotate EDI, SFTP, API, and port community system credentials shared with listed parties, and review access logs from mid-September onward.
- Require MFA on RDP, VPN, Citrix, and cloud administration consoles, and remove direct internet exposure of RDP.
- Monitor the N0n leak site and RSS feed through the stated publication deadline, and review published file trees for organisational references.
- Search infostealer log sources for corporate domains and reset passwords for exposed accounts.
- Maintain immutable or offline backups and test restoration.
MITRE ATT&CK
T1021.001 · Remote Desktop ProtocolRemote Desktop Protocol use is assessed by CYFIRMA; no confirming artefacts were identified.T1074 · Data StagedData staging is assessed as consistent with the contents of the leak-site listings.T1078 · Valid AccountsCYFIRMA assesses use of valid accounts as the most probable initial-access vector, but identifies no confirming artefact.T1486 · Data Encrypted for ImpactN0n claims encryption, but CYFIRMA found no encryptor or ransom note; treat this mapping as actor-claimed and unverified.T1490 · Inhibit System RecoveryN0n claims backup destruction, but CYFIRMA found no confirming artefacts; the capability remains unverified.T1657 · Financial TheftCYFIRMA supports this mapping with leak-site extortion demands and the group's claim that a victim paid.
Threat Actors
Tools
Countries
AustraliaSaaS vendors and small businesses, mainly in the US and Canada, with single cases in the UK and Australia, remain exposed to opportunistic targeting.BrazilIndonesia (4) and Brazil (4) follow.Canadafinancial services, managed service providers, SaaS vendors and small businesses, mainly in the US and Canada, with single cases in the UK and Australia, remain exposed to opportunistic targeting.ChinaElsewhere the batch is thin: one or two organisations each in Japan, China, Singapore, Taiwan, Hong Kong, Vietnam and India, five in Europe including Türkiye, two in the Gulf and one in Morocco.Germanyin the Middle East and South Korea, a port logistics IT provider in Indonesia, and a port consultancy in Germany. EDI data naming many parties could come from a single hub compromise rather than 38 separate intrusions.Hong KongElsewhere the batch is thin: one or two organisations each in Japan, China, Singapore, Taiwan, Hong Kong, Vietnam and India, five in Europe including Türkiye, two in the Gulf and one in Morocco.IndiaElsewhere the batch is thin: one or two organisations each in Japan, China, Singapore, Taiwan, Hong Kong, Vietnam and India, five in Europe including Türkiye, two in the Gulf and one in Morocco.Indonesiaport community system operators in the Middle East and South Korea, a port logistics IT provider in Indonesia, and a port consultancy in Germany. EDI data naming many parties could come from a single hub compromiseJapanElsewhere the batch is thin: one or two organisations each in Japan, China, Singapore, Taiwan, Hong Kong, Vietnam and India, five in Europe including Türkiye, two in the Gulf and one in Morocco.MoroccoElsewhere the batch is thin: one or two organisations each in Japan, China, Singapore, Taiwan, Hong Kong, Vietnam and India, five in Europe including Türkiye, two in the Gulf and one in Morocco.SingaporeElsewhere the batch is thin: one or two organisations each in Japan, China, Singapore, Taiwan, Hong Kong, Vietnam and India, five in Europe including Türkiye, two in the Gulf and one in Morocco.South KoreaOf the 38, 26 are in Asia, led by South Korea with 12 entries.TaiwanElsewhere the batch is thin: one or two organisations each in Japan, China, Singapore, Taiwan, Hong Kong, Vietnam and India, five in Europe including Türkiye, two in the Gulf and one in Morocco.Türkiyeinternet service provider, a South American government ministry and a pharmaceutical subsidiary in Türkiye.United Kingdomservice providers, SaaS vendors and small businesses, mainly in the US and Canada, with single cases in the UK and Australia, remain exposed to opportunistic targeting.VietnamElsewhere the batch is thin: one or two organisations each in Japan, China, Singapore, Taiwan, Hong Kong, Vietnam and India, five in Europe including Türkiye, two in the Gulf and one in Morocco.