JPCERT Details APT-C-60 Attacks Using SpyGlace in 2026
Summary
JPCERT/CC describes APT-C-60 spear-phishing attacks using RAR-delivered LNK files, mshta.exe, and legitimate developer services to deploy SpyGlace, and publishes related IoCs.
Key points
- Spear-phishing emails delivered a RAR archive through Proton Drive or included the malicious file as an attachment; opening its LNK file started the infection chain.
- The LNK copied itself and used mshta.exe to run embedded JavaScript, which retrieved and extracted a file from jsDelivr and used git.exe to execute a script.
- The script assembled a downloader from files in the extracted folder; subsequent downloaders and loaders retrieved and executed SpyGlace.
- The attackers abused GitHub, GitLab, jsDelivr, and Codeberg as infrastructure, which may make malicious traffic harder to distinguish from normal activity.
- JPCERT observed SpyGlace versions 3.1.15, 3.1.17, and 3.1.18, with no major functional differences from earlier versions identified.
- JPCERT advises caution with suspicious email links and LNK files in archives; the article provides C2, file-hash, and other IoCs.
Article Details
- Attack Vectors
- Spear-phishing emails linked to Proton Drive to induce victims to download RAR archives containing malicious LNK files.
- A similar observed case delivered the malicious file directly as an email attachment.
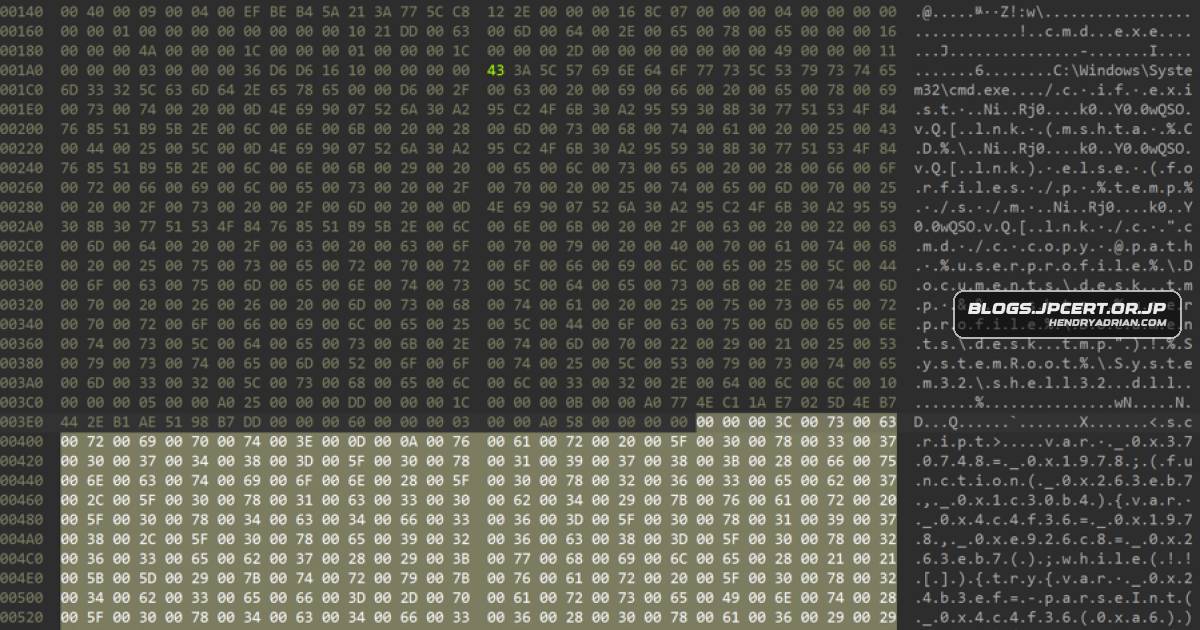
- Opening the LNK file triggered mshta.exe to execute embedded JavaScript, which downloaded, decoded, and extracted additional files.
- A legitimate git.exe executable ran a script that assembled a downloader from .db files. Additional downloaders, loaders, and SpyGlace were retrieved through abused legitimate services.
- Defensive Notes
- Avoid opening cloud storage links in suspicious emails or LNK files contained in archives such as RAR files.
- Detection or blocking based solely on communication destinations is difficult because the attack abuses legitimate developer services and CDNs that are often allowed in corporate environments.
- The infection chain abuses legitimate programs and standard Windows functionality, which the article notes can make detection difficult.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
asako[.]t1011@protonmail[.]com | Spear-phishing email sender identified in the attack. | |
ayuko0328@protonmail[.]com | Spear-phishing email sender identified in the attack. | |
jewexo9791@outlook[.]com | Email address listed as used for commits associated with the attacker repositories. | |
legdevmachine@protonmail[.]com | Email address listed as used for commits associated with the attacker repositories. | |
meimei91@protonmail[.]com | Email address listed as used for commits associated with the attacker repositories. | |
rapefo2905@outlook[.]com | Email address listed as used for commits associated with the attacker repositories. | |
sapphire679@proton[.]me | Email address listed as used for commits associated with the attacker repositories. | |
sapphire689@proton[.]me | Email address listed as used for commits associated with the attacker repositories. | |
| IPV4 | 154[.]18[.]239[.]209 | SpyGlace C2 server confirmed by JPCERT/CC. |
| IPV4 | 173[.]234[.]11[.]141 | SpyGlace C2 server confirmed by JPCERT/CC. |
| IPV4 | 185[.]18[.]222[.]241 | SpyGlace C2 server confirmed by JPCERT/CC. |
| IPV4 | 213[.]111[.]158[.]200 | SpyGlace C2 server confirmed by JPCERT/CC. |
| IPV4 | 213[.]111[.]158[.]201 | SpyGlace C2 server confirmed by JPCERT/CC. |
| IPV4 | 213[.]111[.]158[.]216 | SpyGlace C2 server confirmed by JPCERT/CC. |
| IPV4 | 31[.]58[.]136[.]207 | SpyGlace C2 server confirmed by JPCERT/CC. |
| SHA256 | 002e1207b96361fc4d53b10621225d61700003241fa38caacb411384b3d51135 | Downloader component: TMI400.db. |
| SHA256 | 0120a6396952aec3f05ec0b0efe25e2a1b73545d55d74a3ac0bcd359d29f52bb | Downloader component: TMI400.db. |
| SHA256 | 0420fd9e5f9961458604909391fb0f1a353c17c986b55fc5722c1b68e41865df | Malicious Downloader2 artifact: item.tmp. |
| SHA256 | 0bda4beded9c2923fe16f20b7cbd7baf1a5b7078be5cde715592529a974f9bd9 | Malicious Downloader2 artifact: Encoded_File.tmp. |
| SHA256 | 0bf85d9065feb20ee946acf77c985cc7ec78de048ee41d8c5931e0e88873efaa | Attack-chain JavaScript artifact: help.js. |
| SHA256 | 119ad3dce05b5ef3db5a76655ac050eac51e318f1f31351ac103693a0a849158 | Malicious Downloader2 artifact: iconcache.dat. |
| SHA256 | 131c27c3dce040979044ac1d363050c5d226af76aef1454bbf87c7193f8fc747 | Downloader component: TMI100.db. |
| SHA256 | 131d8f72fde45c5ca1f662c510c3da16fbcd8ff6ef9b9fd893c25a9c8e8ec205 | Attack-chain JavaScript artifact: index.js. |
| SHA256 | 14d799f7897d25f7cfb4d1c86f43c791b6d778d2efd92b5fac4f65fc472bf501 | Attack-chain JavaScript artifact: basecode.dat. |
| SHA256 | 151b2dc70d141c12a33d8e45a80659fc53a71734e27233326bff150ac87744ea | Attack-delivery RAR archive: 具体的内容.rar. |
| SHA256 | 16bdde15cbf9190883c146bab495c8be73daff4fff5ffbf86b4ee46847103fba | Attack-chain JavaScript artifact: basecode.dat. |
| SHA256 | 18683bba19695d325372d195634afd2f76b14896ba68225ba51ea5a039f2f76d | Downloader component: TMI210.db. |
| SHA256 | 1aaf59f05bb724d501cc9bcd6642ab8fd7347cf274d46c24719c9dced9b22bea | Downloader component: TMI100.db. |
| SHA256 | 1ae423e91f6cd679f9ea5be879b07379633b05cd850c37a8a65cdeaf508d097e | Attack-chain JavaScript artifact: call41.js. |
| SHA256 | 1b25c3d56fdb195b427a9c3bfc1f0e98e77a15322e8d3fc53a18edcc4891847f | Malicious Downloader2 artifact: a101.dat. |
| SHA256 | 21ddfbf726caa6d0f32a6bbce8e619f75c81f884bca48564c7a0e5a84bf4bd39 | Attack-chain JavaScript artifact: help.js. |
| SHA256 | 22de84e8f29cba932cf65cf4dc1d333cb8b2e468204f97030712bee32691ac3b | Downloader component: TMI100.db. |
| SHA256 | 23b37d2ebe683cec3b145b6f2234ee728b99228cf3774399fcfad9502daab9a9 | Downloader component: TMI400.db. |
| SHA256 | 248ded4723e9f5da793e5e42d1ba7c2293dd704718f149b84b3b9b818a1f51db | Malicious loader artifact: sdll2.tmp. |
| SHA256 | 2952d72ad1d44f3d424600b8fa4076794e2e072ab46936012a5fb872c67ce189 | Malicious Downloader2 artifact: item.tmp. |
| SHA256 | 2b650e2e2c46a52378aee70fbaff1ce5e832c759c5f937532047f52500428c4d | Malicious loader artifact: Encoded_File.tmp. |
| SHA256 | 2c98781e39a091b370ebd748b495c45752b2c54cdf2c36814358c8c6bd3ae912 | Attack-chain JavaScript artifact: help.js. |
| SHA256 | 2d8def39b76ca17b419e5084832105c0167a171fdcc14eebd0c872ccb7bf9b0c | Malicious LNK artifact: desk.lnk. |
| SHA256 | 3b7a80fc62eb8b248fd0be0d94c78f1efe2f510499c68865a6d0c4ead6bc4055 | Attack-chain JavaScript artifact: help_v3.js. |
| SHA256 | 3c509ec732979d8c91009d2c9f898bea81f3fc4064c3c56576257f61f9bfaaee | Malicious loader artifact: sdll3.tmp. |
| SHA256 | 3e2bc0bd2eb84282086cc5946673b22414a16e982402f1f05ea57059d2962588 | Downloader component: TMI100.db. |
| SHA256 | 3f2f69a8403e6b4e02ebe65448caf6abb8e2fbd1f7636ec71599f2d2d5fac8fb | Malicious Downloader2 artifact: job.tmp or akdjfiwnkd.tmp. |
| SHA256 | 3f67b777660241a1afc39f2ec388cac933a9eb31b3a34bddd12e39e663f1b566 | SpyGlace v3.1.18 artifact: test2.txt. |
| SHA256 | 43d597783af656a35184021f5e20686896463a1712f9216e0217a2ca740e3935 | Downloader component: TMI100.db. |
| SHA256 | 44a4ac119349f525d877728b53fe38453a516881d577679caf08ab69312a695f | Malicious LNK artifact: ipo6.lnk. |
| SHA256 | 45b2ba7c7a39817e1421f2abe2f869fa16af9651a6c863ac59683268fb391fe6 | Downloader component: TMI210.db. |
| SHA256 | 48bb091e0cab562fe094e0ef6a77b434dba97380c09a707220cbd9ca37999484 | Malicious Downloader1 artifact: iconcache.dat. |
| SHA256 | 50ebf107d522326c9a9db8821fe3263aa5136964faaf5dd183657bbb52725f84 | Downloader component: TMI100.db. |
| SHA256 | 5115277eabf2d22d49dcef1e155874387d8e783853bd86debf7ff58588aae35d | Malicious loader artifact: 0311_2nd_sdll.dat. |
| SHA256 | 5272917261d7091a59e00f9d09cd7eb1d3e111115a5b367f79a66d0d7c7b01f4 | Attack-chain JavaScript artifact: help.js. |
| SHA256 | 555360fb918b959176d669ef0ed40ec0b5ee57005fc625109891a16d02952462 | Downloader component: TMI320.db. |
| SHA256 | 55640ad319208915593db8ad43724dddf6e6e17fc6b0014affa69c90f5cd1eb4 | Malicious loader artifact: sdll3.tmp. |
| SHA256 | 5ab41cf20315d2ea1385967d588159873a65ef5581a0b78de06c0d8617894194 | Attack-chain JavaScript artifact: help_v5.js. |
| SHA256 | 5c3d820e032592f47ffb4850ae0183749199b3e0dca3413cd0c3cb631e322f1b | Malicious LNK artifact: 利権癒着の具体的内容.lnk. |
| SHA256 | 5e97848bebf521766910d9c8378e98bf7aa1ce4b06aeb6c3f86c31ababbe9663 | Malicious Downloader1 artifact: iconcache.dat. |
| SHA256 | 60972abf5425c191c81bae117f1dedaea13d39bc52f367d5dff9ad1aa4b9c5ca | Malicious Downloader1 artifact: iconcache.dat. |
| SHA256 | 62a879b0d1c1649cc72b2b6f61a8f6bd888625ce6e8a7aefe0a0461e4f27c525 | Attack-chain JavaScript artifact: help.dat. |
| SHA256 | 669002654c264191d4660fbf757860d930175649735f81370b9f1af3658a304c | SpyGlace v3.1.17 artifact: test2.txt. |
| SHA256 | 6b84eab2aac7754b99d04365a83ec374e3cea99cc3223118a5f8fd545a8483e5 | Malicious Downloader2 artifact: Cached2014.tmp. |
| SHA256 | 6cdc895eda4847f700d6f82fa2e3a8c72c10da1e16455985df855372142ebbd8 | Malicious loader artifact: test1.txt. |
| SHA256 | 71819a1b856b49e7f194ce60468ed8e5ea925c75d01484f4d28ffcf69d480b36 | Malicious Downloader1 artifact: iconcache.dat. |
| SHA256 | 771a47120b935e218322046e838347d722d265b91f1afdef91194a5bec86a97a | Downloader component: TMI320.db. |
| SHA256 | 78c108be692f1c45ed1da1988e3c5ac792c832a78d0b6e8e6550763156fe8f97 | Attack-chain JavaScript artifact: help.js. |
| SHA256 | 7900c2772680523cadc9fe4e07300d45500191ba64ff5b91573531b133840b14 | Attack-chain JavaScript artifact: close.js. |
| SHA256 | 7aa76237a7686583cc526b9d1a8486a52bd44a448d75ced51e1df4ba29ddb163 | Malicious installation script: msdic.log. |
| SHA256 | 7b297f18ece81e87608e158288cc9c06cb9f4a8f1b2d2256aecf7bba8d7be2ab | Downloader component: TMI400.db. |
| SHA256 | 7c3d0bebd263d3529132f2299de55a7801bf3ff40c833b13838be7a98ea3475e | SpyGlace v3.1.18 artifact: test2.txt. |
| SHA256 | 7d09891e26d56a8bec44c3fe9a5791f3a93e8fa31539951ae6e2c40af83ba42d | Attack-chain JavaScript artifact: test.dat. |
| SHA256 | 8114e3f213713dbbbacafcd0f62884a7826139b434bb3c77eae8dce656477621 | Attack-chain JavaScript artifact: call1.js. |
| SHA256 | 83a22d4f61b054bda53a2ea4f506e97d818c7c961d8cd3975c1f2a51443cf95c | Malicious Downloader1 artifact: iconcache.dat. |
| SHA256 | 843c4dc402e96ed72d7716d980c99e5dfa222a2a322250b7c3755a00d142bc1f | Malicious loader artifact: sdll.tmp. |
| SHA256 | 866564bb455bb3c9f3e15cbbc1dcaf75c533a224eb96c4b6d6739e114ee1d065 | Malicious Downloader1 artifact: iconcache.dat. |
| SHA256 | 86ab5161f761822d16637d4d34b84ca6e1f66cea905aa27510620c9cf5f170d8 | Malicious loader artifact: sDll_jj.dll. |
| SHA256 | 86c49174a032ebbba6aeb1541e2aa84da0933b2eac3976f8705451c13bc7f325 | SpyGlace v3.1.18 artifact: test2.txt. |
| SHA256 | 899ce01e7313f4c1cfcf07cb2456282ded1d6b6c57286762f2914a9d60de0146 | Malicious LNK artifact: idx2.lnk. |
| SHA256 | 8a8cabe5f94e7f4c0ccca97f0c361618ec944df03d8b3bfcfdd76a25dd8f7a5a | Malicious loader artifact: Encoded_File.tmp. |
| SHA256 | 8ba3997afa07ac60312edf5f2d16357d1532a140081d638a9e4653768026ac56 | Malicious loader artifact: Encoded_File2.tmp. |
| SHA256 | 8f08ead23767e1e4389927c40af167122b477ad17a98d388c863342dc9259c5e | Downloader component: TMI400.db. |
| SHA256 | 9394627e9c44cf2226ddf50012e5cf47ccf7d3bd8afa2395c635a93637e23502 | SpyGlace v3.1.15 artifact: sdll.tmp. |
| SHA256 | 94072d60170fc72a528f68b2b3826638dbb7283c8906e8051f53fe16eaf054f8 | Attack-chain JavaScript artifact: close.js. |
| SHA256 | 9706ee93f9b4b8214293e2ca4a68525eccaacfea58b135dcb2ea661a099ee9e6 | Attack-chain JavaScript artifact: help.js. |
| SHA256 | 9789d80077998010c47a6a02ef1241eab11b69d667de8751b1e93fed6df913eb | Downloader component: TMI400.db. |
| SHA256 | 9a19598ea286d5f6fa0b7ff981ba21aff503fb217757f4dfbd496ead01805543 | Malicious loader artifact: sdll.tmp. |
| SHA256 | a18b5a78143f004f33aafad998b518ad9ee4dbdec44817a6e9b570e727d3e22c | Downloader component: TMI400.db. |
| SHA256 | a1f0e6a30dc9753c5cbc80fd9df50eb44aee5a2349223b915b758af746275320 | Attack-chain JavaScript artifact: help.js. |
| SHA256 | a4c8a56070fe6f613e79a14554d0a1dba2f70ce2b93319e72972943cc66edf4a | Malicious Downloader2 artifact: reaconinst.tmp. |
| SHA256 | a7981dfccd8e4bdc00133dc15b22472c1677d6270826863caa36e7d58ef50de0 | Malicious Downloader2 artifact: Encoded_File.tmp or inst.tmp. |
| SHA256 | a8bee6c4a5860b0ae08a984d2a6d62c13d3e91d9514262998924d2e0cef88f7c | Downloader component: TMI400.db. |
| SHA256 | a9287e3452ab09144120ecdd20ed7365de589d5dcad28dcd8e191742d1ce5744 | Attack-chain JavaScript artifact: help_v4.js. |
| SHA256 | a9fd615fce38756ba6de8994f200e4b846397648138a9a0e6ef3b5952ef5e68c | Malicious Downloader2 artifact: newjob.tmp. |
| SHA256 | ab5aba292c983db324987e9fde2e01fe24a979d1587888fcc7460c9489c54ee0 | Attack-chain JavaScript artifact: call2.js. |
| SHA256 | ad1c890f458b94683464c4d6d6d41fe63551c2c06ba2a1b8f71d8acb6ab16de3 | Attack-chain JavaScript artifact: close.js. |
| SHA256 | add013bf7ffc8a89789a7fd0ae0ff799c620af9b2755b214880b6a56768fd48c | SpyGlace v3.1.15 artifact: sdll.tmp. |
| SHA256 | afca3bb9fb8d7a4ab4ceb9707f6d9a17352ccfb8ece83c68b01fbb419818e2fc | Downloader component: TMI100.db. |
| SHA256 | b3f0d48506ff868ba145c9dcad7622bc37b723155648053ce2e2e73d8ea30e93 | SpyGlace v3.1.18 artifact: test2.txt. |
| SHA256 | b5458541732f91793ef89cc58ec5e46d04bf43985ab4e6dc5ad10b6da21581ec | Attack-chain JavaScript artifact: call3.js. |
| SHA256 | c1faaff24d58af798c77d34405379df0a9e883e5bd1100a86d4c3e001414acd8 | Malicious loader artifact: sdll3.tmp. |
| SHA256 | c4768d99445128c670a6f848bc69371872e4d6a2160dbe0073e62ffd786c94ee | Malicious Downloader2 artifact: wincfg.db or Cached.tmp. |
| SHA256 | c86f319f64d25f23ac29d9b53c9764f06a150634ee8e2d836424d460e5a99b52 | SpyGlace v3.1.15 artifact: sdll.tmp. |
| SHA256 | c9295c923da64738b93ff1827a39a5cb8f6c71eab060de416c8175a4a67da524 | SpyGlace v3.1.18 artifact: test2.txt. |
| SHA256 | cc2a6a3b4b771aba341293d2321e5f7b70cf517403fe44a58635b043e8868bdb | Malicious Downloader1 artifact: iconcache.dat. |
| SHA256 | d14214e95c9d1ea850e508dfe27928494f2155a7597e4ea0bad9f70690abb397 | Downloader component: TMI003.db. |
| SHA256 | d567af55c97b7a595fcde5082e37a752718044230c16704e24efb43025bed0c2 | Malicious installation script: msdic.log. |
| SHA256 | deba513e2dc52a2931e61f5ac6d550a7938c1f7f63f661867c09d6141ee98560 | Downloader component: TMI100.db. |
| SHA256 | e5f2c7068ade7b87d24c3b94bc749c351d53609f5fcaa48dce06234beaa2444f | SpyGlace v3.1.15 artifact: Encoded_File.tmp. |
| SHA256 | e6a414a53206e25d061a11e63c7d381ab0eb80cd3d174bd13551e2c36f8b5c04 | Attack-chain JavaScript artifact: call4.js. |
| SHA256 | e8514a2372172b4975f77bf69d5e8b7708cfa60157b064fcab13d7a62a99cc55 | Malicious loader artifact: sdll.tmp. |
| SHA256 | f0af281623b422c1d45e7006d78678762341288c05abcb62648ce55c6b63acb6 | Malicious loader artifact: Encoded_File.tmp or sta.tmp. |
| SHA256 | f50a01ae446adfcaaddffe215abd94b5643211e83d52acf5de540abf9fb26045 | Malicious loader artifact: sdll3.tmp. |
| SHA256 | fa53663bfb80e197483e1a1bf123b94fa869e2d7f42b5fdfbff2869589b65a05 | Malicious Downloader1 artifact: iconcache.dat. |
| SHA256 | fa98deb16bd72f2f77349c8c24de674a007a3d1ec8e88dd590791a57c08ab8f6 | Malicious LNK artifact: information.lnk. |
| SHA256 | fd0c7713520bd19c3e2566e93696532aa7da39a0c5ce1a797b67ce777b56d395 | Malicious LNK artifact: desk.lnk. |
| SHA256 | ffe5853d19be1acfe12bd681c7390d8fa88534a471020e6866a9e7c37d01fea2 | Attack-chain JavaScript artifact: close.js. |
| URL | hxxps[:]//c[.]statcounter[.]com/13178005/0/7f3c2735/1/ | Specific legitimate-service resource listed as attacker-used infrastructure. |
| URL | hxxps[:]//cdn[.]jsdelivr[.]net/gh/mei1990789/class125/ | Specific jsDelivr resource listed as attacker-used infrastructure in the payload retrieval chain. |
| URL | hxxps[:]//codeberg[.]org/Hamilton385673/eff88e889w33456 | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//codeberg[.]org/meca922199/ertlokefgpokjper2359 | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//codeberg[.]org/ochi_ma992/3tv9239irfn83 | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/bohihef411/tuikfwoveb | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/cafes39636/ngwtaepesf | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/cefobe3574/kojyyvtkqo | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/fehijow850/uywcrcvlnb | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/gixop88415/glfhvhtzih | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/hexif45133/yedkatinrc | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/jewexo9791/archibkyof | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/kapap40675/fpqtzyofdl | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/lowege1212/izrtysherg | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/mei1990789/class125 | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/rapefo2905/rncprjmauw | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/sapphire679/tblsesarol/ | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/sapphire689/dnaluakxit | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/vogenoc114/qlofnsayvl | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/wanib11399/zjeqopmfit | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/waxiyes819/dymcdbqqen | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/williams250666/bluenote554 | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//github[.]com/yefixi3890/krbgqbmlho | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//gitlab[.]com/cafes39636/ngwtaepesf | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//gitlab[.]com/kapap40675/fpqtzyofdl | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//gitlab[.]com/lowege1212/eboralfotj | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//gitlab[.]com/rapefo2905/yedkatinrc | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//gitlab[.]com/sapphire689/dnaluakxit | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//gitlab[.]com/vogenoc114/qlofnsayvl | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//gitlab[.]com/waxiyes819/dymcdbqqen | Attacker management repository identified by JPCERT/CC. |
| URL | hxxps[:]//gitlab[.]com/yefixi3890/krbgqbmlho | Attacker management repository identified by JPCERT/CC. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe JavaScript embedded in the malicious LNK file was obfuscated.T1059.007 · JavaScriptEmbedded JavaScript downloaded and processed files used in the subsequent infection chain.T1105 · Ingress Tool TransferThe infection chain downloaded files from jsDelivr and retrieved additional downloaders, loaders, and SpyGlace through abused legitimate services.T1140 · Deobfuscate/Decode Files or InformationThe embedded JavaScript decoded and extracted the downloaded contributing[1].txt file.T1204.002 · Malicious FileThe infection process began when the victim opened an LNK file extracted from the downloaded RAR archive.T1218.005 · MshtaThe malicious LNK file invoked mshta.exe to execute JavaScript embedded within the LNK file.T1566.001 · Spearphishing AttachmentJPCERT/CC also confirmed a similar case with the malicious file attached directly to the email.T1566.002 · Spearphishing LinkSpear-phishing emails contained Proton Drive links leading victims to download RAR archives containing malicious LNK files.
People
Threat Actors
Malware
Products
CodebergGitHub and Bitbucket were used. However, in the 2026 attacks, we confirmed that GitLab, jsDelivr, and Codeberg, in addition to GitHub, were abused as attack infrastructure.GitHubby combining .db files located in the extracted folder. The downloader accesses legitimate sites such as GitHub, downloads additional downloaders and loaders, and executes them.GitLabIn the 2025 attacks, GitHub and Bitbucket were used. However, in the 2026 attacks, we confirmed that GitLab, jsDelivr, and Codeberg, in addition to GitHub, were abused as attack infrastructure.jsDelivrDownloads the file contributing[1].txt from jsDelivrMicrosoft WindowsThis allows the threat actor to use a legitimate Windows program while carrying out processes that lead to the retrieval and execution of subsequent payloads.Proton DriveFigure 1 shows the overall attack flow. In the case we observed, the spear-phishing email contained a Proton Drive link, which was used to lure the victim into downloading a RAR file from Proton Drive. When the RAR file