Conti Keeps Posting Victims Despite Offline Panels, DarkOwl Says
Summary
DarkOwl reported that Conti’s administrative and negotiation panels went offline, but its victim blog remained active. The group announced 24 new victims since May 19, leaving claims that it had shut down unsubstantiated.
Key points
- Conti’s administrative panel and negotiation service went offline in late May, prompting reports that the ransomware group had shut down.
- DarkOwl said Conti’s victim blog continued operating, with a brief decline in victim announcements between May 12 and 20.
- As of publication, DarkOwl said Conti had announced 24 new victims since May 19 and had made no known official statement that its operations were interrupted.
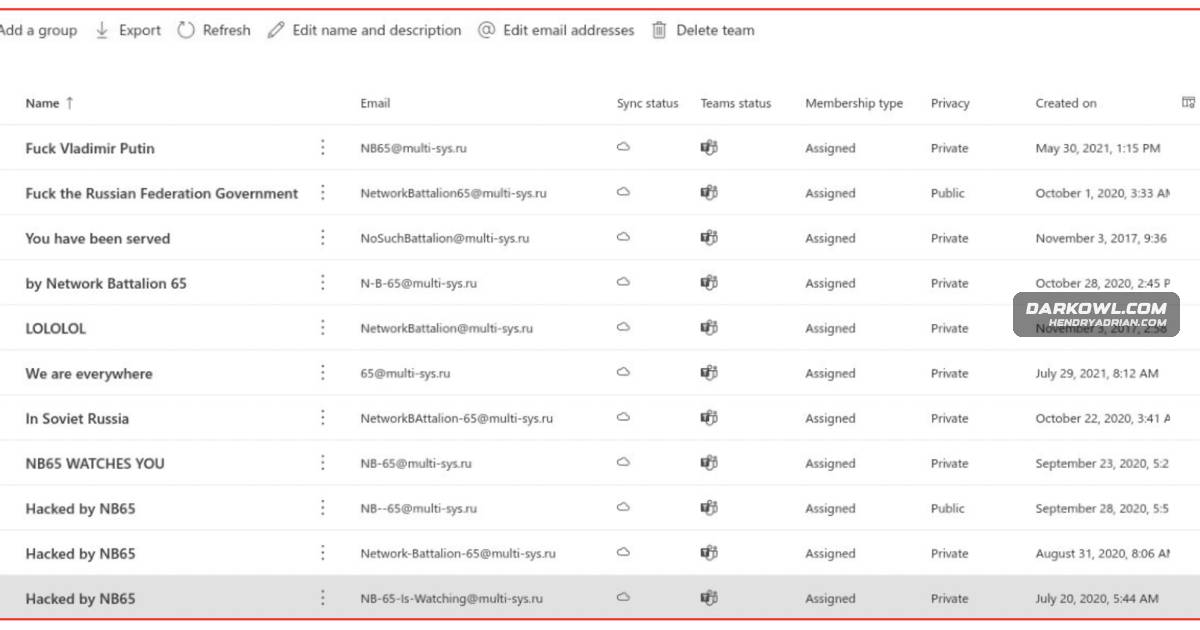
- The article describes Conti’s ransomware source code and internal materials being leaked after the group voiced support for Russia; it says NB65 later used modified leaked code in attacks on Russian targets.
- DarkOwl reported that NB65 claimed to have encrypted networks and exfiltrated more than 350 GB from Russian IT and managed-service providers.
- The article presents reorganization, rebranding, darknet disputes, public backlash, and possible covert law-enforcement activity as potential explanations—not confirmed causes—for the disruption.
- DarkOwl cautioned that a shutdown or rebrand would not necessarily end the threat, citing the history of ransomware groups resurfacing under new names.
Article Details
- Event Type
- Reported Conti infrastructure outages and possible reorganization amid continued ransomware activity
- Impact
- Conti’s negotiation service and administrative panel were reported offline, but its victim blog remained active and the article says Conti announced 24 new victims since May 19. The article describes ransomware attacks affecting Costa Rican government agencies and attacks against Russian organizations using leaked Conti source code. Leaks of Conti’s source code and internal data, and related disclosures involving Trickbot, exposed operational information and damaged the groups’ reputations. Whether Conti had shut down, was changing infrastructure, or was reorganizing remained uncertain.
Threat Actors
AlphaVName used in the article’s parenthetical reference to Blackcat (a.k.a. AlphaV, alfa).Arvin ClubGroup reported to have hacked and leaked STORMOUS’s Tor v3 web service.AvosLockerRansomware group the article says may be directly or indirectly linked to Conti; described as active in recent weeks.BlackByteRansomware group the article says may be directly or indirectly linked to Conti.BlackCatRansomware group identified in a now-removed Conti victim-site post as involved in a dispute with Conti; the post also uses the name AlphaV and the spelling alfa.ContiRansomware group described as attacking victims, leaking stolen data, and continuing to announce victims despite reports of infrastructure outages.DarkSideRansomware group described as going offline after hacking Colonial Pipeline and later resurfacing under new names.HiveRansomware group the article says may be directly or indirectly linked to Conti; described as compromising at least 30 servers in Costa Rica.KarakurtRansomware group the article says may be directly or indirectly linked to Conti.LockBitRansomware group discussed in a dispute with Conti; a representative reportedly invited Conti employees to discuss cooperation.Network Battalion (nb65)Group described as deploying leaked Conti ransomware source code, modified with a different cipher, in attacks against targets in Russia.REvilRansomware group described as having shut down after its attack on Kaseya and later returned, according to analysts cited in the article.StormousRansomware group described as targeting Coca Cola and later suspending operations.Trickbot GroupGroup described as having a strong operational partnership with Conti; members’ information and internal data were leaked.
Malware
Countries
Costa RicaCosta Rica declared a state of national emergency May 8th due a widespread ransomware attack carried out by Conti.ItalyThis includes victims from the transportation sector in Europe, such as a popular airline in the UK, a car dealership chain in Norway, and a mega-yacht supplier in Italy.NorwayThis includes victims from the transportation sector in Europe, such as a popular airline in the UK, a car dealership chain in Norway, and a mega-yacht supplier in Italy.RussiaAt the beginning of the war in Ukraine, Conti was one of the first ransomware groups to publicly announce their support of Russia.UkraineAt the beginning of the war in Ukraine, Conti was one of the first ransomware groups to publicly announce their support of Russia.United KingdomThis includes victims from the transportation sector in Europe, such as a popular airline in the UK, a car dealership chain in Norway, and a mega-yacht supplier in Italy.
Industries
GovernmentThe cyber attack started with the Ministry of Finance, and eventually spread to other Costa Rican government agencies including the tax systems.TransportationThis includes victims from the transportation sector in Europe, such as a popular airline in the UK, a car dealership chain in Norway, and a mega-yacht supplier in Italy.