
Censys Finds 1,465 Exposed ARTEX Consoles Amid Reports of Malicious Use
Summary
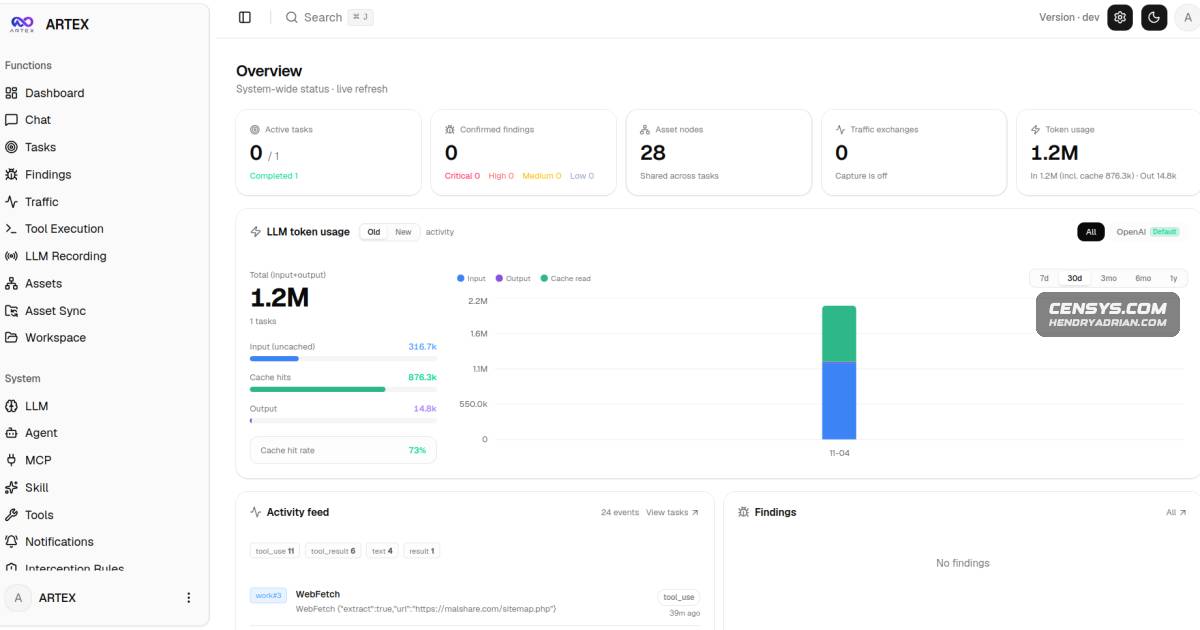
Censys counted 1,465 exposed ARTEX consoles and found open directories exposing post-exploitation tools. The report examines reported ARTEX use in campaigns targeting South Korean finance and ConnectWise customers, and offers host-level hunting pivots.
Key points
- ARTEX is an open-source, LLM-driven autonomous penetration-testing framework released in July 2026; it integrates asset discovery from ScopeSentry.
- Censys observed 1,465 exposed ARTEX hosts as of November 4, 2026. About 650 appeared to share two hosting templates, leaving roughly 815 distinct-looking deployments.
- CrowdStrike reported that an unattributed actor used ARTEX against South Korean financial organizations, and assessed with moderate confidence that the actor was a financially motivated Chinese speaker.
- Microsoft attributed the ConnectWise Cloud Backup supply-chain compromise to Storm-0940 and said the group used ARTEX for scanning, password spraying, and OAuth application abuse across more than 2,250 tenants.
- Censys found 32 open directories on ARTEX hosts, exposing items including post-exploitation kits, stagers, implants, exploit binaries, and operator files.
- Censys found other threat detections on 155 ARTEX hosts, including AI attack frameworks, C2 tools, and LLM gateway or reseller software; it recommends investigating co-located services and scan history.
Article Details
- Attack Vectors
- ARTEX was used to automate reconnaissance and scanning.
- Microsoft reported that Storm-0940 used ARTEX for password spraying and OAuth application abuse in activity linked to the ConnectWise Cloud Backup supply-chain compromise.
- CrowdStrike reported that an unattributed actor used ARTEX to target South Korean financial institutions and exfiltrate data.
- Defensive Notes
- ARTEX consoles do not need to be publicly accessible; identify and restrict exposed consoles, including those on the default port 8787 and commonly observed ports 8790 and 443.
- Check for open directories on ARTEX hosts that may expose configuration files, prompts, session histories, exploit binaries, stagers, or implants.
- Investigate co-located Vshell or FRP listeners and unfamiliar LLM proxy or reseller software, including CLIProxyAPI and New API.
- Review scan history for mitmproxy banners and short-lived Python SimpleHTTP servers on high ports.
- Review the reported CrowdStrike and Microsoft infrastructure indicators and assess potentially exposed systems for unauthorized access or data exfiltration.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 101[.]53[.]80[.]20 | Proxy infrastructure identified in the indicators reported by CrowdStrike. |
| IPV4 | 103[.]248[.]148[.]84 | Proxy infrastructure identified in the indicators reported by CrowdStrike. |
| IPV4 | 124[.]155[.]252[.]63 | Proxy infrastructure identified in the indicators reported by CrowdStrike. |
| IPV4 | 144[.]172[.]64[.]128 | Storm-0940 infrastructure identified by Microsoft. |
| IPV4 | 144[.]172[.]64[.]60 | Storm-0940 infrastructure identified by Microsoft. |
| IPV4 | 144[.]172[.]64[.]99 | Storm-0940 infrastructure identified by Microsoft. |
| IPV4 | 154[.]201[.]79[.]246 | Proxy infrastructure identified in the indicators reported by CrowdStrike. |
| IPV4 | 203[.]160[.]133[.]172 | Proxy infrastructure identified in the indicators reported by CrowdStrike. |
| IPV4 | 205[.]214[.]59[.]31 | Proxy infrastructure identified in the indicators reported by CrowdStrike. |
| IPV4 | 209[.]209[.]85[.]38 | Proxy infrastructure identified in the indicators reported by CrowdStrike. |
| IPV4 | 23[.]158[.]220[.]98 | Proxy infrastructure identified in the indicators reported by CrowdStrike. |
| IPV4 | 23[.]248[.]249[.]90 | Proxy infrastructure identified in the indicators reported by CrowdStrike. |
| IPV4 | 38[.]244[.]50[.]120 | ARTEX host and exposed open directory used by the actor in CrowdStrike's report. |
MITRE ATT&CK
T1110.003 · Password SprayingMicrosoft reported that Storm-0940 used ARTEX for password spraying against ConnectWise customer tenants.T1195.002 · Compromise Software Supply ChainMicrosoft attributed the ConnectWise Cloud Backup supply-chain compromise to Storm-0940.T1595 · Active ScanningARTEX was used to automate scanning and reconnaissance.
People
Threat Actors
Vendors
Products
ARTEXARTEX is an open-source, LLM-driven autonomous penetration testing framework released in July 2026.ConnectWise Cloud BackupMicrosoft attributed the ConnectWise Cloud Backup supply-chain compromise to Storm-0940, a China state-aligned actor active since 2021.DeepSeek v4.1-flashARTEX ran on 38.244.50[.]120 with DeepSeek v4.1-flash as its main model, which the actor likely bought through an API reseller.ScopeSentryIts developer, Autumn-27, is also the author of ScopeSentry, a widely used Chinese asset-discovery and vulnerability-scanning platform with more than 2,000 GitHub stars.
Tools
Adaptix C2These include other AI attack frameworks, recon platforms, tunneling tools, and C2: Vshell, Cobalt Strike, and Adaptix C2.ARTEXARTEX is an open-source, LLM-driven autonomous penetration testing framework released in July 2026.CLIProxyAPI43 ARTEX hosts also run self-hosted LLM gateway or reseller software, mainly CLIProxyAPI (19) and New API (18).Cobalt StrikeThese include other AI attack frameworks, recon platforms, tunneling tools, and C2: Vshell, Cobalt Strike, and Adaptix C2.CyberStrikeAI108.165.147[.]226:8299 Three beacon_linux_amd64 implant builds and reverse-shell scripts, on a host that also runs FRP and CyberStrikeAIFRP108.165.147[.]226:8299 Three beacon_linux_amd64 implant builds and reverse-shell scripts, on a host that also runs FRP and CyberStrikeAIHexStrike AICyberStrikeAI shares hosts with ARTEX on 70 hosts, and PentAGI, HexStrike AI, and RedAmon also appear.mitmproxyIt also includes mitmproxy for traffic recording, and it works with Anthropic, OpenAI, or any OpenAI-compatible model endpoint.New API43 ARTEX hosts also run self-hosted LLM gateway or reseller software, mainly CLIProxyAPI (19) and New API (18).NmapWorker agents claim those intents, run tools (e.g., nmap, which ships in the Docker image), and write results back.PentAGICyberStrikeAI shares hosts with ARTEX on 70 hosts, and PentAGI, HexStrike AI, and RedAmon also appear.RedAmonCyberStrikeAI shares hosts with ARTEX on 70 hosts, and PentAGI, HexStrike AI, and RedAmon also appear.ScopeSentryIts developer, Autumn-27, is also the author of ScopeSentry, a widely used Chinese asset-discovery and vulnerability-scanning platform with more than 2,000 GitHub stars.VShellThese include other AI attack frameworks, recon platforms, tunneling tools, and C2: Vshell, Cobalt Strike, and Adaptix C2.