RemControl Android Malware Targets Banking Users in Europe, Canada and the Middle East
Summary
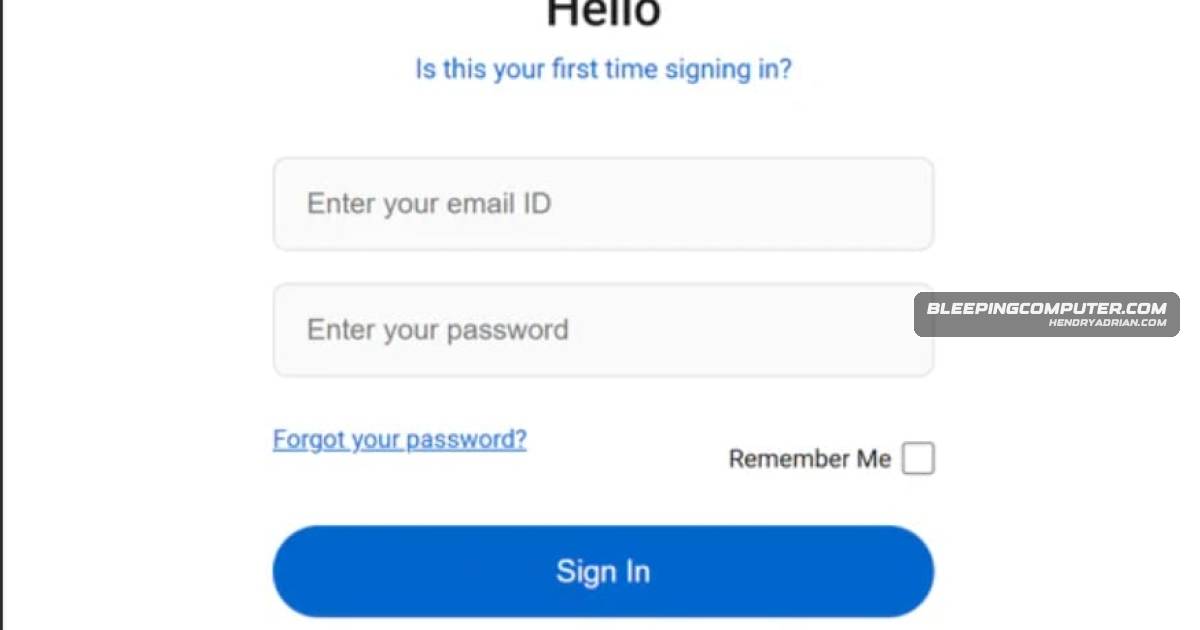
Group-IB reports that RemControl, an Android malware-as-a-service platform, is distributed through malvertising and fake TVTap pages. It uses phishing overlays to steal banking credentials and a VPN service to block Google Play checks.
Key points
- RemControl is distributed through malvertising and fake Google Play pages impersonating the TVTap IPTV app; some campaigns use geofencing and mobile User-Agent checks.
- Group-IB says the malware targets users in parts of Europe, Canada and the Middle East. Its infrastructure has been active since at least May, and researchers first observed samples in July.
- The malware uses more than 30 phishing overlays to steal banking credentials and can receive new targets from its command-and-control infrastructure.
- During installation, RemControl requests Accessibility Service permissions. If granted, it can capture user input and screen data, remotely control the device, and resist removal.
- A VPN service started by the dropper blocks Google Play services traffic, preventing Play Protect from performing real-time checks, according to the report.
- RemControl retrieves encrypted C2 information from Telegram channels. Group-IB tracks the operator as UNKK and suspects a connection to the Medusa banking trojan; the actor’s origin remains unclear.
- The article advises Android users to avoid untrusted APK downloads, run Play Protect scans, and deny Accessibility Service permissions to apps that do not need them.
Article Details
- Event Type
- Android banking malware-as-a-service campaign distributed through malvertising and fake Google Play pages impersonating TVTap IPTV.
- Impact
- RemControl uses more than 30 phishing overlays to steal banking credentials and can capture user input, stream screenshots and accessibility data, and remotely control devices. Group-IB reports targeting in Europe, Canada, and the Middle East; the source does not quantify victim numbers or financial losses.
Threat Actors
Malware
MedusaResearchers linked the operator to UNKK and suspect a connection to Medusa.RemControlRemControl is a new Android malware-as-a-service platform spread through malvertising and fake Google Play pages impersonating the TVTap IPTV app, with phishing overlays aimed at stealing banking credentials.ToxicPanda#RemControl
Products
AndroidRemControl is a new Android malware-as-a-service platform spread through malvertising and fake Google Play pages impersonating the TVTap IPTV app, with phishing overlays aimed at stealing banking credentials.Google PlayRemControl is a new Android malware-as-a-service platform spread through malvertising and fake Google Play pages impersonating the TVTap IPTV app, with phishing overlays aimed at stealing banking credentials.Play ProtectWhen launched, the dropper starts a VPN service that blocks traffic from Google Play services, preventing Play Protect from performing real-time checks against known malware.TVTapRemControl is a new Android malware-as-a-service platform spread through malvertising and fake Google Play pages impersonating the TVTap IPTV app, with phishing overlays aimed at stealing banking credentials.
Countries
CanadaGroup-IB says it targets users across Europe, Canada, and the Middle East, uses a VPN trick to block Google Play protections, and may have been built with AI assistance.FranceResearchers at cybersecurity company Group-IB say that the malware targets users in Europe (Italy, France, Spain, Poland, Portugal), Canada, and countries in the Middle East.ItalyResearchers at cybersecurity company Group-IB say that the malware targets users in Europe (Italy, France, Spain, Poland, Portugal), Canada, and countries in the Middle East.PolandResearchers at cybersecurity company Group-IB say that the malware targets users in Europe (Italy, France, Spain, Poland, Portugal), Canada, and countries in the Middle East.PortugalResearchers at cybersecurity company Group-IB say that the malware targets users in Europe (Italy, France, Spain, Poland, Portugal), Canada, and countries in the Middle East.SpainResearchers at cybersecurity company Group-IB say that the malware targets users in Europe (Italy, France, Spain, Poland, Portugal), Canada, and countries in the Middle East.