MacSync Malware Uses Public iCloud Calendars to Deliver Payloads and Install a macOS Backdoor
Summary
Kaspersky says a new MacSync variant hides downloader commands in public iCloud calendar events and adds an Objective-C backdoor that can run AppleScript, steal data, and persist on macOS systems.
Key points
- MacSync is a Swift-based information stealer first observed in April 2025; delivery methods include ClickFix lures and fake or cracked software.
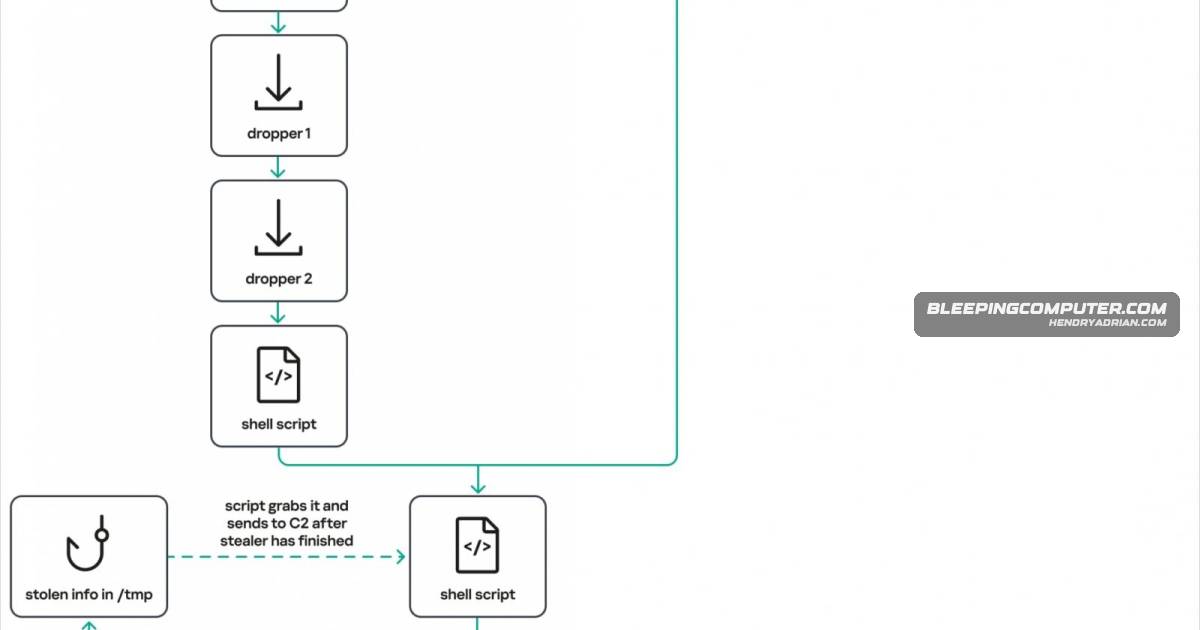
- In one campaign, a downloader retrieves commands hidden after the DESCRIPTION: line in a public iCloud calendar event, then fetches a malware archive from iCloud.
- The stealer targets browser data, crypto wallets, Telegram, Keychain, SSH, AWS, Kubernetes, Git, and system information.
- A new Objective-C backdoor disguises itself as Finder and uses a LaunchAgent, .zshrc changes, and global Git hooks for persistence.
- The backdoor can run attacker-supplied AppleScript, deploy a browser extension or replace a Ledger app, and collect and upload files and system information.
- Kaspersky could not determine the purpose of the backdoor's live_browser command, which downloads and executes a component called sn_relay.
Article Details
- Event Type
- MacSync malware campaign using public iCloud calendar events to deliver payloads and a new backdoor module
- Impact
- The malware steals browser, cryptocurrency wallet, Telegram, Keychain, SSH, AWS, Kubernetes, Git, and system data. Its new Objective-C backdoor can run attacker-supplied AppleScript, deploy browser extensions or replace a Ledger wallet app, collect and upload files, and establish persistence. The article reports delivery through ClickFix lures and fake software, with commands and a next-stage payload delivered via public iCloud calendar events.
MITRE ATT&CK
T1005 · Data from Local SystemThe malware collects system information and files from infected systems.T1041 · Exfiltration Over C2 ChannelThe backdoor uploads collected information and files to its command-and-control server.T1059.002 · AppleScriptThe backdoor runs attacker-supplied AppleScript received from its command-and-control server.T1543.001 · Launch AgentThe installer establishes persistence through a LaunchAgent.T1546.004 · Unix Shell Configuration ModificationThe installer modifies .zshrc to establish persistence.
Malware
Products
iCloudA new MacSync variant is targeting macOS users by hiding its payload delivery in public iCloud calendar events, adding a more evasive infection chain.LedgerDeploy a browser extension or replace an installed Ledger wallet app with versions supplied by the command-and-control (C2) server.macOSA new MacSync variant is targeting macOS users by hiding its payload delivery in public iCloud calendar events, adding a more evasive infection chain.