Compromised GitHub Actions Reactivated Mini Shai-Hulud Malware Payloads
Summary
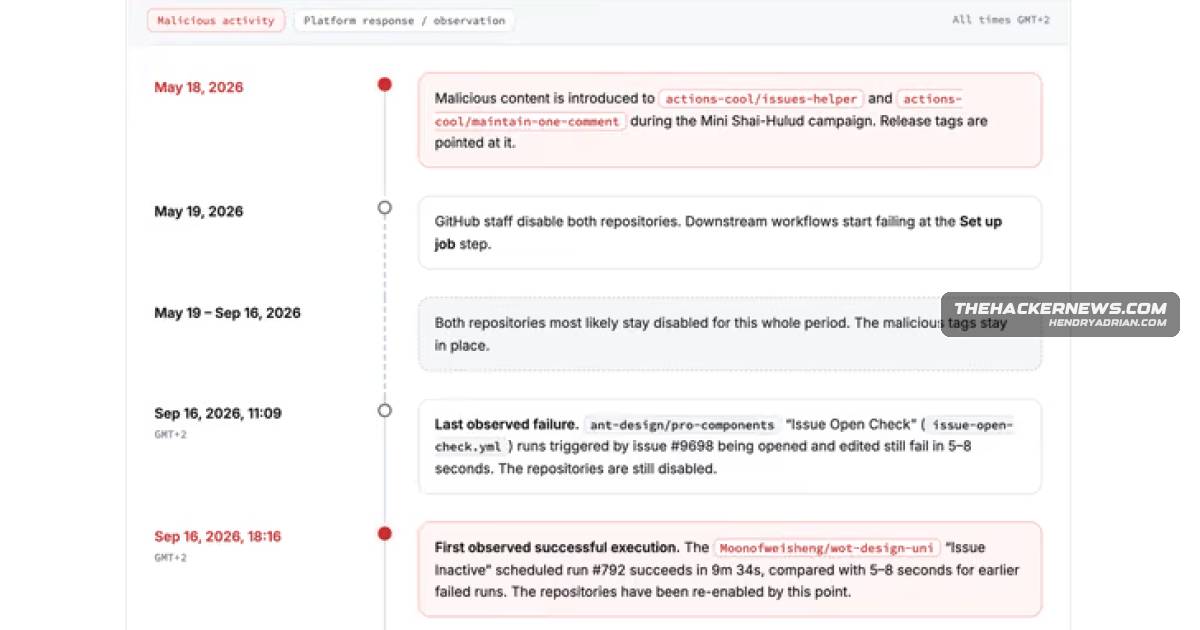
Two actions-cool GitHub Actions became accessible again with malicious tags still in place, potentially resuming payload delivery. Developers are advised to remove the actions, pin clean commit SHAs, rotate secrets, and review workflow history.
Key points
- The two actions-cool repositories became accessible on September 16, 2026, before GitHub disabled them again.
- Release tags still pointed to malicious code introduced during the May 18 compromise, so workflows using those tags could resume downloading and executing the payload.
- The original payload harvested CI/CD credentials and exfiltrated them to an attacker-controlled server.
- Socket linked the activity to the Mini Shai-Hulud cluster, citing shared infrastructure including t.m-kosche[.]com.
- Workflows pinned to a full commit SHA from before May 18, 2026, were not affected by the tag reactivation.
- Recommended steps include removing affected actions, switching to a known-clean SHA, rotating exposed secrets, and reviewing workflow runs and repository history.
Article Details
- Event Type
- Supply-chain security incident involving compromised GitHub Actions that were re-enabled with malicious code still present.
- Impact
- Workflows referencing the affected actions by mutable version tags resumed downloading and executing credential-harvesting payloads, which exfiltrated CI/CD secrets to an attacker-controlled server. Workflows pinned to a clean pre-compromise commit SHA were not affected. The repositories were disabled again; the article says the reason for their re-enablement is unknown.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | t[.]m-kosche[.]com | Exfiltration domain cited as shared infrastructure linking the compromised GitHub Actions to the Mini Shai-Hulud activity cluster. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelThe stolen credential details were exfiltrated to an attacker-controlled server.T1195.002 · Compromise Software Supply ChainCompromised GitHub Actions delivered malicious code through software supply-chain workflows.T1552 · Unsecured CredentialsThe malicious code harvested sensitive credentials from CI/CD pipelines.