
Reports: Malicious Agent Framework PyPI Releases Steal Cloud Credentials
Summary
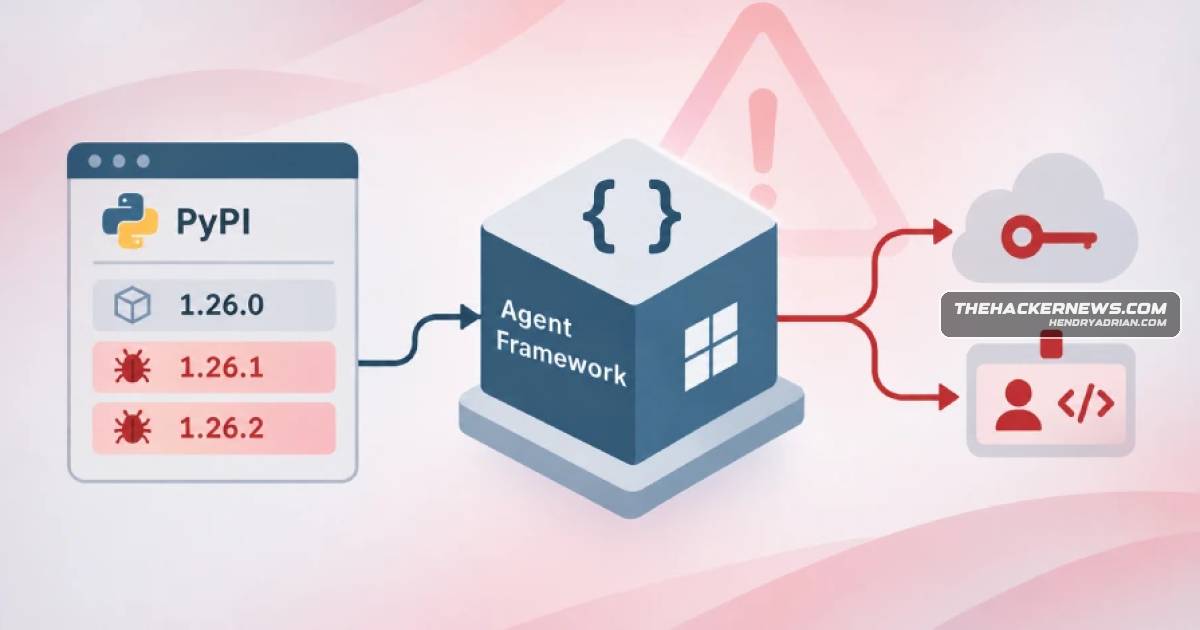
Multiple security firms report that PyPI versions 1.26.1 and 1.26.2 of Microsoft's agent-framework install startup hooks to steal credentials and cloud tokens. Both releases have been quarantined; the publishing-access route is unclear.
Key points
- Reports from multiple security firms say versions 1.26.1 and 1.26.2 were published on November 17, 2026, 33 minutes apart.
- The releases install a .pth file that runs the stealer whenever Python starts in an affected environment, even if the package is not imported.
- The malware reportedly collects stored credentials, environment data, cloud identity tokens and instance metadata, then sends compressed data to a webhook[.]site endpoint.
- Version 1.26.2 reportedly adds GitHub Actions OIDC token collection and expands searches for credential-related environment variables.
- Both malicious releases have been quarantined on PyPI; how the attacker obtained publishing access remains unclear.
- The article says the package attracts about 190,000 downloads per month.
Article Details
- Event Type
- Supply-chain compromise of Microsoft's agent-framework package on PyPI.
- Impact
- Versions 1.26.1 and 1.26.2 install Python startup hooks that run the credential stealer on every interpreter start. Reports say it collects credentials, environment data, cloud identity tokens, and instance metadata, then exfiltrates the collected information. Both versions had been quarantined on PyPI at the time of reporting; how the attacker obtained publishing access was unclear.
Threat Actors
Malware
Vendors
Products
Azure"In an Azure DevOps pipeline, SYSTEM_ACCESSTOKEN and SYSTEM_OIDCREQUESTURI are enough to request a federated token for api://AzureADTokenExchange. On Azure compute, it asks the managed identity endpoint for an accessAzure DevOps"In an Azure DevOps pipeline, SYSTEM_ACCESSTOKEN and SYSTEM_OIDCREQUESTURI are enough to request a federated token for api://AzureADTokenExchange. On Azure compute, it asks the managed identity endpoint for an accessDurableTaskthis year. In May 2026, the threat actors behind TeamPCP pushed three malicious versions of durabletask, Microsoft's Python client for the Durable Task workflow execution framework, to distribute the MiniGitHub ActionsVersion 1.26.2, on the other hand, imports a new top-level module, af_runtime_diag.py, collects GitHub Actions OIDC tokens, and expands the search patterns used for harvesting credential-related environment variables.Microsoft Agent FrameworkAgent-framework is the meta-package for Microsoft Agent Framework, an open-source framework for building and orchestrating artificial intelligence (AI) agents using Python.