Underground Malware Operation Drains About $100,000 in Cryptocurrency
Summary
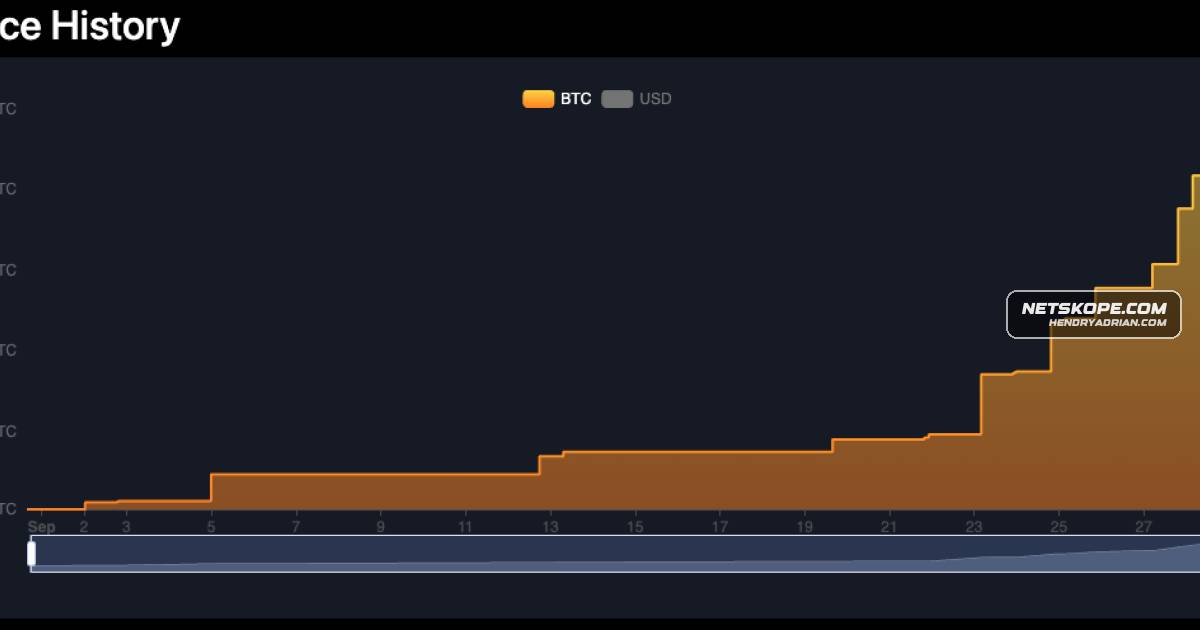
Netskope researchers detail a Windows malware operation that injects a Vidar-class stealer into browsers to drain exchange accounts and replace copied wallet addresses. They estimate about $100,000 in proceeds and at least 350–430 paying victims.
Key points
- Aotera/Tedy loader builds deliver a Vidar-class stealer into a suspended dllhost.exe process; the injected process launches Chrome or Edge under the victim’s profile.
- The malware injects scripts into logged-in browser sessions to drain exchange accounts, including disabling Binance withdrawal allow lists, converting funds to Bitcoin, and withdrawing them to operator-controlled addresses.
- A clipboard clipper replaces copied cryptocurrency wallet addresses with the operator’s addresses; the configuration covers more than 80 destinations across roughly two dozen chains.
- Netskope estimates at least $100,000 in on-chain proceeds and 350–430 paying victims; the victim count excludes exchange-account drains and is therefore likely higher.
- The campaign uses rotating, Cloudflare-fronted gates and disguises withdrawal confirmation emails in webmail. Researchers did not attribute it to a named actor.
- Blocking a gate does not remove the implant. Netskope recommends investigating endpoints for the loader’s process behavior and artifacts, and hunting for browser requests to /api/machine/* across any domain.
- Netskope reports detections for the gate URI pattern, malicious gate domains, and loader binaries; it also disclosed live gate domains to Cloudflare.
Article Details
- Attack Vectors
- Versioned 7z or zip lure archives contain setup.exe, a trojanized msys-crypto-3.dll, and encrypted data.bin. How the archives reach victims is unknown.
- The Underground loader decrypts an embedded stage and injects it into a suspended dllhost.exe process. That process launches Chrome or Edge under the victim’s existing browser profile.
- The injected stealer obtains browser-injection scripts from a rotating gate and runs them in authenticated exchange and webmail sessions.
- In a logged-in Binance session, an injected script displays a fake security-verification overlay while disabling the withdrawal allow list, converting balances, and withdrawing funds to operator addresses.
- A clipboard clipper replaces copied cryptocurrency wallet addresses with operator addresses. Webmail injections alter how withdrawal-confirmation messages appear in the victim’s browser.
- Defensive Notes
- Treat contact with a blocked gate as evidence of an active infection: blocking traffic does not remove the implant, and infected machines may continue polling.
- Hunt for injection into dllhost.exe, Chrome or Edge launched by dllhost.exe, activity in C:\ProgramData\Underground\, and PNG-named artifacts in AppData\Local. The malware may delete the Underground folder after use.
- Use behavioral detection for chrome.exe or msedge.exe requests to /api/machine/* alongside domain reputation, because the operator rotates gate domains.
- Verify exchange withdrawals through a separate channel; the payload can alter confirmation emails displayed in webmail.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | easybooters[.]com | Operator C2 log domain used to report account-drain steps. |
| DOMAIN | quick-neo[.]com | Example of a hardcoded gate used by the stealer. |
| DOMAIN | slow-sky[.]com | Tracked gate domain that was serving the injection configuration during the investigation. |
| DOMAIN | true-lie[.]com | Tracked rotating gate domain. |
| IPV4 | 95[.]164[.]53[.]76 | Underground loader telemetry-panel address. |
| URL | hxxp[:]//95[.]164[.]53[.]76/new/log/048466C5/startCrypt | Recorded loader telemetry URL for the startCrypt stage. |
| URL | hxxp[:]//95[.]164[.]53[.]76/new/log/29A5FDA7/failed/1769331221 | Recorded loader telemetry URL for a failed stage. |
| URL | hxxp[:]//95[.]164[.]53[.]76/new/log/29A5FDA7/startLoader/1769331211 | Recorded loader telemetry URL for the startLoader stage. |
| URL | hxxp[:]//95[.]164[.]53[.]76/new/log/8320e1a4/startloader/1767499038 | Recorded loader telemetry URL for the startloader stage. |
| URL | hxxp[:]//95[.]164[.]53[.]76/new/log/8320E1A4/success/1767499039 | Recorded loader telemetry URL for a success stage. |
| URL | hxxp[:]//95[.]164[.]53[.]76/new/log/D9D278DD/success/1696492954 | Recorded loader telemetry URL for a success stage. |
| URL | hxxps[:]//easybooters[.]com/newlog[.]php | Configured operator log endpoint for reporting account-drain steps. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe loader carries an encrypted stage, and the gate serves obfuscated browser-injection scripts.T1055 · Process InjectionThe loader uses section-based injection to place a self-decrypting payload into a suspended dllhost.exe process.T1057 · Process DiscoveryThe loader examines running processes to find names on its hard-coded anti-analysis list.T1070.004 · File DeletionA second dllhost.exe process deletes the Underground folder after use.T1071.001 · Web ProtocolsInfected machines poll web-based /api/machine/* gate paths for commands and injection configuration.T1113 · Screen CaptureThe Vidar-class payload collects screenshots.T1115 · Clipboard DataThe clipper checks copied wallet addresses against address patterns and substitutes operator addresses.T1140 · Deobfuscate/Decode Files or InformationThe loader decrypts an embedded stage using per-build AES keys.T1185 · Browser Session HijackingThe stealer injects scripts into pages opened in the victim’s authenticated Chrome or Edge sessions.T1497.001 · System ChecksBefore injection, the loader checks running processes against names associated with debuggers, monitors, and virtual-machine or sandbox agents.T1539 · Steal Web Session CookieThe payload collects browser cookies and stages stolen cookies under C:\ProgramData\Underground\.T1555.003 · Credentials from Web BrowsersThe Vidar-class payload collects Chromium and Gecko browser passwords.T1657 · Financial TheftInjected scripts drain authenticated exchange accounts, while the clipper diverts cryptocurrency transfers to operator addresses.
Malware
Aotera/TedyAn Aotera/Tedy loader injects a Vidar-class stealer into a Windows process, which then launches Chrome or Edge and injects its scripts into the pages the victim opens.UndergroundWe refer to the builder as Underground, after the folder its loader logs to (C:\ProgramData\Underground\).VidarAn Aotera/Tedy loader injects a Vidar-class stealer into a Windows process, which then launches Chrome or Edge and injects its scripts into the pages the victim opens.
Vendors
BinanceWithin a logged-in Binance session, the injected script renders a fake security-verification dialog as an in-page overlay drawn over the page content, rather than as a separate window, and styles it to mimic Binance’sCloudflareThe gate is an nginx/FastCGI origin behind Cloudflare.NetskopeNetskope Threat Labs analyzed a crypto-stealing operation that drains victims’ cryptocurrency exchange accounts.
Products
BinanceWithin a logged-in Binance session, the injected script renders a fake security-verification dialog as an in-page overlay drawn over the page content, rather than as a separate window, and styles it to mimic Binance’sEdgeAn Aotera/Tedy loader injects a Vidar-class stealer into a Windows process, which then launches Chrome or Edge and injects its scripts into the pages the victim opens.GmailA webmail injection covering Gmail, Outlook, Yahoo, and Proton then watches for the exchange’s withdrawal confirmation, using keywords in about 24 languages, and rewrites its subject and body in the victim’s browser soGoogle ChromeAn Aotera/Tedy loader injects a Vidar-class stealer into a Windows process, which then launches Chrome or Edge and injects its scripts into the pages the victim opens.Netskope Threat ProtectionNetskope Threat Protection detects this campaign at three layers.OutlookA webmail injection covering Gmail, Outlook, Yahoo, and Proton then watches for the exchange’s withdrawal confirmation, using keywords in about 24 languages, and rewrites its subject and body in the victim’s browser soProtonA webmail injection covering Gmail, Outlook, Yahoo, and Proton then watches for the exchange’s withdrawal confirmation, using keywords in about 24 languages, and rewrites its subject and body in the victim’s browser soWindowsAn Aotera/Tedy loader injects a Vidar-class stealer into a Windows process, which then launches Chrome or Edge and injects its scripts into the pages the victim opens.YahooA webmail injection covering Gmail, Outlook, Yahoo, and Proton then watches for the exchange’s withdrawal confirmation, using keywords in about 24 languages, and rewrites its subject and body in the victim’s browser so
Tools
Burp Suiteradare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (Process Monitor, Process Explorer, Process Hacker, PEStudio), and virtual-machineCharlesdnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (Process Monitor, Process Explorer, Process Hacker, PEStudio), andCutterThe list covers debuggers and disassemblers (IDA, x64dbg, OllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (ProcessdnSpyThe list covers debuggers and disassemblers (IDA, x64dbg, OllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (ProcessFiddlerOllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (Process Monitor, Process Explorer, Process Hacker, PEStudio),Fridadebuggers and disassemblers (IDA, x64dbg, OllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (Process Monitor,IDAThe list covers debuggers and disassemblers (IDA, x64dbg, OllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (ProcessOllyDbgThe list covers debuggers and disassemblers (IDA, x64dbg, OllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (ProcessPEStudioFiddler, Charles, Burp Suite), process monitors (Process Monitor, Process Explorer, Process Hacker, PEStudio), and virtual-machine and sandbox agents (VMware, VirtualBox, QEMU guest tools).Pinand disassemblers (IDA, x64dbg, OllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (Process Monitor, ProcessProcess ExplorerPin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (Process Monitor, Process Explorer, Process Hacker, PEStudio), and virtual-machine and sandbox agents (VMware, VirtualBox, QEMU guestProcess Hacker(Wireshark, Fiddler, Charles, Burp Suite), process monitors (Process Monitor, Process Explorer, Process Hacker, PEStudio), and virtual-machine and sandbox agents (VMware, VirtualBox, QEMU guest tools).Process Monitor(Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (Process Monitor, Process Explorer, Process Hacker, PEStudio), and virtual-machine and sandbox agents (VMware,radare2The list covers debuggers and disassemblers (IDA, x64dbg, OllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (ProcessWiresharkx64dbg, OllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (Process Monitor, Process Explorer, Process Hacker,x64dbgThe list covers debuggers and disassemblers (IDA, x64dbg, OllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (Process