
Binance Hit by $6.3 Billion Crypto Heist, Attributed to North Korean Group
Summary
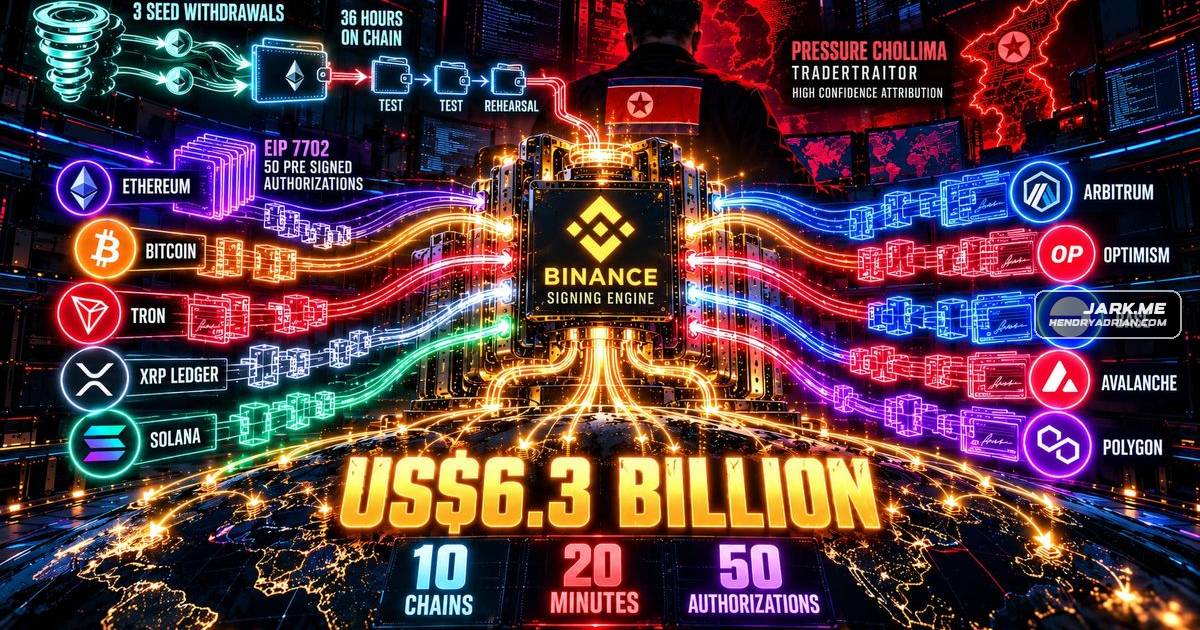
Binance’s hot wallets reportedly lost about $6.3 billion across ten blockchains. TRM Labs and Chainalysis attributed the heist to North Korea-linked PRESSURE CHOLLIMA; how the attacker accessed Binance’s signing systems remains unresolved.
Key points
- On October 29, Binance wallets transferred assets across ten blockchains; most of the reported $6.3 billion moved in roughly 20 minutes.
- On Ethereum, the attacker used EIP-7702 to make a Binance wallet execute code that forwarded assets. The article says the feature worked as designed and did not itself provide initial access.
- TRM assessed that the attacker reached Binance’s hot-wallet signing infrastructure, citing coordinated valid transactions across chains. Binance has not published a root cause and said it found no evidence that wallet private keys had leaked.
- TRM Labs attributed the operation with high confidence to PRESSURE CHOLLIMA, also known as TraderTraitor; Chainalysis reached the same conclusion.
- Stablecoin issuers and Arbitrum reportedly froze about $2.7 billion. TRM estimated the attacker still held more than 420,000 ETH and 18,270 BTC, worth about $2.4 billion.
- Binance said it would cover the losses and had set aside more than $6.34 billion through its SAFU fund and corporate treasury.
- TRM’s cited guidance recommends separating signing infrastructure and approval paths by blockchain and wallet tier.
Article Details
- Victim Organization
- Binance
- Incident Type
- Cross-chain cryptocurrency theft from Binance hot wallets. The attacker transferred assets across ten blockchains. TRM assesses that the attacker gained control of Binance's signing infrastructure; Binance has not published a root cause, and the method of initial access remains unclear.
- Incident Date
- 2026-10-29
- Operational Impact
- Approximately US$6.3 billion in cryptocurrency was stolen from Binance's own wallets. Issuers and Arbitrum's Security Council froze roughly US$2.7 billion; TRM estimated the attacker still held about US$2.4 billion beyond issuers' reach. Binance said it would cover the losses and set aside more than US$6.34 billion through SAFU and its corporate treasury.
- Claim Status
- confirmed
MITRE ATT&CK
People
Threat Actors
Vendors
Binancefrom Tornado Cash. On the morning of October 28, they landed in a staging wallet not yet linked to Binance. Over the next thirty-six hours, the attacker built the theft in pieces, deploying code, testing itCirclein any large theft, because the issuers behind them can freeze a balance on command. Within hours Tether, Circle, and other issuers froze about US$2.67 billion. Arbitrum's Security Council locked roughly US$30 millionRippleby code, nor by any property of the blockchains themselves. It was frozen by companies, Tether, Circle, Ripple, and a few others, reaching into their own ledgers and switching balances off. An industry selling itselfTetherspot in any large theft, because the issuers behind them can freeze a balance on command. Within hours Tether, Circle, and other issuers froze about US$2.67 billion. Arbitrum's Security Council locked roughly US$30