Datadog Releases 100+ Vulnerable AWS Labs for Cloud Security Testing
Summary
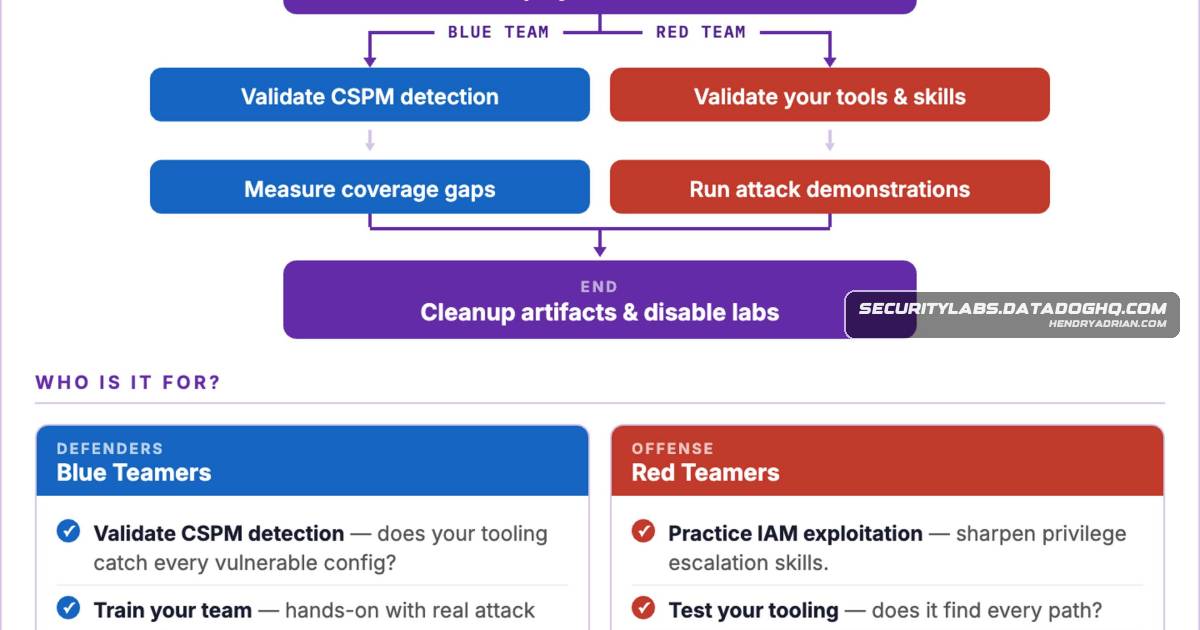
Datadog’s Pathfinding Labs offers more than 100 deployable, intentionally vulnerable AWS environments for practicing privilege escalation and testing CSPM detection. The labs run in sandbox accounts through a Go CLI.
Key points
- Pathfinding Labs includes a web catalog, Terraform-based lab environments, and the plabs Go CLI for enabling, deploying, exploiting, and removing labs.
- More than 100 labs cover privilege escalation, CSPM misconfigurations, toxic combinations, multi-hop paths, and cross-account scenarios.
- Each lab includes an exploitation script to verify the attack path and can help teams test whether CSPM tools identify exploitable misconfigurations.
- Labs can also help evaluate graph-based cloud security tools by checking whether they reconstruct the deployed attack paths.
- The labs deliberately create vulnerable resources, including overly permissive roles, administrative users, public S3 buckets, and internet-facing Lambda functions.
- Datadog advises using a dedicated, isolated sandbox account—not production or accounts containing customer data—and running plabs destroy when finished.
- A hosted version for training and demonstrations is in development; the self-hosted labs are available now.
Article Details
- Event Type
- Launch of Pathfinding Labs, a collection of intentionally vulnerable AWS environments for security testing and training.
- Impact
- Provides more than 100 deployable labs for practicing cloud attack paths and validating CSPM detection. The labs create vulnerable resources and should be deployed only in dedicated sandbox accounts, not production accounts or accounts containing real customer data.
People
Vendors
Products
AWSEarlier this year, we launched pathfinding.cloud, a catalog of AWS IAM privilege escalation techniques.Pathfinding LabsToday, we're thrilled to introduce Pathfinding Labs, a collection of intentionally vulnerable AWS environments that can be deployed into a sandbox account, exploited, and torn down.pathfinding.cloudEarlier this year, we launched pathfinding.cloud, a catalog of AWS IAM privilege escalation techniques.TerraformThe Terraform labs: https://github.com/DataDog/pathfinding-labs