
Datadog Details ARTEX Activity in AWS Environments
Summary
Datadog details ARTEX-attributed activity observed in AWS in October 2026, including CloudWatch searches using compromised IAM keys and abuse of public Cognito pools, and shares behaviors and detections for hunting.
Key points
- Datadog attributed in-the-wild activity across several AWS environments to ARTEX, an AI-native penetration framework.
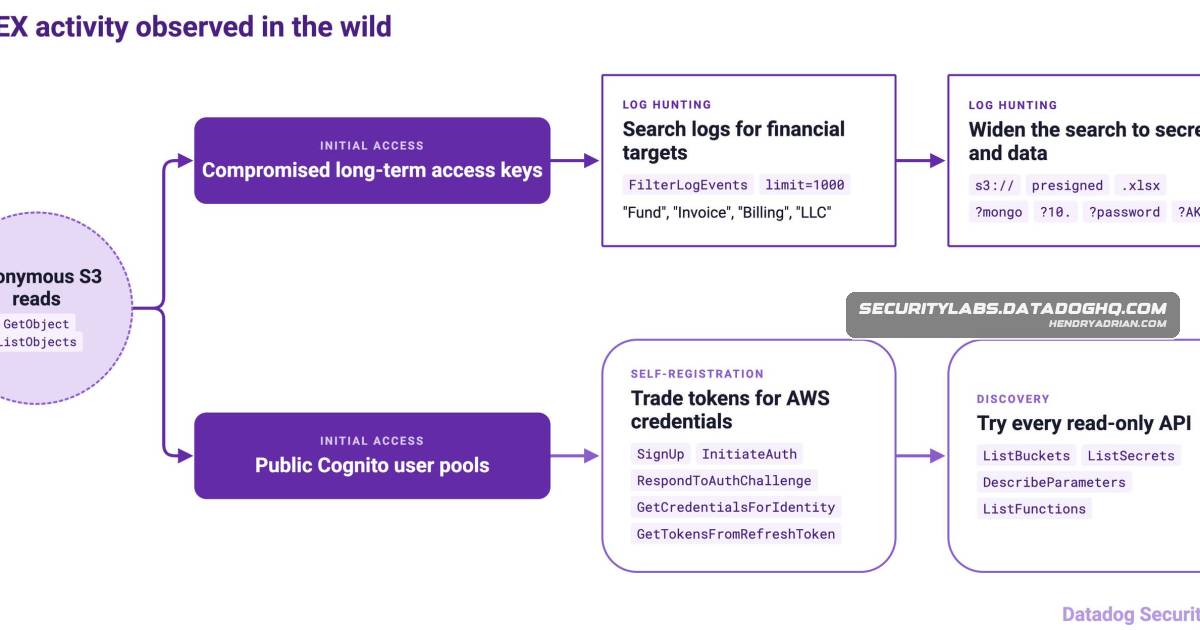
- Sessions reviewed by Datadog began with anonymous S3 read requests, including GetObject and ListObjects.
- Using a valid long-term access key, ARTEX repeatedly called CloudWatch FilterLogEvents to search for financial organizations, file paths, storage links, and secrets.
- In a public Cognito user pool example, ARTEX registered an account, collected tokens, obtained temporary AWS credentials, and attempted broad read-only resource enumeration; the calls failed because the role lacked permissions.
- Datadog observed tenant-domain validation probing during Cognito sign-up attempts and user agents that sometimes identified ARTEX.
- In early November 2026, Datadog linked activity IPs to a hosted console and found hundreds of additional internet-exposed ARTEX consoles.
- Suggested hunting signals include ARTEX user agents, associated IP addresses, unusual S3 access, and spikes in permission-denied events.
Article Details
- Attack Vectors
- ARTEX used compromised long-term AWS access keys to search CloudWatch logs for financial information, file and storage links, internal secrets, internal IP addresses, and database information.
- ARTEX made unauthenticated requests to S3, including GetObject and ListObjects calls.
- Against public Cognito user pools, ARTEX attempted self-registration, collected tokens, exchanged them for AWS credentials, and then tried to enumerate AWS resources.
- ARTEX used Cognito account-recovery operations, including InitiateAuth, ForgotPassword, and ResendConfirmationCode, in activity reported by Wiz.
- Defensive Notes
- Hunt for ARTEX-related user agents and activity from the IP addresses listed as indicators; user agents can be changed.
- Review for large volumes of AccessDenied errors, S3 object enumeration, and unusual access patterns such as EC2 instance-role credentials used from a non-AWS IP.
- Investigate CloudTrail events involving cloud resource discovery and secret enumeration.
- Datadog recommends rotating AWS access keys every 90 days or less and deactivating or removing unused credentials.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 102[.]216[.]154[.]102 | Listed in the article's indicators appendix as associated with ARTEX activity. |
| IPV4 | 103[.]54[.]154[.]32 | Listed in the article's indicators appendix as associated with ARTEX activity. |
| IPV4 | 103[.]54[.]154[.]40 | Source IP from which a compromised long-term AWS key was used during a reported ARTEX session. |
| IPV4 | 154[.]36[.]136[.]197 | Listed in the article's indicators appendix as associated with ARTEX activity. |
| IPV4 | 154[.]36[.]136[.]23 | Listed in the article's indicators appendix as associated with ARTEX activity. |
| IPV4 | 154[.]64[.]252[.]77 | Source IP for a reported ARTEX Cognito sign-up activity spike on October 26 and 27. |
| IPV4 | 169[.]128[.]55[.]214 | Listed in the article's indicators appendix as associated with ARTEX activity. |
| IPV4 | 45[.]145[.]228[.]25 | Listed in the article's indicators appendix as associated with ARTEX activity. |
| IPV4 | 82[.]158[.]88[.]233 | Listed in the article's indicators appendix as associated with ARTEX activity. |
| IPV4 | 88[.]229[.]22[.]232 | Listed in the article's indicators appendix as associated with ARTEX activity. |
MITRE ATT&CK
T1078.004 · Cloud AccountsARTEX used compromised, valid long-term AWS access keys to access victim environments.T1526 · Cloud Service DiscoveryARTEX attempted to discover cloud services through calls including ListSecrets, DescribeParameters, ListTopics, GetRestApis, and ListFunctions20150331.T1528 · Steal Application Access TokenIn the reported Cognito activity, ARTEX registered an account and collected tokens before using them in a flow to obtain AWS credentials.T1530 · Data from Cloud StorageThe article reports unauthenticated S3 reads and ARTEX attempts to retrieve objects.T1580 · Cloud Infrastructure DiscoveryAfter obtaining AWS credentials through a Cognito flow, ARTEX attempted AWS infrastructure discovery calls such as ListBuckets and DescribeLogGroups.T1619 · Cloud Storage Object DiscoveryARTEX issued S3 ListObjects and similar requests to enumerate cloud storage objects.
Threat Actors
Vendors
Amazon Web ServicesIn October 2026, Datadog observed in-the-wild activity from ARTEX, an AI-native penetration framework, against several AWS environments, with a focus on accessing financial data.DatadogIn October 2026, Datadog observed in-the-wild activity from ARTEX, an AI-native penetration framework, against several AWS environments, with a focus on accessing financial data.
Products
Amazon CloudWatchUsing compromised long-term IAM access keys, ARTEX searched through CloudWatch using FilterLogEvents, hunting for financial information, file paths and secrets such as long-lived AKIA access keys and passwords.Amazon CognitoWe also observed unauthenticated abuse of public Amazon Cognito user pools, including anonymous sign-ups, token collection, and follow-up AWS account enumeration attempts.AWSIn October 2026, Datadog observed in-the-wild activity from ARTEX, an AI-native penetration framework, against several AWS environments, with a focus on accessing financial data.Cloud Security MisconfigurationsDatadog Cloud Security Misconfigurations ships with out-of-the-box (OOTB) rules to help you identify risky long-lived AWS credentials proactively:CloudTrailIn CloudTrail, these show a userIdentity.type of AWSAccount and an accountId of anonymous, calling GetObject, ListObjects and similar read APIs.Datadog Cloud SIEMDatadog Cloud SIEM contains several out-of-the-box (OOTB) rules that can detect ARTEX-related post-exploitation and initial access in your AWS environment:IAMUsing compromised long-term IAM access keys, ARTEX searched through CloudWatch using FilterLogEvents, hunting for financial information, file paths and secrets such as long-lived AKIA access keys and passwords.S3ARTEX activity observed in the wild, from anonymous S3 reads to compromised access keys and public Cognito user pools (click to enlarge)
Tools
ARTEXIn October 2026, Datadog observed in-the-wild activity from ARTEX, an AI-native penetration framework, against several AWS environments, with a focus on accessing financial data.Stratus Red Teambeing used by a non-AWS IP), and CloudTrail events that relate to known cloud attack techniques (Stratus Red Team, Datadog's Cloud Security Atlas and TrailDiscover are useful resources for these).TrailDiscoverthat relate to known cloud attack techniques (Stratus Red Team, Datadog's Cloud Security Atlas and TrailDiscover are useful resources for these).