
SANS Diary Analyzes Macfinger ClickFix’s “DownTheDRAIN” macOS Infostealer
Summary
A SANS diary analyzes a DownTheDRAIN macOS infostealer sample delivered through the Macfinger ClickFix campaign. The author says macOS blocked it before sensitive data could be exfiltrated; Huntress identified a function that can redirect cryptocurrency wallet contents.
Key points
- The diary covers a sample distributed through the Macfinger ClickFix campaign on November 11, 2026, using a fake CAPTCHA page and ClickFix instructions.
- The instructions led to a shell script that installed an arm64 Mach-O infostealer.
- Huntress reported that a function in a sample can identify cryptocurrency wallet addresses and redirect their contents to a threat-actor-controlled wallet.
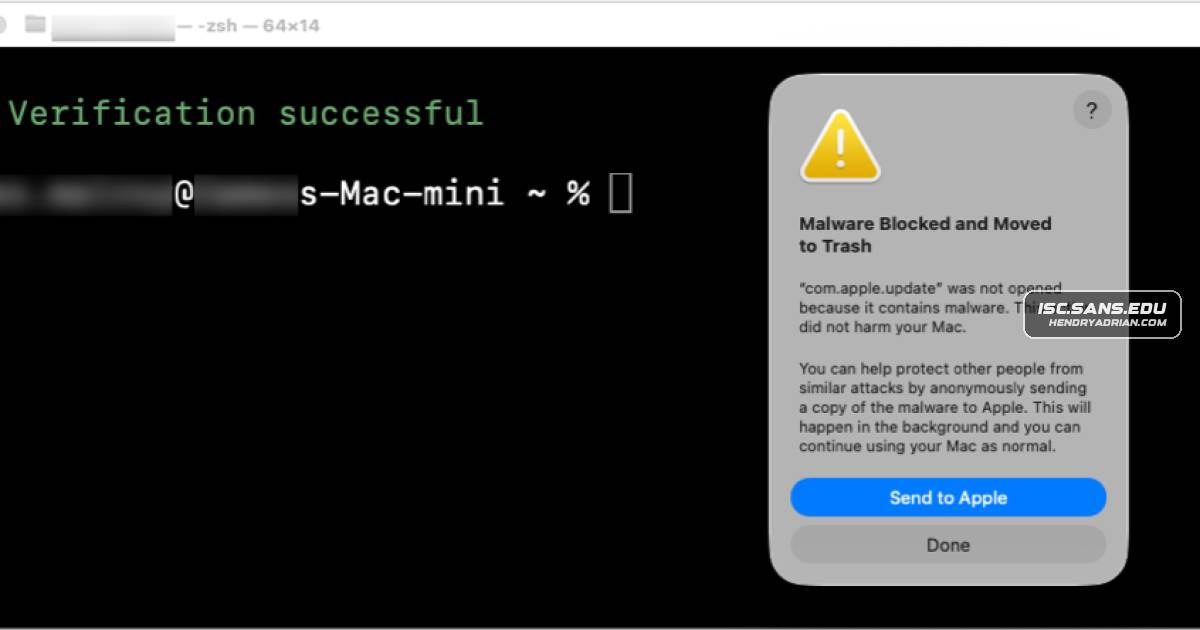
- The author observed four HTTP POST requests before macOS 26.7.3 blocked the malware and moved it to Trash; the author says this occurred before sensitive data could be exfiltrated.
- The diary provides file hashes and network indicators, including traffic to 171.22.131.24:8133.
Article Details
- Event Type
- Macfinger ClickFix campaign distributing the DownTheDRAIN macOS infostealer through a fake CAPTCHA page and pasted Terminal commands.
- Impact
- The malware is described as stealing information and redirecting cryptocurrency wallet contents to an attacker-controlled wallet. In the reported test, macOS blocked the malware before it could exfiltrate sensitive data.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | quill-kraee-um2gf[.]pro | Campaign domain serving the fake CAPTCHA page. |
| SHA256 | 58e503cc2e6aacc6bdba54f40a7edebf7a5362bef0a9039769baaba8c472c4db | SHA-256 hash of the shell script retrieved through ClickFix that installs DownTheDRAIN. |
| SHA256 | 8b5026d841aa93758ec3cb55c276f84d3ec1cf459810e0d9aa5624e2776f2fcd | SHA-256 hash of the DownTheDRAIN infostealer Mach-O binary. |
| SHA256 | c34cc30cb1cff5c47d77e62a3ba63e9a183989ec1ccdf7929beb1bcae0d41f23 | SHA-256 hash of the DownTheDRAIN infostealer saved on the infected host. |
| URL | hxxp[:]//171[.]22[.]131[.]24:8133/api/t | Infection-related HTTP POST endpoint contacted by the malware. |
| URL | hxxp[:]//45[.]150[.]32[.]130/37339606cba4522a?force=1 | Payload URL used to retrieve the shell script that installs DownTheDRAIN. |
| URL | hxxp[:]//45[.]150[.]32[.]130/4be1066a49e75?force=1 | Payload URL used to retrieve the DownTheDRAIN infostealer binary. |