
Investigation Links Qilin Administrator Haise to Aleksey Yakovtsev
Summary
A KrebsOnSecurity investigation links Qilin administrator “Haise” to Aleksey Yakovtsev through forum identities, Telegram accounts, email and phone records, and leaked Russian data; Yakovtsev did not respond to outreach.
Key points
- The article says Qilin claimed at least 365 victim organizations in the preceding three months; an NCC Group report described it as the most active ransomware affiliate program.
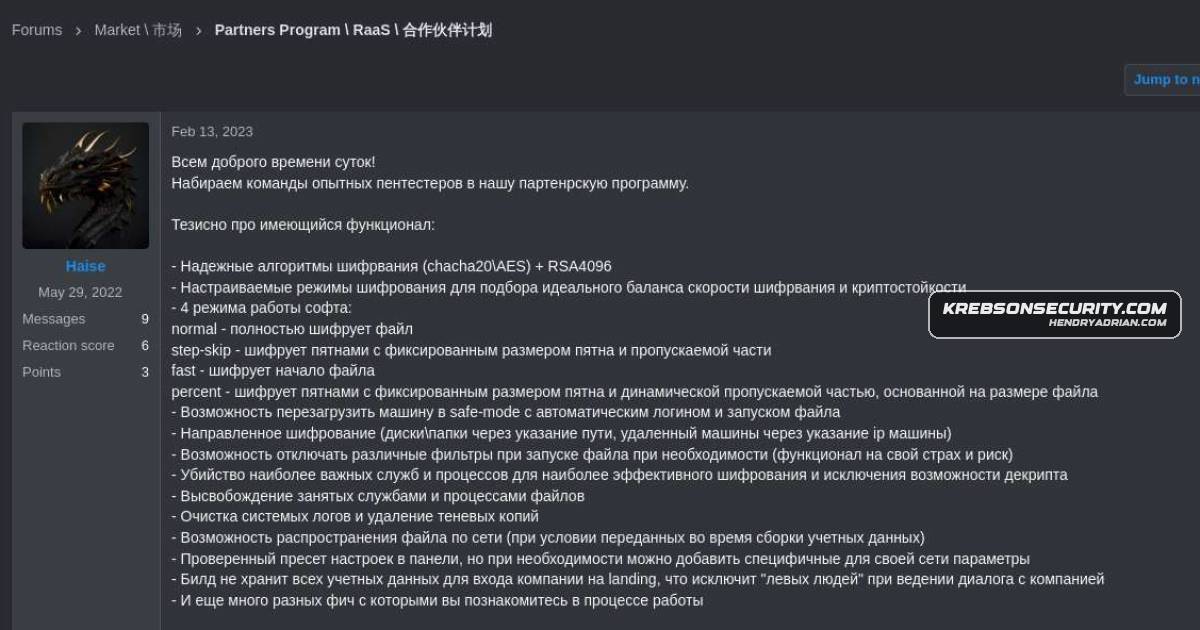
- Intel 471-indexed RAMP messages show that Haise applied to the forum in 2022 using the Telegram username Alexbigboss44.
- Intel 471 records connect Alexbigboss44 to the forum identity Rjun, which used the email address [email protected].
- The article says leaked Gosuslugi records associate that email address with 36-year-old Aleksey Yakovtsev of St. Petersburg; the exposure of more than 20 million records was reported, not independently established in this article.
- The investigation also correlates Telegram account and phone records with other email and travel records to support its identification.
- The article attributes parts of the identity analysis to Intel 471, Flashpoint, Spycloud, Constella Intelligence, and IntelHawk; Yakovtsev did not respond to attempts to contact him.
Article Details
- Attack Vectors
- Qilin recruits affiliates to hack organizations and deploy ransomware, offering affiliates at least 80 percent of any extortion payment.
- Qilin affiliates use double extortion: they steal sensitive data before encrypting systems and threaten to publish the files online.
MITRE ATT&CK
People
Aleksey Mikhailovich YakovtsevLeaked Gosuslugi records reportedly connect him to an email address associated with the Qilin administrator’s older accounts; the article presents him as the suspected real-life identity of the administrator, not as a confirmed identification.Leo BogodIntelHawk founder and chief technology officer who described the analysis linking the identities and their alleged progression through cybercrime-related activities.
Threat Actors
HaiseThe reported handle of Qilin’s administrator, who promotes the affiliate program. The article links this identity to the older handles Rjun and Alexbigboss44.QilinA ransomware-as-a-service group reported to have operated since September 2022; its affiliates hack organizations, deploy ransomware, steal data, and threaten publication.RansomHubQilin’s leader reportedly said the group had worked with RansomHub.RjunAn older forum identity linked by the article’s cited intelligence sources to Qilin administrator Haise and the Telegram username Alexbigboss44.Scattered SpiderQilin’s leader reportedly said the group had worked with Scattered Spider.
Malware
Vendors
Constella IntelligenceA search for that email at the breach tracking service Constella Intelligence shows that it appeared in records maintained by gosuslugi.ru, the official digital platform for state and municipal services in the RussianFlashpointThe cyber intelligence platform Flashpoint finds Alexbigboss44 is a prolific participant in cybercriminal forums and Telegram channels, primarily focused on the illicit trade of traffic, logs, and corporate access [fullIntel 471The cyber intelligence platform Intel 471 records that in June 2022, Haise applied for membership to RAMP, a closely-guarded Russian cybercrime forum that was created as a haven for ransomware affiliate programs.IntelHawkHaise and the much older Rjun and Alexbigboss44 accounts was shared privately earlier this month by IntelHawk, which describes itself as an AI-based platform capable of de-anonymizing threat actors based onSpycloudThe identity threat protection firm Spycloud found the email address [email protected] at one time used the password “Rjun132” [Spycloud is also an advertiser on this blog].
Products
FacebookFlashpoint says this user was engaged in high-volume acquisition of Facebook logs and Google Ads accounts to facilitate fraudulent advertising and gambling schemes, and that they functioned as a broker and operator —Google AdsFlashpoint says this user was engaged in high-volume acquisition of Facebook logs and Google Ads accounts to facilitate fraudulent advertising and gambling schemes, and that they functioned as a broker and operator —Telegramout of Russia, Qilin is happy to team with English-speaking affiliates, and its leader has shared on Telegram that they’ve worked with cybercrime groups like Scattered Spider and RansomHub.
Tools
Countries
Industries
Cybersecuritythe most industrious ransomware-as-a-service gang, according to a report (PDF) this month by the cybersecurity firm NCC Group (KrebsOnSecurity profiled the administrator of the second most active ransomware groupGamblingacquisition of Facebook logs and Google Ads accounts to facilitate fraudulent advertising and gambling schemes, and that they functioned as a broker and operator — managing a network of traffickers and