
Datadog Reproduces Unauthenticated Crash Triggered by MongoDB CVE-2026-118383
Summary
Datadog reproduced a crash in MongoDB replica-set members using two unauthenticated ping requests and a later election/catch-up event. CVE-2026-118383 is fixed in listed releases; the tests did not achieve code execution.
Key points
- CVE-2026-118383 is a critical use-after-free in MongoDB Server's primary catch-up process, rated CVSS 4.0 at 9.5.
- It affects replica-set members, including shard and config server members; standalone mongod instances are not affected.
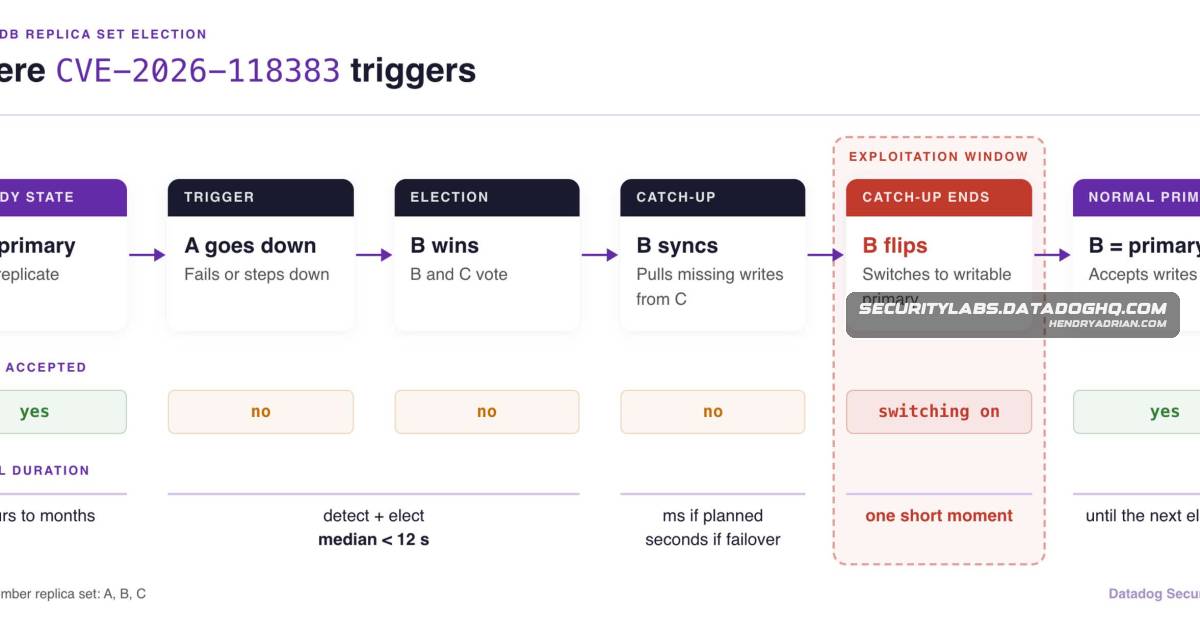
- Two unauthenticated ping requests containing readConcern.afterOpTime can leave waiters on a vulnerable member. A later election while that member is behind can trigger double cleanup and a crash.
- Datadog reproduced a segmentation fault on MongoDB Server 8.0.34. The tests did not demonstrate code execution; MongoDB says arbitrary code execution is possible under certain conditions.
- Fixed releases are 9.0.7, 8.3.16, 8.0.37, 7.0.48, 6.0.30, 5.0.35, and 4.4.32. Upgrade every affected replica-set member; restricting network access can reduce exposure while upgrading.
- Logs may show Slow query events with ping and readConcern.afterOpTime fields, followed by two catch-up exits and a fatal signal or backtrace involving CatchupState::abort_inlock().
Article Details
- Attack Vectors
- An unauthenticated client can send two ping requests containing readConcern.afterOpTime to a reachable, vulnerable MongoDB replica set member, leaving waiters that persist until the member restarts, rolls back, or steps down.
- The crash occurs if that member later wins an election while behind another member and completes primary catch-up. The article reports that the attacker cannot cause the lag or election.
- The researchers reproduced a crash on MongoDB Server 8.0.34 but did not achieve code execution. MongoDB's advisory says arbitrary code execution is possible under certain conditions.
- Defensive Notes
- Upgrade every affected replica set member to a fixed release: 9.0.7, 8.3.16, 8.0.37, 7.0.48, 6.0.30, 5.0.35, or 4.4.32, as applicable. Verify versions on all members, including offline members and containerized members.
- Until upgrading, restrict MongoDB network access to systems that require it; this reduces exposure but does not fix the vulnerability. Standalone mongod instances are not affected.
- Review MongoDB structured logs for unauthenticated ping commands with unusual attr.command.readConcern.afterOpTime values and expired waits, alongside a member entering catch-up, exiting catch-up twice in one transition, and a fatal signal or backtrace involving CatchupState::abort_inlock().
MITRE ATT&CK
T1190 · Exploit Public-Facing ApplicationThe article describes unauthenticated requests exploiting CVE-2026-118383 against a reachable MongoDB replica set member.T1499.004 · Application or System ExploitationIn the researchers' reproduction, the vulnerability caused the MongoDB server process to crash when the affected member completed primary catch-up.
CVE
Vendors
Products
Datadog Cloud Security ManagementDatadog Cloud Security Management reports findings for CVE-2026-118383.Datadog Cloud SIEMDatadog Cloud SIEM detections for CVE-2026-118383 are currently being evaluated, and we will update this post when they are available.MongoDB ServerCVE-2026-118383 is a critical use-after-free in MongoDB Server's primary catch-up process, with a CVSS v4.0 score of 9.5.