
StepSecurity compares Secure Registry with GitHub’s npm package firewall
Summary
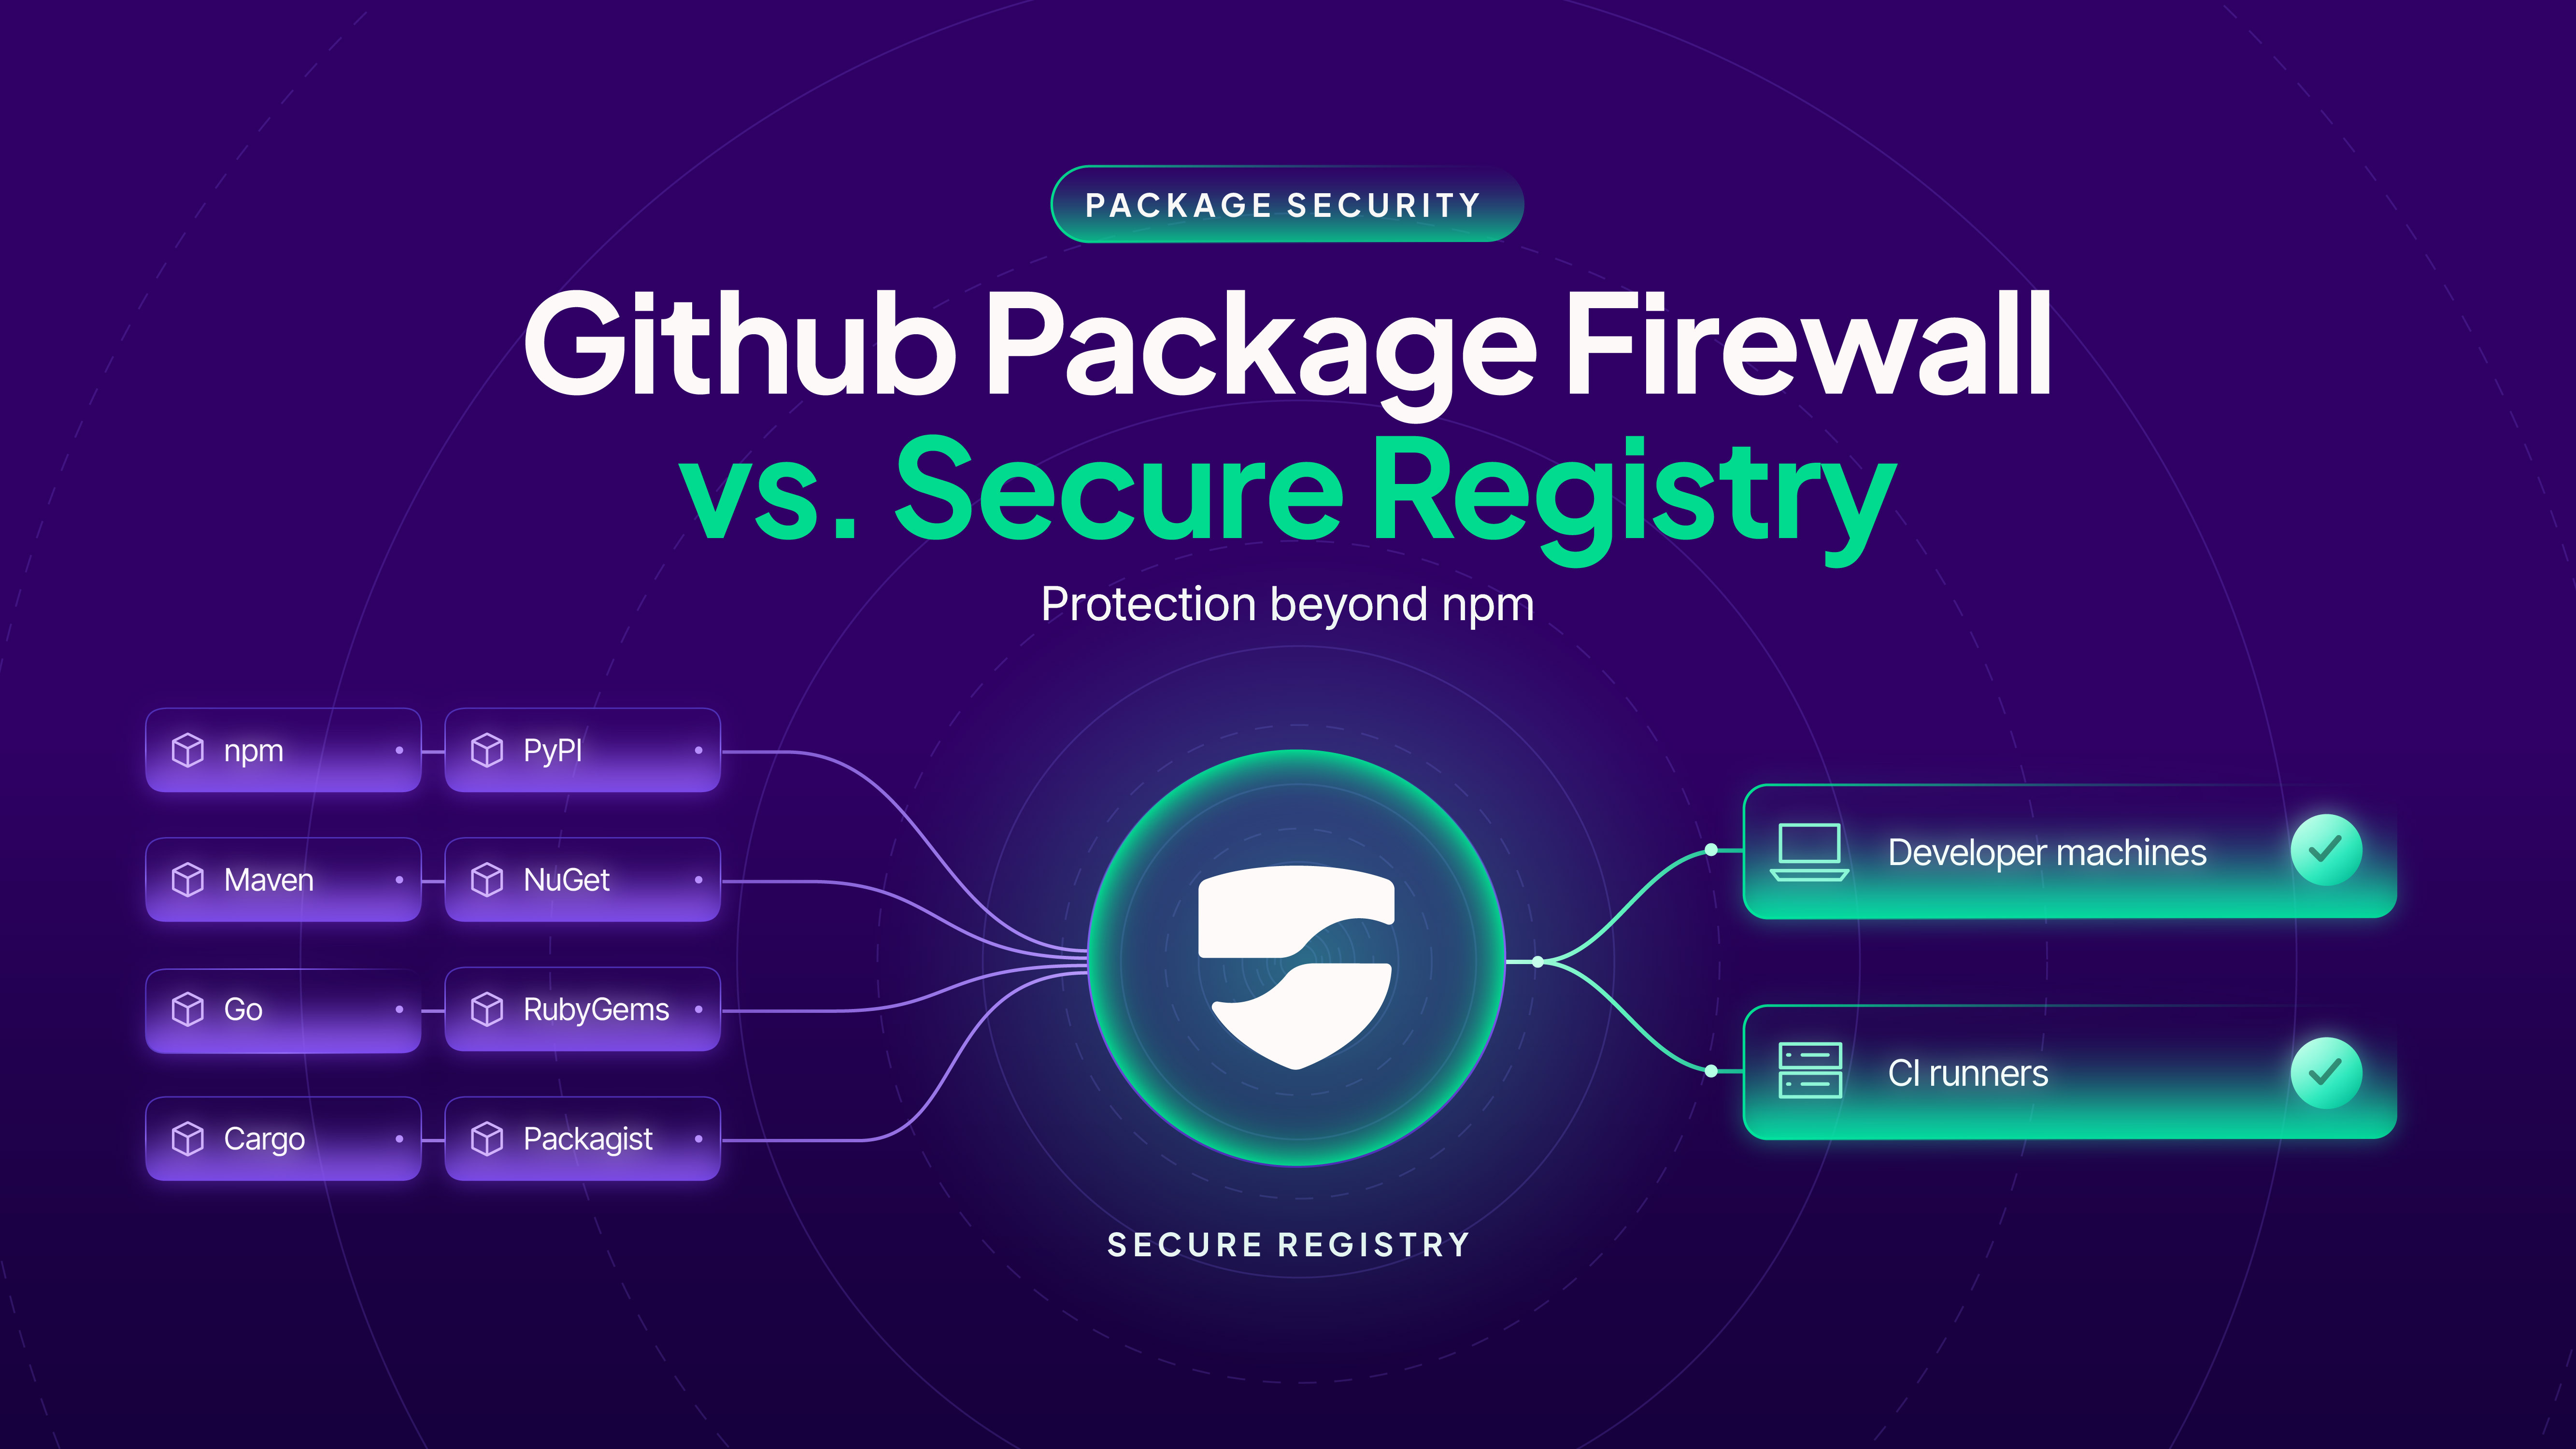
StepSecurity compares GitHub’s npm-only package firewall with Secure Registry, describing its multi-ecosystem coverage, package-request tracking, claimed one-hour blocking SLA, cooldown handling, and controls to prevent registry bypass.
Key points
- GitHub’s package firewall is in public preview, checks npm packages against enterprise policy, and is limited to GitHub Enterprise Cloud customers.
- StepSecurity says Secure Registry supports npm, PyPI, Maven, NuGet, Go, RubyGems, and Cargo, with Packagist in beta.
- Secure Registry logs package requests and can attribute them to a GitHub Actions run or developer machine when source attribution is configured; its inventory includes licenses and known vulnerabilities.
- StepSecurity says its Compromised Packages control is backed by its threat intelligence team and 24×7 SOC, and its SLA commits to blocking a malicious version within one hour of release.
- The product’s cooldown feature holds back new versions while allowing normal installs to resolve to the newest permitted version; requests for an exact version still on hold are blocked.
- StepSecurity describes using device policies and its Dev Machine Guard agent to direct developer machines to Secure Registry, and Harden-Runner baselines and deny policies to identify and block CI jobs that bypass it.
Article Details
- Event Type
- GitHub launched its npm package firewall in public preview; StepSecurity compares it with Secure Registry.
- Impact
- The article describes controls for screening package requests, identifying where packages were installed, blocking malicious versions, delaying new releases, and enforcing registry use across developer machines and CI runners. It says GitHub's firewall supports npm for GitHub Enterprise Cloud customers, while Secure Registry supports several ecosystems. The article also reports that compromised litellm releases on PyPI stole credentials upon installation.
Vendors
GitHubGitHub has launched a package firewall in public preview. It checks npm packages against an enterprise policy before they install. We welcome this feature. Many recent supply chain attacks run the moment a package isStepSecurityFor teams evaluating it, the practical question is how it compares with StepSecurity Secure Registry. Secure Registry sits between your developer machines and CI (Continuous Integration) runners and the public
Products
Harden-RunnerCI runners: Harden-Runner's baselines show which jobs still call public registries such as registry.npmjs.org, and its deny policies block those calls so builds cannot bypass Secure Registry.StepSecurity Dev Machine GuardDeveloper machines: Dev Machine Guard's Package Configs page shows the registry each device actually resolves packages from. Device Policy points npm, PyPI, and Go at Secure Registry, through your MDM (Mobile DeviceStepSecurity Secure RegistryFor teams evaluating it, the practical question is how it compares with StepSecurity Secure Registry. Secure Registry sits between your developer machines and CI (Continuous Integration) runners and the public