
Binance’s Estimated $6.3 Billion Incident Raises Developer-Machine Security Concerns
Summary
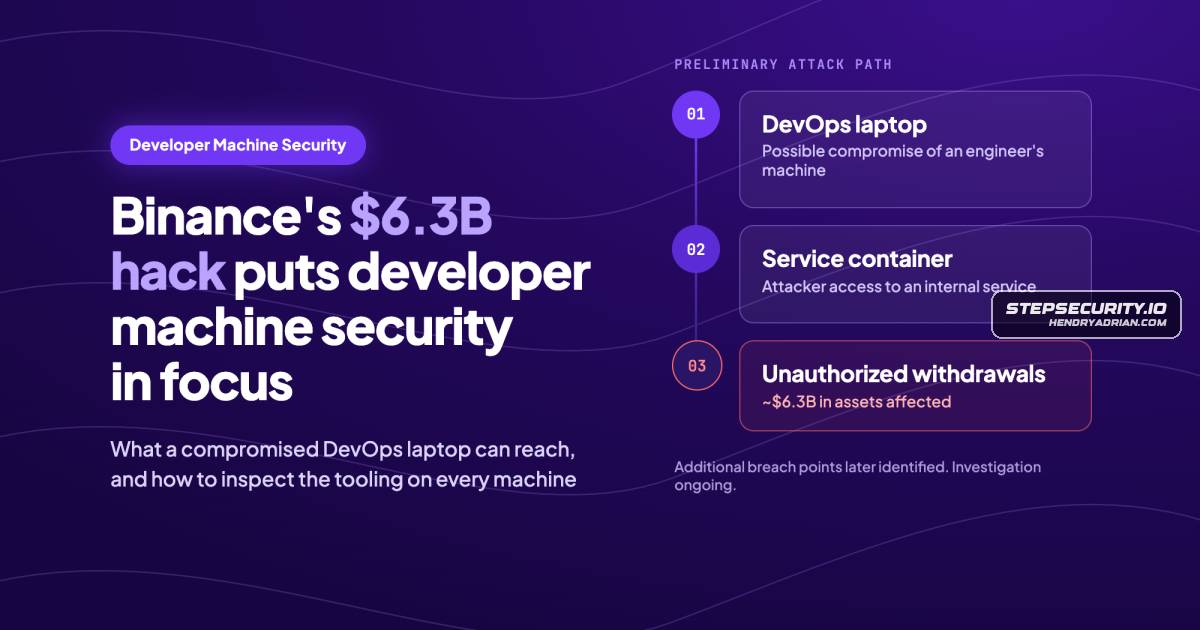
Binance estimates its Oct. 29 incident affected about $6.3 billion; its investigation cited a possible DevOps laptop compromise and later additional breach points. Researchers reported Ethereum signing-infrastructure activity; Binance said it found no evidence of a key-
Key points
- Binance’s initial account described a possible path from a compromised DevOps laptop to a service container and unauthorized withdrawals; a later update identified additional breach points, and the investigation is ongoing.
- Binance said it found no evidence of a wallet private-key leak. It reported pausing withdrawals, keeping deposits unaffected, freezing about $3 billion with partners’ help, and covering losses with SAFU and company funds.
- TRM Labs reported 50 signed Ethereum authorizations covering consecutive nonces and using EIP-7702. Elliptic described a persistent delegation to an attacker-controlled contract that swept funds at least six more times over three and a half hours.
- TRM assessed that the attacker accessed signing infrastructure, but the article says this is not Binance’s completed root-cause analysis; how the laptop may have been compromised remains unresolved.
- The article summarizes developer-tool compromises involving Nx packages and its VS Code extension, OVHcloud CLI release binaries, and a trojanized Claude Code extension, describing risks including credential theft and persistence.
- For investigations, it recommends preserving device evidence, revoking exposed credentials, reviewing connected cloud and command-line access, checking downstream activity, and verifying recovery and persistence.
Article Details
- Event Type
- Binance-reported security incident involving unauthorized withdrawals, with the initial investigation pointing to a possible compromise of a DevOps engineer’s laptop and subsequent access to a service container. The article also describes separate developer-tool and software supply-chain compromises as context; they are not established as the cause of the Binance incident.
- Impact
- Binance estimated that approximately $6.3 billion in assets were affected. It reported pausing withdrawals, said deposits were unaffected, and reported that approximately $3 billion had been frozen with partners’ help. Binance said it found no evidence of a wallet private-key leak and committed to covering losses through its SAFU fund and company funds. TRM Labs assessed that the attacker gained access to signing infrastructure; Binance’s investigation was ongoing, and the laptop’s compromise method was unresolved.
MITRE ATT&CK
Vendors
Products
Claude CodeOctober 2026: A trojanized Claude Code extensionDev Machine Guardinto compromised packages, IDE extensions, and CLI tools show why that question deserves attention. Dev Machine Guard helps inventory this software and identify known threats; its Community tier is free and availableNxAugust 2025: Nx npm packages and AI-assisted reconnaissanceNx ConsoleMay 2026: Nx Console’s VS Code extensionOVHcloud CLIOctober 2026: OVHcloud CLI release binariesStepSecurity Secure RegistrySecure Registry checks package requests at install time. It sits between configured package clients and public registries, so the same controls can apply to a developer running a local install and a CI runnerThreat CenterThreat Center brings active and historical supply chain incidents into one view, with affected components, incident details, and remediation guidance. It helps teams understand what was compromised and what toVS CodeVS Code extensionOpening a workspace fetched a credential stealer. The payload also installed a macOS backdoor.