
StepSecurity Adds AI Agent Plugin Inventories for Developer Devices and GitHub Repositories
Summary
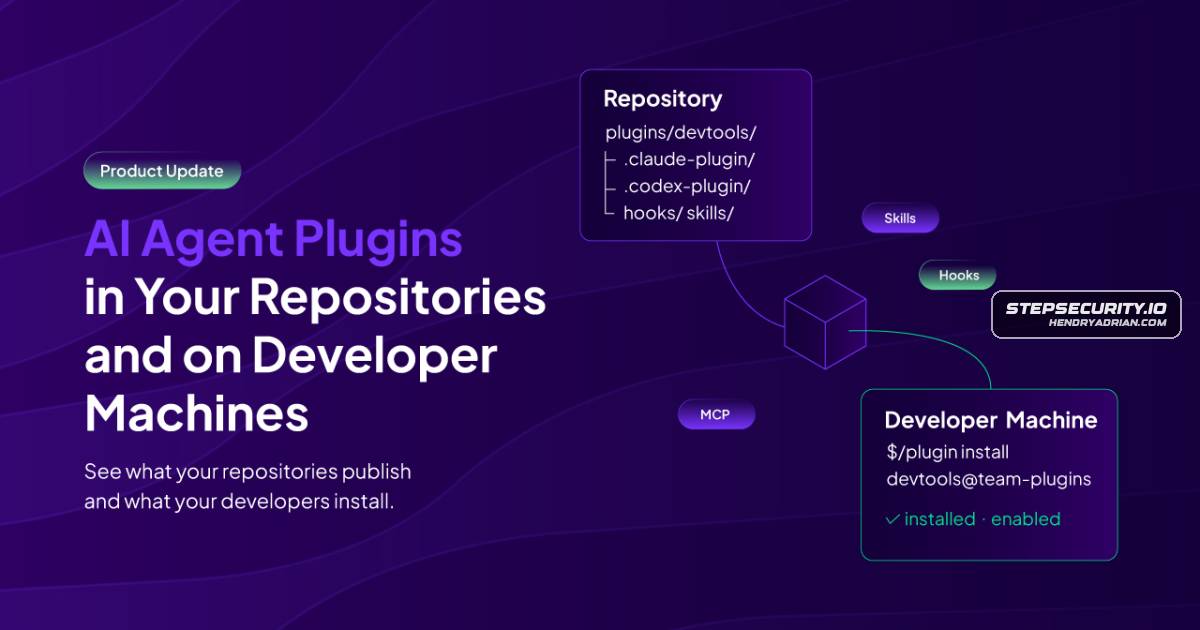
StepSecurity added inventories for Claude Code and Codex plugins installed on developer machines and published or enabled in GitHub repositories, showing plugin sources, versions, components and distribution.
Key points
- Dev Machine Guard inventories Claude Code and Codex plugins installed on developer machines, including their sources, versions, enablement, components and affected devices.
- A separate GitHub inventory shows plugins published in organizational repositories and which repositories enable them for contributors.
- The inventories distinguish manifest-declared plugin metadata from observed sources, helping teams investigate mismatches between declared authors or repositories and the actual publishing location.
- StepSecurity says its device scan reads plugin records, manifests and declared components without running plugins, hooks, scripts or agent command-line tools, and makes no network requests.
- The company says plugin metadata and definition hashes are reported while skill and command bodies, credentials and complete settings files remain on the device.
Article Details
- Event Type
- Security product feature announcement
- Impact
- StepSecurity announced inventories for Claude Code and Codex plugins on developer machines and in organizational GitHub repositories. The inventories show plugin sources, declared metadata, versions, enablement, components, and repository usage, helping security teams review plugin supply-chain exposure. The article describes risks and prior incidents involving related mechanisms, but does not report a malicious plugin or a new compromise.
Malware
Vendors
Products
Claude CodeStepSecurity now gives security teams an inventory of both. Dev Machine Guard shows the Claude Code and Codex plugins installed on your developer machines, and a new Agent Plugins page under GitHub shows the pluginsCodexStepSecurity now gives security teams an inventory of both. Dev Machine Guard shows the Claude Code and Codex plugins installed on your developer machines, and a new Agent Plugins page under GitHub shows the pluginsDev Machine GuardStepSecurity now gives security teams an inventory of both. Dev Machine Guard shows the Claude Code and Codex plugins installed on your developer machines, and a new Agent Plugins page under GitHub shows the pluginsGitHubClaude Code and Codex plugins installed on your developer machines, and a new Agent Plugins page under GitHub shows the plugins your organization's repositories publish and enable. Together, they answer two