
Analysis Identifies 8,318 DNS-Linked Artifacts Tied to 2025 Salesforce Supply-Chain Attack
Summary
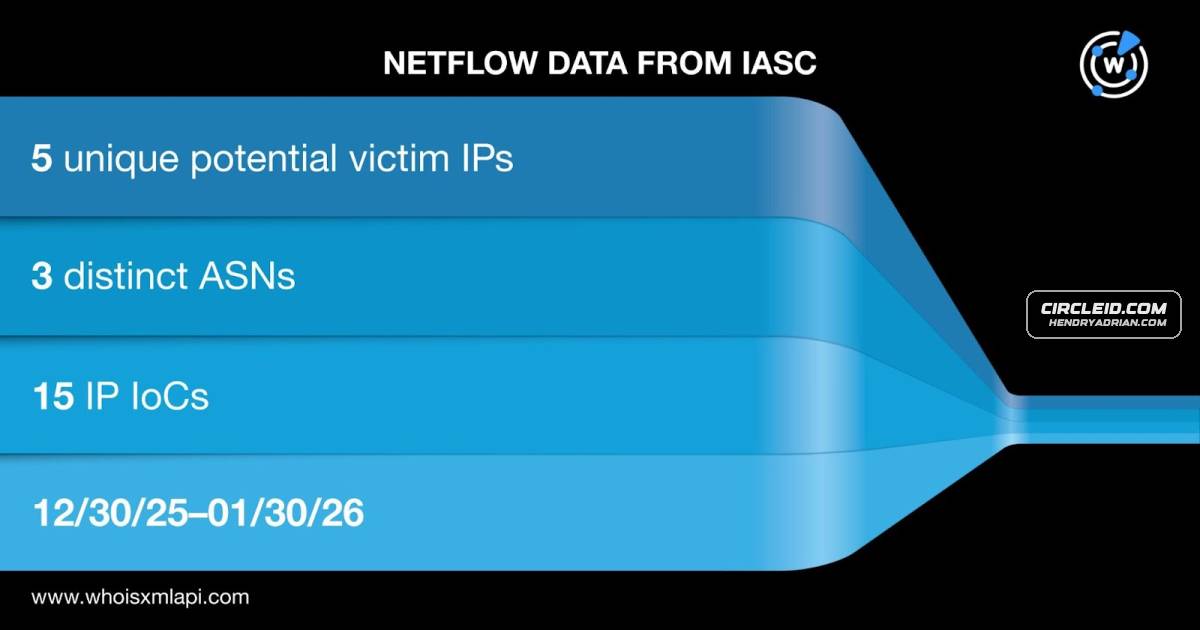
An analysis of LevelBlue and Seqrite IoCs associated with the 2025 Salesforce SaaS supply-chain attack identified 8,318 related artifacts, including domains and IPs; it also found 1,722 potential victim IPs communicated with 24 IoC IPs.
Key points
- The article says reports attributed the 2025 Salesforce SaaS supply-chain attack to Scattered Lapsus$ Hunters, described as a collaboration between Scattered Spider and ShinyHunters.
- The analysis combined 39 IoCs from LevelBlue and Seqrite, excluding two domains the authors considered legitimate.
- Historical WHOIS and DNS analysis linked the IoCs to 8,318 additional artifacts: 405 email-connected domains, two IP addresses, 11 IP-connected domains, and 7,900 string-connected domains.
- Network telemetry showed 1,722 potential victim IP addresses across 152 ASNs communicating with 24 IoC IP addresses between December 30, 2025, and January 30, 2026.
- The authors said one IoC domain, ticket-audemarspiguet[.]com, was deemed likely to turn malicious 76 days before it appeared in the Seqrite report.
- The article cautions that some entities labeled as threats may prove harmless and recommends further investigation to corroborate the findings.
Article Details
- Attack Vectors
- The reported attackers obtained OAuth tokens and accessed SaaS/CRM accounts and data.
- Phishing activity was associated with several discovered domains, including ticket-escrow[.]com and ticket-frankfurt[.]de.
- Malicious domains were registered and used in connection with the campaign; some related domains were associated with malware distribution.
- Defensive Notes
- The article recommends conducting supplementary investigations to corroborate entities identified as threats, since some may later be deemed harmless or their context may change.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | join-meets[.]com | Email-connected domain reported as associated with malware distribution from 28 July 2025 to 24 January 2026. |
| DOMAIN | ticket-audemarspiguet[.]com | Identified as an IoC; the article says it was registered with malicious intent on 20 June 2025. |
| DOMAIN | ticket-aviata[.]info | String-connected domain reported as associated with malware distribution. |
| DOMAIN | ticket-dior[.]com | Identified as a domain IoC associated with the reported Salesforce supply-chain attack investigation. |
| DOMAIN | ticket-escrow[.]com | String-connected domain reported as associated with phishing. |
| DOMAIN | ticket-frankfurt[.]de | String-connected domain reported as associated with phishing. |
| DOMAIN | ticket-nike[.]com | Identified as a domain IoC associated with the reported Salesforce supply-chain attack investigation. |
| IPV4 | 104[.]21[.]78[.]124 | Additional IP reported as associated with malware distribution and phishing. |
| IPV4 | 185[.]207[.]107[.]130 | Listed as an IP IoC in the article's analysis of infrastructure connected to the attack. |
| IPV4 | 192[.]42[.]116[.]20 | Listed as an IP IoC in the article's analysis of infrastructure connected to the attack. |
| IPV4 | 208[.]68[.]36[.]90 | Listed as an IP IoC in the article's analysis of infrastructure connected to the attack. |
| IPV4 | 31[.]133[.]0[.]210 | Listed as an IP IoC in the article's analysis of infrastructure connected to the attack. |
| IPV4 | 81[.]17[.]28[.]95 | Listed as an IP IoC in the article's analysis of infrastructure connected to the attack. |
MITRE ATT&CK
T1078 · Valid AccountsThe article reports that attackers obtained OAuth tokens to access SaaS/CRM accounts and services.T1566 · PhishingThe article reports phishing activity associated with discovered domains, including ticket-escrow[.]com and ticket-frankfurt[.]de.T1583.001 · DomainsThe article describes domains registered with malicious intent and used in connection with the campaign.
Threat Actors
Scattered Lapsus$ HuntersSOCRadar and reports cited in the article attributed the 2025 Salesforce SaaS supply-chain attack to this collaboration.Scattered SpiderThe article identifies Scattered Spider as a collaborator in Scattered Lapsus$ Hunters, which reports attributed with the Salesforce supply-chain attack.ShinyHuntersThe article identifies ShinyHunters as a collaborator in Scattered Lapsus$ Hunters, which reports attributed with the Salesforce supply-chain attack.
Products
Tools
Industries
Aviationcustomer records and compromising OAuth tokens, CRM data, and support/travel records across technology, aviation, and luxury customers.luxuryand compromising OAuth tokens, CRM data, and support/travel records across technology, aviation, and luxury customers.Technologymillions of customer records and compromising OAuth tokens, CRM data, and support/travel records across technology, aviation, and luxury customers.