
AttackIQ Releases BlackByte Ransomware Emulation to Test Security Controls
Summary
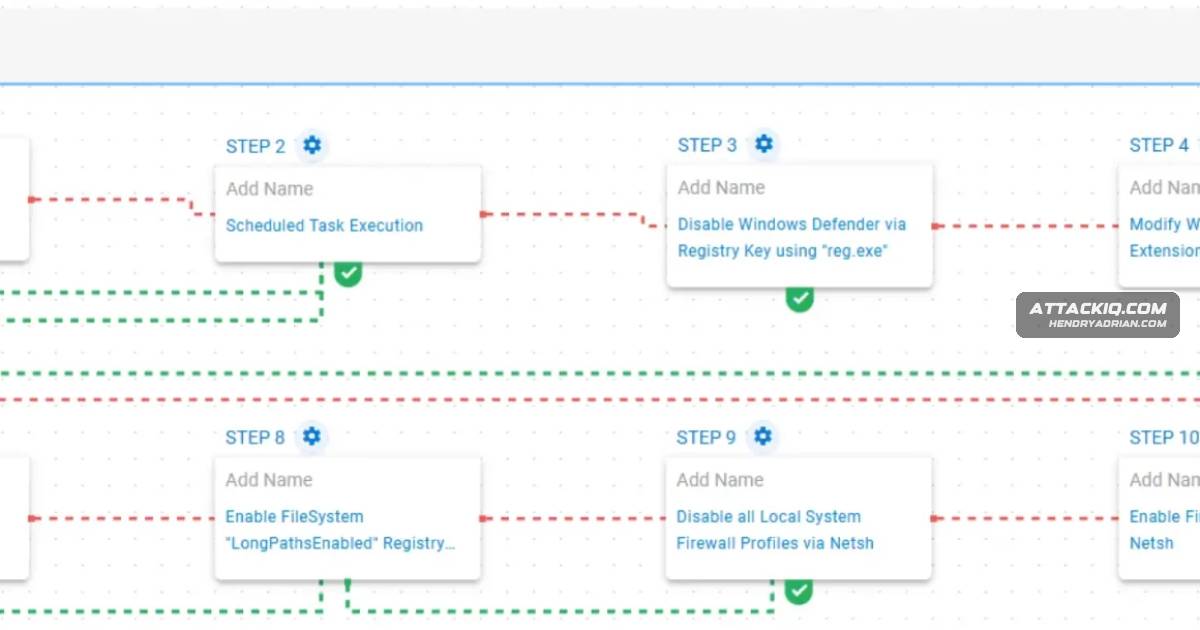
AttackIQ released an emulation of reported BlackByte behaviors for testing security controls, including scheduled-task execution, security-tool tampering, ARP discovery, shadow-copy deletion, and AES/RSA file encryption.
Key points
- AttackIQ's emulation is designed to help organizations assess detection and prevention controls against behaviors associated with BlackByte ransomware.
- Scenarios include scheduled-task execution, Windows Defender and firewall changes, and registry modifications.
- The emulation tests ARP-table discovery, Volume Shadow Copy deletion, and file encryption using AES-128-CBC and RSA-1024.
- AttackIQ says the emulation is based on behaviors reported by Cisco Talos, Trend Micro, Zscaler, Palo Alto Networks, and IC3.
- AttackIQ recommends adding a scenario for discovering Active Directory computers with PowerShell; this is presented as a proposed extension.
Article Details
- Event Type
- AttackIQ released an emulation of BlackByte ransomware behaviors for security-control validation.
- Impact
- The emulation lets organizations test detection and prevention controls against behaviors including scheduled-task execution, security-tool and firewall tampering, ARP discovery, shadow-copy deletion, and file encryption. The article reports no new victim compromise or operational impact from the emulation.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| SHA256 | 8d2581e5cc6e6fdf17558afe025ff84d9023ea636aca74dee39900d8f523e912 | SHA-256 hash of the BlackByte ransomware sample identified as malicious and used in the emulation. |
MITRE ATT&CK
T1016 · System Network Configuration DiscoveryThe emulation uses the ARP table to perform network reconnaissance.T1053.005 · Scheduled TaskThe emulation runs the ransomware by creating and triggering a scheduled task.T1105 · Ingress Tool TransferThe emulation saves a BlackByte ransomware sample to disk to test delivery of the malicious sample.T1112 · Modify RegistryThe emulation modifies registry values, including EnableLinkedConnections and Windows time-format settings.T1486 · Data Encrypted for ImpactThe emulation encrypts files using AES-128 and RSA-1024.T1490 · Inhibit System RecoveryThe emulation deletes Volume Shadow Copies to inhibit system recovery before encryption.T1562.001 · Disable or Modify ToolsThe emulation modifies Windows Defender settings and exclusions and disables Controlled Folder Access.T1562.004 · Disable or Modify System FirewallThe emulation disables local Windows Firewall profiles and modifies firewall rule groups.
Threat Actors
Malware
Vendors
Products
AEV PlatformAttackIQ released an emulation (AEV Platform) that reproduces BlackByte TTPs to validate security controls, including scheduled task execution, Defender and firewall tampering, and file encryption.Windows DefenderThe emulation reproduces execution via scheduled tasks, disabling and excluding Windows Defender and firewall profiles, ARP discovery, shadow copy deletion, and AES/RSA file encryption to test defensive controls.
Countries
Industries
Energycritical infrastructure sectors such as Government, Financial Services, Manufacturing, and Energy.Financial Servicescritical infrastructure sectors such as Government, Financial Services, Manufacturing, and Energy.Governmentcritical infrastructure sectors such as Government, Financial Services, Manufacturing, and Energy.Manufacturingcritical infrastructure sectors such as Government, Financial Services, Manufacturing, and Energy.