
uCreator Android Spyware Can Steal Telegram 2FA Passwords and Clone WeChat Accounts
Summary
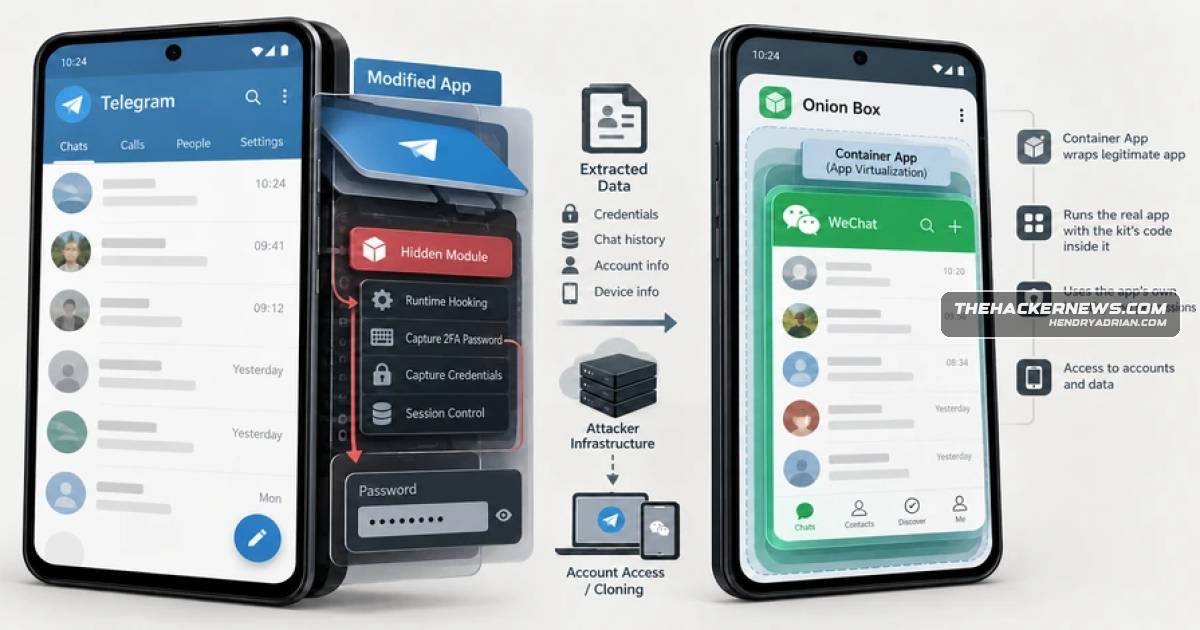
Researchers found the rentable uCreator Android kit can steal Telegram 2FA passwords and clone WeChat accounts through tampered apps or a container. Its code exposes a multi-customer backend; victim impact and some operator links remain unconfirmed.
Key points
- Ovi found that uCreator can be installed through tampered apps distributed outside official stores or run WeChat inside its Onion Box container; how every victim was infected is unknown.
- In tampered Telegram apps, the kit hooks the login process to capture the 2FA password in readable form and can query the app's message store for chat history.
- The Telegram code can manipulate sessions, phone numbers or accounts, and hide an attacker's session from the device list shown by the tampered app.
- For WeChat, the kit can copy login identity, package and upload app data, and use a login script to clone an account. Ovi says this targets the account, not its chat history.
- Ovi found a rented backend with customer-specific commands and scheduling designed to manage activity across controlled and victim phones. The code shows capabilities, not that every step was used against victims.
- Ovi found code similarities between uCreator's Telegram component and Baohuo, including a namespace, C2 server and command names; whether the kit makers or a customer ran Doctor Web's earlier campaign is unclear.
- On a Pixel 10 Pro running Android 17, uCreator's hooking engine could not find an Android function it relies on, but Frida could still hook apps; this does not establish that Android 17 blocks the attack.
Article Details
- Attack Vectors
- Tampered Telegram and Telegram X copies are distributed outside official app stores through sideloading, fake app-store sites, and in-app ads; Ovi also identified social engineering, though he could not confirm the infection route for every victim.
- A container app called 洋葱盒子 (Onion Box) can run WeChat inside a virtualized environment.
- After installation, tampered apps download code for their target app and run it under that app's identity and permissions.
- The kit hooks Telegram's two-step verification flow to capture the password before it is hashed, and can manipulate account sessions and settings.
- For WeChat, the kit can copy login identity data, zip and upload app data, and use a bundled script to clone the account.
- Defensive Notes
- Ovi identified TgJarPine.dex in the assets of some tampered Telegram copies as a phone-side trace.
- Ovi also identified cache/lspatch/origin/*.apk as a trace left by LSPatch, but noted it may also appear in apps patched for other reasons.
- Ovi said the kit's hooking engine could not find a relied-on internal Android function on a Pixel 10 Pro running Android 17; he described this as extra work for the kit's makers, not proof that Android 17 blocks the attack.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 121[.]37[.]194[.]194 | IP address still associated with the kit's version-upload server when The Hacker News checked DNS records on October 23, 2026. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelFor WeChat, the kit zips app data and uploads it; Doctor Web also reported Baohuo sending account details to its server.T1056 · Input CaptureThe kit hooks Telegram's two-step verification flow to copy the password in readable form before the app hashes it.T1098 · Account ManipulationThe code can reset logged-in sessions, change the linked phone number, or delete a Telegram account.T1105 · Ingress Tool TransferTampered apps download code for the target app after installation.T1409The kit can issue database queries to a Telegram app's message store and retrieve chat history.
People
Malware
BaohuoThe kit's Telegram part matches Baohuo, a backdoor that Doctor Web reported in October 2025. Doctor Web found Baohuo in tampered copies of Telegram X, an Android app from Telegram. At the time, the company estimatedFjordPhantomEarlier Android malware has also run legitimate apps with attacker code inside them. FjordPhantom did this to banking apps through virtualization in 2023, and so did the GodFather banking trojan in 2025.GodFatherEarlier Android malware has also run legitimate apps with attacker code inside them. FjordPhantom did this to banking apps through virtualization in 2023, and so did the GodFather banking trojan in 2025.uCreatorA rentable Android spyware kit called uCreator takes over Telegram and WeChat accounts by hiding its code inside working copies of the two apps, researcher Ovi found. It only reaches people who install one of these
Products
AndroidA rentable Android spyware kit called uCreator takes over Telegram and WeChat accounts by hiding its code inside working copies of the two apps, researcher Ovi found. It only reaches people who install one of theseTelegramA rentable Android spyware kit called uCreator takes over Telegram and WeChat accounts by hiding its code inside working copies of the two apps, researcher Ovi found. It only reaches people who install one of theseTelegram Xa backdoor that Doctor Web reported in October 2025. Doctor Web found Baohuo in tampered copies of Telegram X, an Android app from Telegram. At the time, the company estimated that more than 58,000 devices wereWeChatA rentable Android spyware kit called uCreator takes over Telegram and WeChat accounts by hiding its code inside working copies of the two apps, researcher Ovi found. It only reaches people who install one of theseWeComstill unconfirmed, are users of mobile wallets and messaging apps in China and Southeast Asia, including WeCom, QQ, WhatsApp, LINE, Zalo, KakaoTalk, Viber, GCash and MoMo. He found code supporting about 20 apps, butYingGaiThe makers' own name for the product is YingGai, and the product line appears in records dating back to September 2021. The samples Ovi studied date from 2024 to July 2026.
Tools
FridaAnother tool, Frida, could still hook apps the same way on that phone. Ovi therefore describes this as extra work for the kit's makers, not proof that Android 17 blocks the attack.LSPatchTgJarPine.dex, in the assets of some tampered Telegram copies. The other is the original app copy that LSPatch, an off-the-shelf patching tool, leaves at cache/lspatch/origin/*.apk.
Countries
BrazilThe sites' banners were available only in Portuguese, for users in Brazil, and in Indonesian. Even so, Doctor Web's 2025 map of infected devices by country put India first, at 22.8%, ahead of Brazil at 20.5% andChinaOvi got access to one of the kit's command servers. It held data on victims apparently located in China and the United States, but not enough for a reliable count. He calls his report "an analysis of technicalIndiafor users in Brazil, and in Indonesian. Even so, Doctor Web's 2025 map of infected devices by country put India first, at 22.8%, ahead of Brazil at 20.5% and Indonesia at 9.6%.IndonesiaWeb's 2025 map of infected devices by country put India first, at 22.8%, ahead of Brazil at 20.5% and Indonesia at 9.6%.United Statesto one of the kit's command servers. It held data on victims apparently located in China and the United States, but not enough for a reliable count. He calls his report "an analysis of technical capability, not a