
Apple patches older iPhones and iPads against Coruna-exploited flaws
Summary
Apple backported iOS/iPadOS fixes for kernel and WebKit flaws exploited by the Coruna exploit kit, covering older devices on versions 15.8.7 and 16.7.15. CISA also directed federal agencies to patch.
Key points
- Apple backported fixes for older iPhones and iPads that cannot update to the latest iOS version.
- The patches address CVE-2023-41974, CVE-2023-43000, CVE-2023-43010, and CVE-2024-23222, affecting kernel and WebKit components.
- Affected devices include older iPhone, iPad, and iPod touch models running iOS/iPadOS 15.8.7 or 16.7.15.
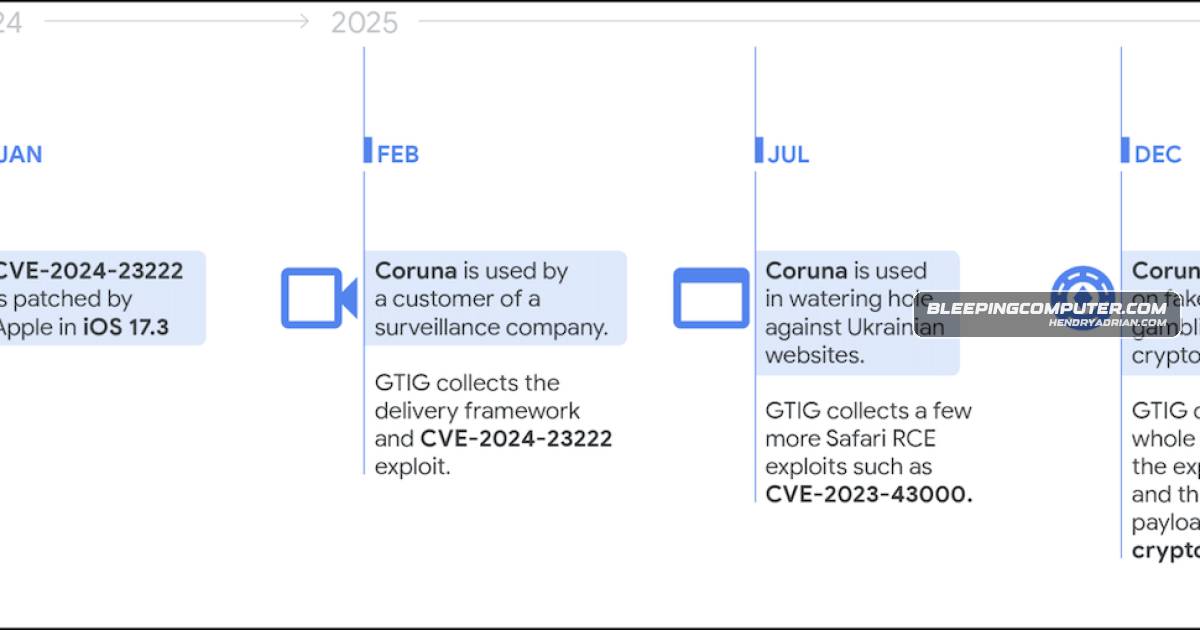
- The flaws were targeted in exploit chains associated with the Coruna exploit kit; the article says some were used in zero-day attacks.
- Google GTIG linked Coruna to multiple threat groups, including suspected state-backed UNC6353 and financially motivated UNC6691; UNC6691 was reported to use it on fake gambling and crypto sites to steal cryptocurrency wallets.
- CISA added three Coruna-targeted vulnerabilities to its Known Exploited Vulnerabilities catalog and directed federal agencies to patch by March 26.
Article Details
- Vulnerability Types
- Kernel use-after-free
- WebKit type confusion
- WebKit use-after-free
- Affected Versions
- iOS 15.8.7
- iOS 16.7.15
- iPadOS 15.8.7
- iPadOS 16.7.15
- Exploitation Status
- reported
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
T1068 · Exploitation for Privilege EscalationThe article says exploit chains targeted vulnerabilities to help attackers escalate permissions to kernel privileges.T1189 · Drive-by CompromiseUNC6691 reportedly deployed the Coruna exploit kit on fake gambling and crypto websites to deliver malware payloads to visitors' devices.T1203 · Exploitation for Client ExecutionThe Coruna exploit kit used vulnerabilities in iOS devices, including WebKit flaws, to target devices and deliver malware payloads.
CVE
CVE-2023-41974Apple · iOS and iPadOSThe updates address kernel and WebKit flaws including CVE-2023-41974, CVE-2023-43000, CVE-2023-43010, and CVE-2024-23222.CVE-2023-43000Apple · iOS and iPadOS; Apple · macOS; +1 moreThe updates address kernel and WebKit flaws including CVE-2023-41974, CVE-2023-43000, CVE-2023-43010, and CVE-2024-23222.CVE-2023-43010Apple · iOS and iPadOS; Apple · macOS; +15 moreThe updates address kernel and WebKit flaws including CVE-2023-41974, CVE-2023-43000, CVE-2023-43010, and CVE-2024-23222.CVE-2024-23222Apple · iOS and iPadOS; Apple · macOS; +3 moreThe updates address kernel and WebKit flaws including CVE-2023-41974, CVE-2023-43000, CVE-2023-43010, and CVE-2024-23222.CVE-2026-20700Apple · iOS and iPadOS; Apple · macOS; +3 moreSince the start of the year, Apple has also fixed a zero-day vulnerability (CVE-2026-20700) exploited in an “extremely sophisticated attack” targeting specific individuals and allowing threat actors to execute arbitrary
Threat Actors
UNC6353Google GTIG linked Coruna to UNC6353, described as a suspected Russian state-backed hacking group.UNC6691Google GTIG linked Coruna to UNC6691, described as a financially motivated Chinese threat actor. It was reportedly seen deploying Coruna on fake gambling and crypto websites to deliver payloads that stole cryptocurrency wallets.
Vendors
Products
iOSAffected devices include models running iOS/iPadOS 15.8.7 and 16.7.15 such as iPhone 6s through iPhone X and several older iPad models.iPadAffected devices include models running iOS/iPadOS 15.8.7 and 16.7.15 such as iPhone 6s through iPhone X and several older iPad models.iPadOSAffected devices include models running iOS/iPadOS 15.8.7 and 16.7.15 such as iPhone 6s through iPhone X and several older iPad models.iPhoneAffected devices include models running iOS/iPadOS 15.8.7 and 16.7.15 such as iPhone 6s through iPhone X and several older iPad models.iPod touchiPad Air 2, iPad mini (4th generation), iPod touch (7th generation), iPad 5th generation, iPad Pro 9.7-inch, and iPad Pro 12.9-inch 1st generation