
Infoblox Maps Casino Sites Used for Money Laundering, Scams and PeckBirdy Espionage
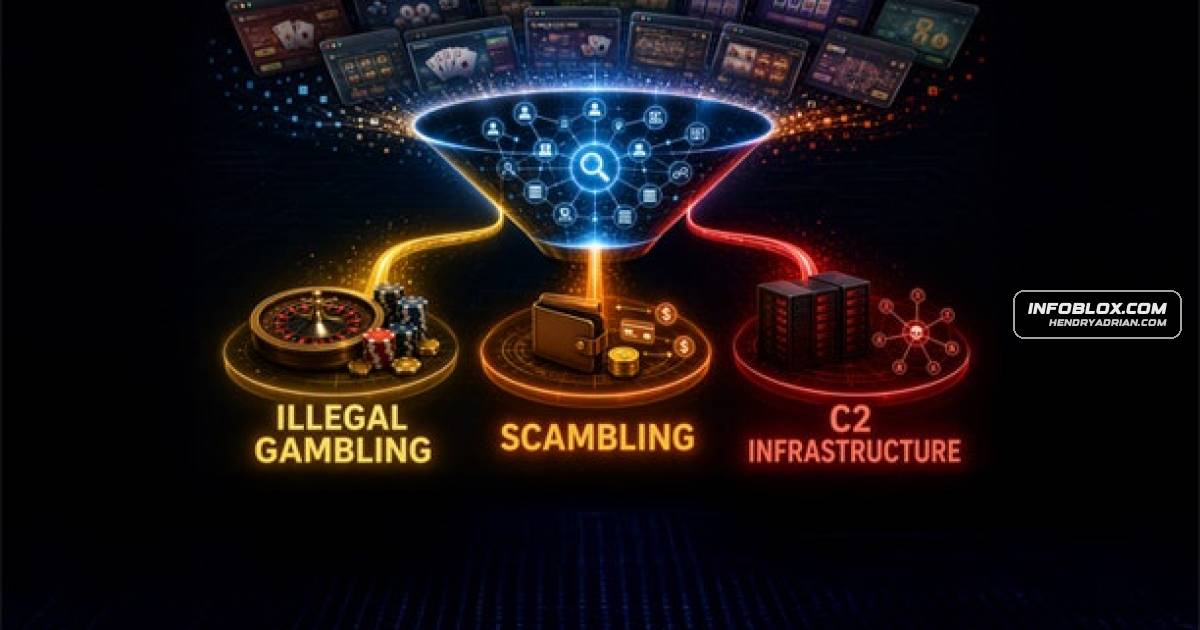
Summary
Infoblox analyzes three casino-site ecosystems: illegal Chinese-language gambling tied to laundering, scam gambling sites, and decoys hiding PeckBirdy C2. It reports infrastructure trends, detection gaps and network signals defenders can use to triage possible exposure.
Key points
- Infoblox tracks more than 1.7 million Chinese-language casino domains; it attributes about 81% of the tracked population to the FUNNULL and Vigorish Viper networks.
- The report distinguishes illegal gambling and money-laundering sites from scam gambling sites that offer bonuses but may prevent customers from withdrawing winnings.
- Infoblox says China-aligned APT groups have hidden PeckBirdy C2 infrastructure in casino and adult websites since 2023, including through JavaScript and WebSocket connections.
- As of August 31, 2026, Infoblox reported zero VirusTotal detections for mcp-source[.]online, compared with three for cache-mcp[.]com and 13 for cache-cdn[.]org.
- Just over 3% of Infoblox enterprise customers in its telemetry resolved at least one PeckBirdy C2 domain. The report says contact with multiple distinct C2 domains is more concerning than a single query, which may reflect a typo.
- Infoblox advises defenders not to dismiss alerts involving Chinese-language casino or adult domains without checking for C2 activity; repeated resolution of distinct C2 domains should be treated as a potential compromise signal.
Article Details
- Publisher
- Infoblox Threat Intel
- Report Period
- Infrastructure observations from January 2021 through August 2026; VirusTotal results reported as of August 31, 2026.
- Scope
- Analysis of illegal Chinese-language casino sites, scam gambling sites, and PeckBirdy C2 decoys, including infrastructure and enterprise DNS telemetry.
- Sample Size
- Tracked populations include more than 1.7 million Chinese-language casino domains, thousands of scambling domains, and dozens of PeckBirdy decoy domains.
- Key Statistics
- Infoblox tracks more than 1.7 million illegal Chinese-language casino domains.
- FUNNULL and Vigorish Viper were associated with 745,148 and 666,157 domains, respectively—about 81% of the tracked Chinese-language casino population.
- UNODC estimated global illegal betting revenue at up to $1.7 trillion annually.
- UNODC estimated transnational online scam losses across East Asia, Southeast Asia, Australia, and New Zealand at $88.3–$114.1 billion in 2025, compared with $18–$37 billion in 2023.
- Just over 3% of Infoblox enterprise customers resolved at least one PeckBirdy C2 domain.
- Recommendations
- Investigate casino and adult-domain alerts for embedded C2 payloads before dismissing them as employee browsing violations.
- Treat repeated resolutions of multiple distinct PeckBirdy C2 domains as a potential compromise; a single githubassets[.]net resolution may reflect a typo and is a weaker signal.
- Do not rely on domain blocking as a standalone response to the casino infrastructure, since operators rotate domains when existing ones are blocked.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 11168833[.]com | Listed as a sample illegal Chinese-language casino domain; the report associates this population with illegal gambling and money laundering. |
| DOMAIN | 11170011[.]com | Listed as a sample illegal Chinese-language casino domain; the report associates this population with illegal gambling and money laundering. |
| DOMAIN | 1862[.]cc | Illegal Chinese-language casino domain that redirected visitors to IP addresses hosting exact copies of the site. |
| DOMAIN | 312zym001[.]cc | Listed as a sample illegal Chinese-language casino domain; the report associates this population with illegal gambling and money laundering. |
| DOMAIN | 80074[.]cc | Listed as a sample illegal Chinese-language casino domain; the report associates this population with illegal gambling and money laundering. |
| DOMAIN | 843470[.]cc | Listed as a sample illegal Chinese-language casino domain; the report associates this population with illegal gambling and money laundering. |
| DOMAIN | am125[.]cc | Listed as a sample illegal Chinese-language casino domain; the report associates this population with illegal gambling and money laundering. |
| DOMAIN | appcasino[.]online | Domain to which the scambling site dragobet[.]net redirects most clicks. |
| DOMAIN | asg78[.]com | PeckBirdy decoy domain that loaded a suspicious JavaScript payload resembling prior PeckBirdy payloads. |
| DOMAIN | cache-cdn[.]org | PeckBirdy C2 domain referenced in prior Trend Micro reporting; Infoblox reported 13 VirusTotal detections as of August 31, 2026. |
| DOMAIN | cache-mcp[.]com | PeckBirdy C2 domain associated with a suspicious JavaScript payload and technical fingerprints linking it to other PeckBirdy C2 domains. |
| DOMAIN | dollycasino[.]com | Listed as a scambling domain; the report cites complaints about users being unable to cash out winnings. |
| DOMAIN | dragobet[.]net | Scambling domain promoted through comment spam injected across numerous websites. |
| DOMAIN | mcp-source[.]online | PeckBirdy C2 endpoint used for data collection over WebSocket connections; the report recorded zero VirusTotal detections as of August 31, 2026. |
| DOMAIN | puqxr[.]com | Listed as a sample illegal Chinese-language casino domain; the report associates this population with illegal gambling and money laundering. |
| DOMAIN | realz[.]com | Listed as a scambling domain; the report describes its deposit-bonus gambling site. |
| DOMAIN | storebet77[.]support | Listed as a scambling domain featuring Joker casino branding. |
| DOMAIN | summer138[.]fit | Listed as a scambling domain featuring Joker casino branding. |
| DOMAIN | vip311[.]cc | PeckBirdy decoy domain that embeds a PeckBirdy C2 domain behind casino branding. |
| DOMAIN | zenplay77-x[.]space | Listed as a sample illegal Chinese-language casino domain; the report associates this population with illegal gambling and money laundering. |
| DOMAIN | zzyud[.]com | Listed as a sample illegal Chinese-language casino domain; the report associates this population with illegal gambling and money laundering. |
| IPV4 | 146[.]103[.]91[.]133 | Final destination IP for visitors accessing 1862[.]cc with a Japanese IP address; hosted an exact copy of the illegal casino site. |
| IPV4 | 157[.]185[.]143[.]150 | Final destination IP for visitors accessing 1862[.]cc with a Hong Kong IP address; hosted an exact copy of the illegal casino site. |
MITRE ATT&CK
People
Threat Actors
FUNNULLTracked as one of the largest Chinese-language casino clusters; the report associates its infrastructure with illegal gambling and money laundering and attributes 745,148 tracked domains to it.Sable SquirrelReportedly uses casino and streaming sites as malware C2 infrastructure; the article says it controls more than 10,000 domains and estimates it spent $7 million on expired domains.Vigorish ViperTracked as one of the largest Chinese-language casino networks associated with illegal gambling and money laundering; Infoblox attributes 666,157 tracked domains to the network.
Vendors
AkamaiAkamai TechnologiesAmazonhosting companies (Amazon, Microsoft, Cloudflare, and Google) continue to host portions of the observed infrastructure associated with these casino operations.Cloudflarehosting companies (Amazon, Microsoft, Cloudflare, and Google) continue to host portions of the observed infrastructure associated with these casino operations.CTG Serverhosts, they are using a wide range of Asian hosting providers including the known bulletproof hosting ASN, CTG Server (myctgs[.]com).GoogleIf you search this domain “dragobet[.]net” on Google it quickly becomes clear that someone ran a blackhat SEO campaign spamming websites all over the internet with this domain earlier this year (Figure 10).Microsofthosting companies (Amazon, Microsoft, Cloudflare, and Google) continue to host portions of the observed infrastructure associated with these casino operations.
Tools
PeckBirdyThat last category is used by little-known China-aligned advanced persistent threat (APT) actors operating since 2023 using a C2 framework known as PeckBirdy to attack corporate and government targets across Asia.urlscan.ioLive PeckBirdy casino domains can be found through this URLscan query for the cache-mcp[.]com C2 domain—open them only if you understand the risks.VirusTotalWe also documented a C2 domain being used by the PeckBirdy framework that had zero detections on VirusTotal at the time of this publication.
Countries
Australiathey estimated losses from transnational online scam operations across East Asia, Southeast Asia, Australia, and New Zealand at $88.3 billion to $114.1 billion for 2025 alone, roughly three times the $18–37Chinathree major purposes hiding behind most illicit online casino sites: facilitating illegal gambling across China and Asia, and laundering money; stealing money from customers or preventing them from cashing outNew Zealandlosses from transnational online scam operations across East Asia, Southeast Asia, Australia, and New Zealand at $88.3 billion to $114.1 billion for 2025 alone, roughly three times the $18–37 billion estimated forNorth KoreaIt supports the movement of money out of China and other Asian jurisdictions to avoid taxes and oversight, and North Korea uses it to launder proceeds from its online criminal operations.PhilippinesThe UNODC report also highlighted that the Philippines ordered more than 7,000 illegal gambling websites blocked in 2024, which had limited effect and was described as “practical futility.”SingaporeThe counts are small, and the mix leans toward Hong Kong, mainland China and Singapore (Starcloud Global) hosts alongside Cloudflare, Microsoft, Amazon and Akamai.United StatesBut as we explain throughout this research, these websites are being registered and hosted with U.S.
Industries
BankingThese Chinese-language online casinos are one leg of the Asian underground banking economy operating across over 1.7 million domains.EducationWhen we look at the industries that are targeted, education has been a top target, which aligns to previous Trend Micro reporting about a July 2024 attack on a Philippines education institution.Financial ServicesWe have also seen IT, banking, financial services, and government as top targets, but also broad potential targeting of other industries.GovernmentThat last category is used by little-known China-aligned advanced persistent threat (APT) actors operating since 2023 using a C2 framework known as PeckBirdy to attack corporate and government targets across Asia.online gamblingMany security teams ignore online gambling and casino domains, especially Chinese-language websites.