
Analysis Finds 54 EDR Killers Using 34 Vulnerable Drivers to Disable Security
Summary
An ESET analysis found 54 of nearly 90 identified EDR killers use BYOVD to abuse 34 vulnerable drivers, gain kernel access and disable endpoint protections before ransomware encryption.
Key points
- ESET found that 54 of nearly 90 identified EDR-killer tools abuse 34 vulnerable drivers using BYOVD.
- Kernel-level access can let these tools terminate EDR processes, disable security tools and tamper with kernel callbacks.
- The tools are developed by closed ransomware groups, proof-of-concept code forkers and underground-market sellers.
- Other approaches include administrative scripts, anti-rootkit utilities and driverless tools that block EDR network traffic.
- ESET says sophisticated evasion has shifted toward EDR-killer components, while encryptors remain noisy.
- Blocking commonly abused drivers can help, but ESET recommends layered monitoring and response throughout the attack lifecycle.
Article Details
- Event Type
- Security research finding: analysis identified 54 EDR-killer tools using BYOVD to exploit 34 vulnerable signed drivers.
- Impact
- BYOVD can provide kernel-mode privileges that attackers use to terminate EDR processes and disable endpoint protections before ransomware encryption. The article reports no specific victims or quantified incident impact.
MITRE ATT&CK
T1068 · Exploitation for Privilege EscalationThe article says BYOVD tools exploit vulnerable drivers to gain elevated, kernel-mode privileges.T1486 · Data Encrypted for ImpactThe article describes ransomware encrypting files after security protections are disabled.T1562.001 · Disable or Modify ToolsEDR killers terminate EDR processes and disable security tools to impair defenses.
People
Threat Actors
Malware
Vendors
ESETof their encryptors, and ensuring that each new build is reliably undetected can be time-consuming,” ESET researcher Jakub SouÄek said in a report shared with The Hacker News.MicrosoftThe result is an abuse of Microsoft’s driver trust model to evade defenses, taking advantage of the fact that the vulnerable driver is legitimate and signed.
Products
Tools
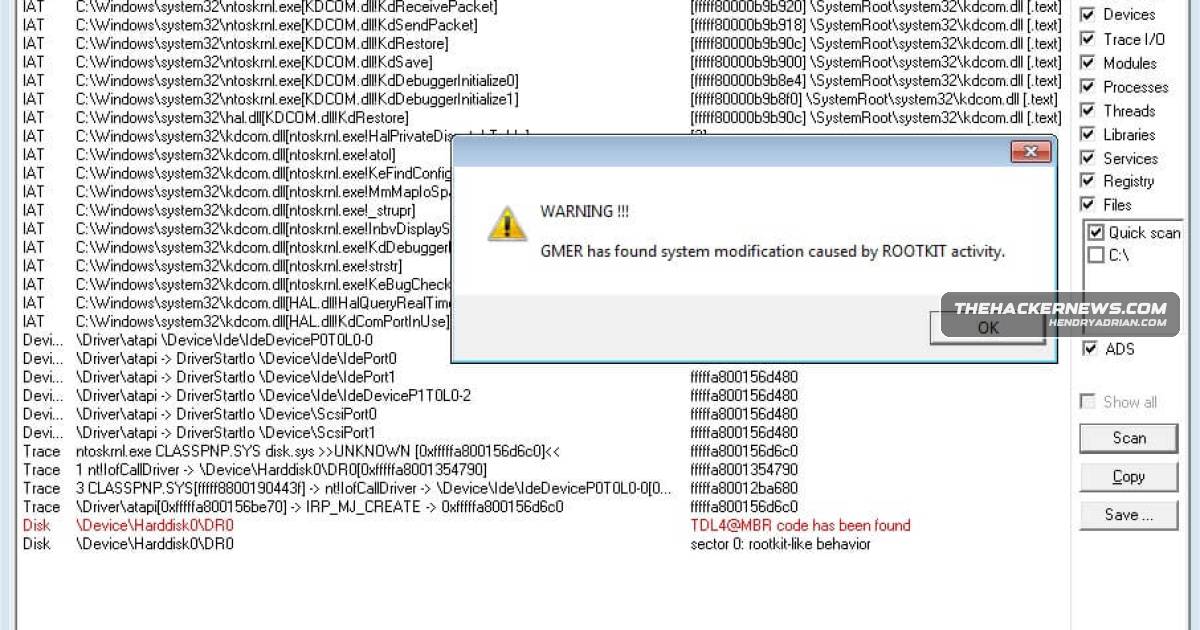
ABYSSWORKER(e.g., SmilingKiller, TfSysMon-Killer), and marketplace sellers (e.g., DemoKiller/ÐаÑомеÑ, ABYSSWORKER, CardSpaceKiller).CardSpaceKillerTfSysMon-Killer), and marketplace sellers (e.g., DemoKiller/ÐаÑомеÑ, ABYSSWORKER, CardSpaceKiller).DemoKillerThese tools are developed by closed ransomware groups, proof-of-concept forkers, and marketplace sellers and include examples such as DemoKiller, EDRSilencer, and the Reynolds ransomware.EDR-FreezeVariants include script-based killers, anti-rootkit utilities (GMER, HRSword, PC Hunter), and driverless tools like EDRSilencer and EDR-Freeze.EDRSilencerThese tools are developed by closed ransomware groups, proof-of-concept forkers, and marketplace sellers and include examples such as DemoKiller, EDRSilencer, and the Reynolds ransomware.GMERVariants include script-based killers, anti-rootkit utilities (GMER, HRSword, PC Hunter), and driverless tools like EDRSilencer and EDR-Freeze.HRSwordVariants include script-based killers, anti-rootkit utilities (GMER, HRSword, PC Hunter), and driverless tools like EDRSilencer and EDR-Freeze.PC HunterVariants include script-based killers, anti-rootkit utilities (GMER, HRSword, PC Hunter), and driverless tools like EDRSilencer and EDR-Freeze.SmilingKillerThree developer types produce these tools: closed gangs (e.g., DeadLock, Warlock), POC forkers (e.g., SmilingKiller, TfSysMon-Killer), and marketplace sellers (e.g., DemoKiller/ÐаÑомеÑ, ABYSSWORKER,TfSysMon-Killertypes produce these tools: closed gangs (e.g., DeadLock, Warlock), POC forkers (e.g., SmilingKiller, TfSysMon-Killer), and marketplace sellers (e.g., DemoKiller/ÐаÑомеÑ, ABYSSWORKER, CardSpaceKiller).