Warden Stealer Targets AI Agent Data and Bypasses Browser Encryption
Summary
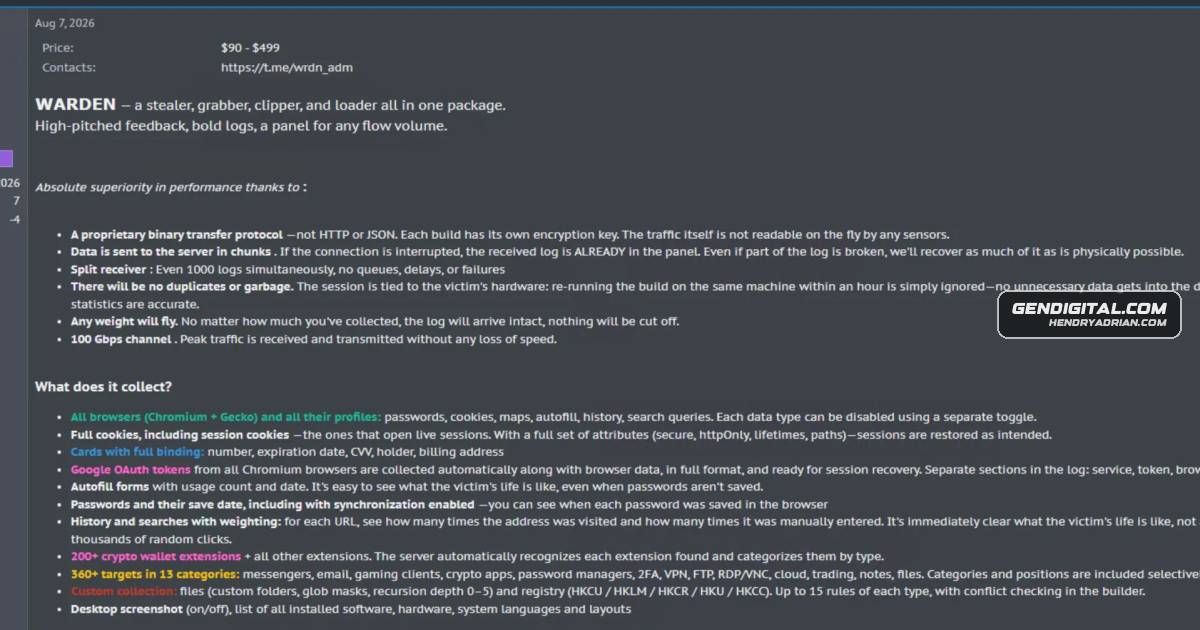
Gen Threat Labs analyzes Warden Stealer, a rapidly spreading Rust infostealer that targets AI agent data, steals browser credentials by bypassing Application-Bound Encryption, and includes a loader and cryptocurrency clipper.
Key points
- Warden Stealer is a Rust-based malware-as-a-service that has become one of the most prevalent infostealers in Gen Digital’s user base.
- It can steal configuration and local data from AI assistants and coding agents, potentially exposing tokens, credentials, conversation histories, and project information.
- The malware includes a loader that can inject its payload into another process, as well as a cryptocurrency clipper.
- Its loader and stealer use extensive obfuscation, code morphing, and anti-virtual-machine checks to hinder detection and analysis.
- To bypass Chromium Application-Bound Encryption, it locates an encrypted browser key in memory and injects shellcode into the browser process to decrypt it.
- Operators distribute the malware through methods including cracked software, game cheats, malvertising, and ClickFix campaigns; the malware can also download and run additional payloads.
Article Details
- Attack Vectors
- Operators distribute Warden Stealer through supposedly cracked software, game cheats, malvertising, and ClickFix campaigns.
- The loader can inject the stealer payload into a running process, sideload it as a DLL alongside a signed executable, or be omitted for standalone execution.
- Warden Stealer steals browser data and local AI-agent data, including tokens, credentials, prompt histories, and conversation databases.
- The malware can download and execute additional payloads from URLs supplied in its dynamic configuration.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | backtoblack7[.]com | Extracted Warden Stealer C2 domain. |
| DOMAIN | berff3788[.]com | Extracted Warden Stealer C2 domain. |
| DOMAIN | bobroviysmex[.]shop | Extracted Warden Stealer C2 domain. |
| DOMAIN | bomboclat[.]rest | Extracted Warden Stealer C2 domain. |
| DOMAIN | brodyagup[.]com | Extracted Warden Stealer C2 domain. |
| DOMAIN | culture-shock[.]club | Extracted Warden Stealer C2 domain. |
| DOMAIN | diseazhjw[.]cloud | Extracted Warden Stealer C2 domain. |
| DOMAIN | dojaekrt[.]cc | Extracted Warden Stealer C2 domain. |
| DOMAIN | dojaekrt[.]forum | Extracted Warden Stealer C2 domain. |
| DOMAIN | dojaekrt[.]trade | Extracted Warden Stealer C2 domain. |
| DOMAIN | erifytrtr1[.]vip | Extracted Warden Stealer C2 domain. |
| DOMAIN | ggresp[.]com | Extracted Warden Stealer C2 domain. |
| DOMAIN | hotelcalifornia[.]club | Extracted Warden Stealer C2 domain. |
| DOMAIN | hroffice[.]work | Extracted Warden Stealer C2 domain. |
| DOMAIN | incoming[.]rent | Extracted Warden Stealer C2 domain. |
| DOMAIN | jgkawdq[.]cloud | Extracted Warden Stealer C2 domain. |
| DOMAIN | kaiangelsystems[.]rest | Extracted Warden Stealer C2 domain. |
| DOMAIN | kaifdlyaw[.]com | Extracted Warden Stealer C2 domain. |
| DOMAIN | kaliop-weda[.]club | Extracted Warden Stealer C2 domain. |
| DOMAIN | konradkerz40000[.]work | Extracted Warden Stealer C2 domain. |
| DOMAIN | library2000[.]com | Extracted Warden Stealer C2 domain. |
| DOMAIN | luqiuid91[.]com | Extracted Warden Stealer C2 domain. |
| DOMAIN | macfilecloud8[.]com | Extracted Warden Stealer C2 domain. |
| DOMAIN | matie-bal[.]club | Extracted Warden Stealer C2 domain. |
| DOMAIN | modicontools[.]com | Extracted Warden Stealer C2 domain. |
| DOMAIN | nextlanding[.]net | Extracted Warden Stealer C2 domain. |
| DOMAIN | nweenwew234[.]cc | Extracted Warden Stealer C2 domain. |
| DOMAIN | patduggan[.]com | Extracted Warden Stealer C2 domain. |
| DOMAIN | pianolovers[.]club | Extracted Warden Stealer C2 domain. |
| DOMAIN | piska-sosidka-govno[.]asia | Extracted Warden Stealer C2 domain. |
| DOMAIN | plainhorizon[.]org | Extracted Warden Stealer C2 domain. |
| DOMAIN | publisher99[.]com | Extracted Warden Stealer C2 domain. |
| DOMAIN | rabbids-sixseven[.]cc | Extracted Warden Stealer C2 domain. |
| DOMAIN | recap-check[.]org | Extracted Warden Stealer C2 domain. |
| DOMAIN | rocks56[.]com | Extracted Warden Stealer C2 domain. |
| DOMAIN | rrrrrrrfffff[.]club | Extracted Warden Stealer C2 domain. |
| DOMAIN | russianaltushkawantdickinside[.]club | Extracted Warden Stealer C2 domain. |
| DOMAIN | sfgiantslive[.]com | Extracted Warden Stealer C2 domain. |
| DOMAIN | skibidiclipper[.]pw | Extracted Warden Stealer C2 domain. |
| DOMAIN | skibidiproliv[.]com | Extracted Warden Stealer C2 domain. |
| DOMAIN | skibidistealer[.]team | Extracted Warden Stealer C2 domain. |
| DOMAIN | systemformating[.]rest | Extracted Warden Stealer C2 domain. |
| DOMAIN | verifytrtr[.]vip | Extracted Warden Stealer C2 domain. |
| DOMAIN | vlad-nazarenko2004[.]club | Extracted Warden Stealer C2 domain. |
| DOMAIN | web03-azureupdate[.]com | Extracted Warden Stealer C2 domain. |
| DOMAIN | webex-028ue2[.]com | Extracted Warden Stealer C2 domain. |
| DOMAIN | wosback[.]cc | Extracted Warden Stealer C2 domain. |
| DOMAIN | zalupka[.]website | Extracted Warden Stealer C2 domain. |
| DOMAIN | zolotoy[.]club | Extracted Warden Stealer C2 domain. |
| DOMAIN | zxcwork[.]com | Extracted Warden Stealer C2 domain. |
| SHA256 | 006510ce1da2b7410376f0788c19e55616eb4bcc30072d25b7d0871dc32aa11c | Warden Loader malware hash. |
| SHA256 | 04beeb716a79661ea770138558dbdebccb493bf6b4b1ec37f19b9c028dea98d5 | Warden Stealer malware hash. |
| SHA256 | 0d727a4ef1178e767afdd0080ba1ebda0f24ac52b639f0501021affd8f88d26a | Warden Loader malware hash. |
| SHA256 | 159b472e0e0bdc05933da64032761cbd042b6cc5dc4e1cd11d5ef7af5180b972 | Warden Stealer malware hash. |
| SHA256 | 241df5a4ee38658329025152807fcd69b7e40361428000bb56d14cadeb48b437 | Warden Stealer build hash tracked by Gen Threat Labs from early May 2026. |
| SHA256 | 3d0794fca8ae2ca80eee463b11557d696c48c8ddf17f5e2917cc33fbf0596842 | Warden Stealer malware hash. |
| SHA256 | 51bc797e783b6a765e174736ff12a711a243099f4e19739388e5bce1548a448d | Warden Stealer malware hash. |
| SHA256 | 5b6ec081f385d91273a79c6645cd0f932539dc267863e5d243657a8ccb5ca351 | Warden Stealer malware hash. |
| SHA256 | 63959ef6309cd01b5d3c7262a3a41394dca2db2dc74bd030a517b7e23a2c3fef | Warden Loader malware hash. |
| SHA256 | 6e47d6da0e2ab2226ee033e75c7b9b41e4e908d6f71b47d0ce7477a492fb418e | Warden Stealer malware hash. |
| SHA256 | 77c8266935bc040c992ab70abd402bd203b9c12e7548c80b84fd21308c250f0e | Warden Loader malware hash. |
| SHA256 | 77cc246272f2af21b64bbc6c6173d57affee97eb0ccf747d89492d06d4c52865 | Warden Loader malware hash. |
| SHA256 | a396ccfb5547f04cef4be18ed076bb2c62c571268306d201b6177188f05723f1 | Warden Stealer malware hash. |
| SHA256 | abcc49cd8a9b08a18ad9e516ec13350e01a05f04f1c5e025080e1c0e3b4bec36 | Warden Loader malware hash. |
| SHA256 | b855f6883391e25f1a91692bef76771065b4b0436a014de5b25aa9d0de6238e4 | Warden Loader malware hash. |
| SHA256 | cc1f2ae885d317e6c520ea6d219370630c1c7a8fe600b89d0d78fdee28174ff4 | Warden Stealer malware hash. |
| SHA256 | dd1c3b2bfe32b41902ffe875e568f52f44f0900209b9cb447c9ae4444a5dce4e | Warden Loader malware hash. |
| SHA256 | e62b24142e7244573cf37cef55b175fbba6a43ac4592d30f8b061dda8866c9b9 | Warden Stealer malware hash. |
| SHA256 | ea9debbe4b3d11bf6c986af63a94e13ceb2a1cbc167a642697fcabc9e8a50439 | Warden Loader malware hash. |
| SHA256 | fea9538084b70e9681fd8104b9319792c4d8c2701ae145ec31dc26e7526f2ae0 | Warden Stealer malware hash. |
| SHA256 | ff85bb43e546fac541443006878828c47958c1d55dfa32c529651bfcc12832f1 | Warden Loader malware hash. |
MITRE ATT&CK
T1005 · Data from Local SystemWarden Stealer collects local files and data, including AI-agent configuration files, conversation histories, and project traces.T1041 · Exfiltration Over C2 ChannelThe stealer uploads collected data to its C2 server in batches.T1055.002 · Portable Executable InjectionThe loader manually maps the reconstructed stealer image into a remote process using remote memory allocation and writing.T1055.003 · Thread Execution HijackingThe ABE bypass suspends an existing browser thread and redirects its instruction pointer to shellcode that decrypts the staged key.T1059.003 · Windows Command ShellThe malware launches certutil downloads and downloaded payloads through cmd.exe commands.T1071.001 · Web ProtocolsWarden Stealer communicates with its C2 server over HTTPS using a custom binary message format.T1105 · Ingress Tool TransferWarden Stealer downloads additional payloads from configured URLs using certutil.exe.T1497.001 · System ChecksThe stealer checks firmware records, CPU and hypervisor identifiers, installed software, and display adapters to detect virtualized environments.T1552.001 · Credentials In FilesThe stealer collects credentials and tokens from local AI-agent configuration data, including MCP configurations.T1555.003 · Credentials from Web BrowsersThe stealer targets Chromium-based browser cookies and passwords and describes bypassing ABE to access protected browser data.
People
Malware
Amateralandscape and is currently one of the most prevalent infostealers in our user base (together with Vidar, Amatera, and Remus).CallbackBeaverThere, however, we referred to Warden Stealer as CallbackBeaver, since at that time we had not yet been able to attribute it to Warden Stealer and had therefore given it our own name.GoFlateLoadera massive PE overlay, a design choice intended to bypass detection (also employed, for example, by GoFlateLoader), as excessively large executables may pose challenges for some AV and EDR solutions, which, primarilyRemusis currently one of the most prevalent infostealers in our user base (together with Vidar, Amatera, and Remus).Vidarlandscape and is currently one of the most prevalent infostealers in our user base (together with Vidar, Amatera, and Remus).Warden StealerGen Threat Labs has been tracking Warden Stealer, an emerging and actively developed malware-as-a-service (MaaS) infostealer written in the Rust programming language that has, within just a few months, already become
Products
ChromiumAccording to its advertisement, Warden Stealer is supposedly capable of stealing data from all Chromium- and Gecko-based browsers, more than 200 cryptocurrency wallet extensions, and over 360 other targets across 13Claudestealing configuration files and local data belonging to AI assistants and agentic coding tools, such as Claude, Codex, Grok, and Cursor.Codexconfiguration files and local data belonging to AI assistants and agentic coding tools, such as Claude, Codex, Grok, and Cursor.Cursorand local data belonging to AI assistants and agentic coding tools, such as Claude, Codex, Grok, and Cursor.Grokfiles and local data belonging to AI assistants and agentic coding tools, such as Claude, Codex, Grok, and Cursor.Microsoft WindowsThe stealer is written in the Rust programming language and targets Windows systems from Windows 8 through Windows 11 (Figure 1 below also lists Windows 7 as supported, but support for it was dropped as of Warden