DNS Analysis Maps Infrastructure Linked to Five Ransomware Groups
Summary
Researchers analyzed 84 network indicators linked to LockBit, Cl0p, Akira, Medusa, and Qilin, examining DNS traffic and historical resolutions to identify potentially malicious domains, IPs, and other connected artifacts.
Key points
- The analysis covered 84 indicators: three subdomains, eight domains, and 73 IP addresses gathered from five ransomware-related sources.
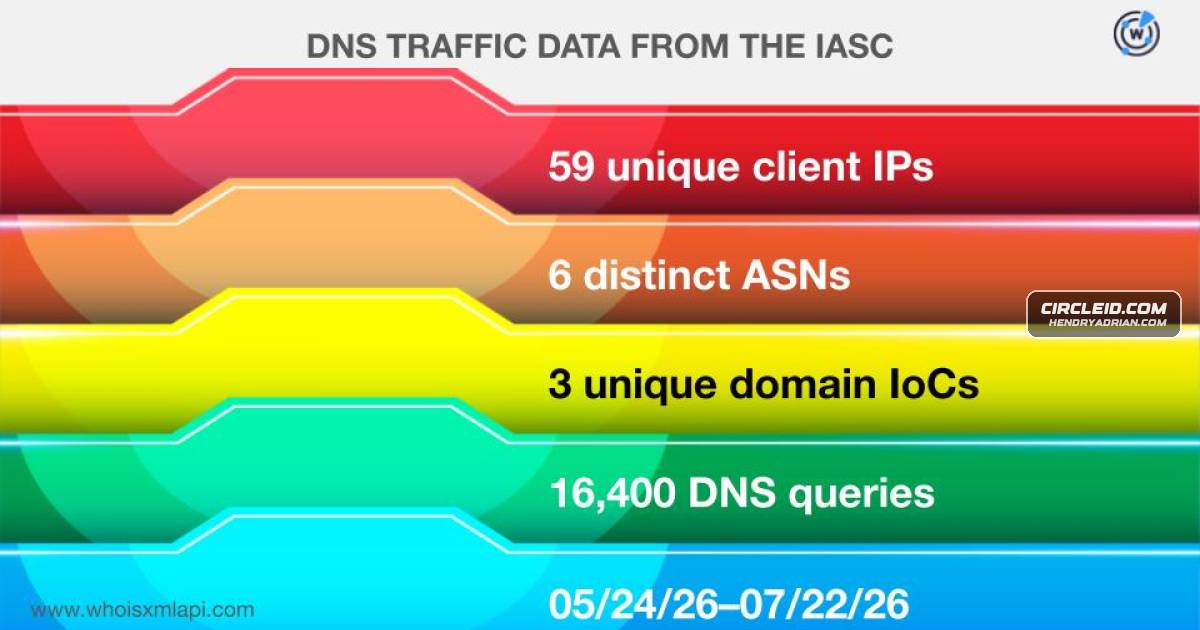
- Traffic data showed 59 client IPs queried three LockBit-related domains 16,400 times between May 24 and July 22, 2026.
- Researchers found 19,360 distinct IPs had communicated with 55 of the analyzed IP indicators; these addresses spanned 531 ASNs.
- Historical DNS data included 421 domain-to-IP resolutions for five Cl0p-related domains and 13,899 IP-to-domain resolutions for 57 IP indicators.
- Analysis of historical WHOIS email addresses produced 5,100 connected domains; two were identified as previously weaponized, including answersite[.]com, associated with malware distribution.
- The researchers caution that some entities labeled malicious may prove harmless and recommend further investigation to corroborate findings.
Article Details
- Attack Vectors
- The article identifies five domains as Cl0p-related network IoCs and reports that one additional domain was associated with malware distribution.
- Three subdomain IoCs were associated with Medusa; the article says they could have been compromised when used by Medusa threat actors, but none was categorized as malicious at the time of writing.
- The article lists IP addresses as network IoCs associated with LockBit, Cl0p, Akira, Medusa, and Qilin.
- Defensive Notes
- The article recommends conducting supplementary investigations to corroborate entities identified as threats or malicious.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | answersite[.]com | Reportedly associated with malware distribution. |
| DOMAIN | hiperfdhaus[.]com | Identified as a Cl0p-related domain IoC. |
| DOMAIN | jirostrogud[.]com | Identified as a Cl0p-related domain IoC. |
| DOMAIN | zoom[.]voyage | Identified as a Cl0p-related domain IoC. |
| HOSTNAME | erp[.]ranasons[.]com | Medusa-related subdomain IoC; the article says it could have been compromised when used, but it was not categorized as malicious at the time of writing. |
| HOSTNAME | pruebas[.]pintacuario[.]mx | Medusa-related subdomain IoC; the article says it could have been compromised when used, but it was not categorized as malicious at the time of writing. |
| HOSTNAME | wizarr[.]manate[.]ch | Medusa-related subdomain IoC; the article says it could have been compromised when used, but it was not categorized as malicious at the time of writing. |
| IPV4 | 104[.]194[.]8[.]58 | Listed as an Akira IP IoC. |
| IPV4 | 174[.]169[.]162[.]62 | Listed as a LockBit IP IoC. |
| IPV4 | 185[.]181[.]230[.]103 | Listed as a Cl0p IP IoC. |
| IPV4 | 31[.]220[.]45[.]120 | Listed as a Medusa IP IoC. |
| IPV4 | 82[.]29[.]54[.]140 | Listed as a Qilin IP IoC. |
CVE
Malware
AkiraWe zoomed into five of them—LockBit, Cl0p, Akira, Medusa, and Qilin—in a bid to know more about their network IoCs and identify new artifacts.Cl0pWe zoomed into five of them—LockBit, Cl0p, Akira, Medusa, and Qilin—in a bid to know more about their network IoCs and identify new artifacts.LockBitWe zoomed into five of them—LockBit, Cl0p, Akira, Medusa, and Qilin—in a bid to know more about their network IoCs and identify new artifacts.MedusaWe zoomed into five of them—LockBit, Cl0p, Akira, Medusa, and Qilin—in a bid to know more about their network IoCs and identify new artifacts.QilinWe zoomed into five of them—LockBit, Cl0p, Akira, Medusa, and Qilin—in a bid to know more about their network IoCs and identify new artifacts.
Tools
Bulk IP Geolocation LookupWe also queried the IP IoCs for the five ransomware on Bulk IP Geolocation Lookup and discovered that:DNS Chronicle APINext, we queried the five nonwildcard domain IoCs related to Cl0p on DNS Chronicle API and discovered that they posted 421 historical domain-to-IP resolutions over time.Domain Info APIWe queried them on WHOIS API next and filled in missing details using Domain Info API.Reverse WHOIS APIAfter querying the public email addresses on Reverse WHOIS API, we discovered 5,100 unique email-connected domains after those tagged as IoCs were filtered out.Threat Intelligence APIThreat Intelligence API queries for the email-connected domains showed that two have already been weaponized for various campaigns.WHOIS APIWe queried them on WHOIS API next and filled in missing details using Domain Info API.WHOIS History APIWe started our hunt for new artifacts by querying the domain IoCs on WHOIS History API and learned that six had 37 distinct email addresses in their historical records.WhoisXML API MCP Serverthe subdomain IoCs and filtering out those that belonged to legitimate entities aided by the WhoisXML API MCP Server, we ended up with 84 network IoCs comprising three subdomains, eight domains, and 73 IP addresses