
Tycoon2FA Adds Device-Code Phishing to Target Microsoft 365 Accounts
Summary
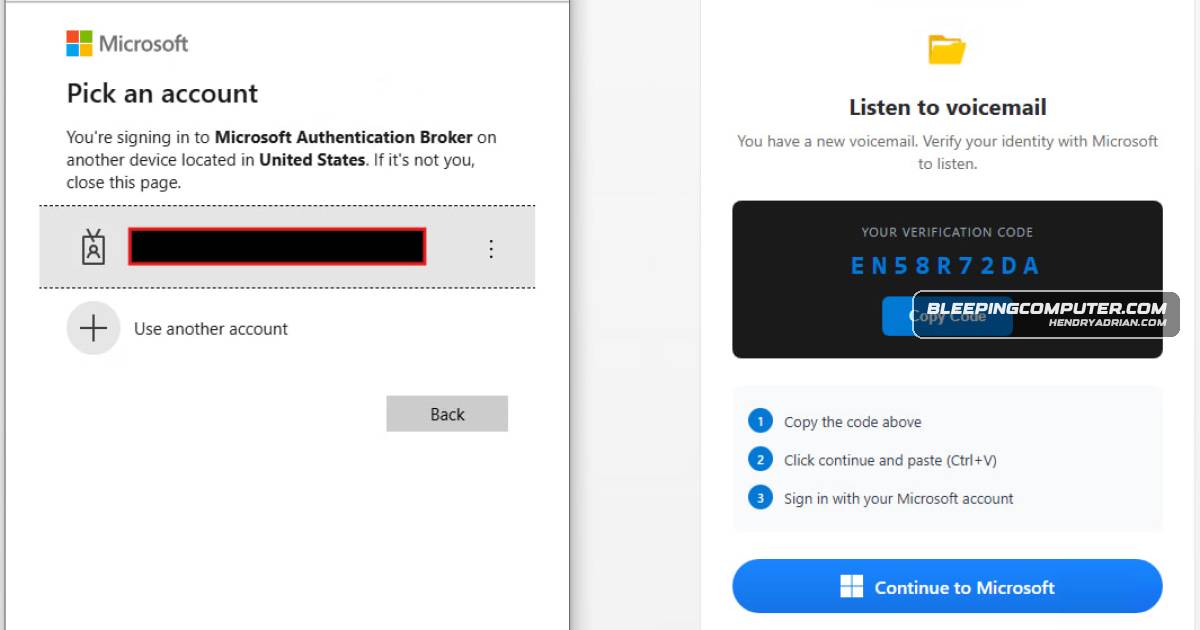
eSentire reports Tycoon2FA uses invoice-themed Trustifi tracking links and redirects to trick Microsoft 365 users into authorizing attacker-controlled devices through OAuth device-code flow. The kit has added anti-analysis defenses after a March disruption.
Key points
- eSentire describes invoice-themed emails using Trustifi click-tracking URLs to start the phishing flow.
- The chain redirects through Cloudflare Workers and obfuscated JavaScript to a fake Microsoft CAPTCHA page.
- Victims are prompted to enter an attacker-provided device code at microsoft[.]com/devicelogin; completing the flow grants OAuth tokens to an attacker-controlled device.
- The kit detects analysis tools and environments, blocks security vendors and other sources, and redirects some requests to a legitimate Microsoft page.
- Abnormal Security reported Tycoon2FA had returned to regular activity after a March law-enforcement disruption; eSentire observed the new device-code capability in late April.
- eSentire recommends disabling unused device-code flow, restricting OAuth consent, requiring admin approval for third-party apps, enforcing compliant-device policies, and monitoring Entra logs.
Article Details
- Event Type
- Tycoon2FA device-code phishing campaign targeting Microsoft 365 accounts
- Impact
- Victims who enter the attacker-provided device code and complete authentication unknowingly authorize an attacker-controlled device. The attacker receives OAuth access and refresh tokens, enabling access to victims’ Microsoft 365 data and services, including email, calendars, and cloud file storage.
MITRE ATT&CK
T1528 · Steal Application Access TokenVictims are tricked into authorizing an attacker-controlled device, allowing the attacker to obtain OAuth access and refresh tokens.T1566.002 · Spearphishing LinkThe campaign uses invoice-themed phishing emails containing Trustifi click-tracking URLs that redirect victims to a phishing page.
Vendors
CloudflareThe attack chain redirects victims through Cloudflare Workers and fake Microsoft pages.MicrosoftTycoon2FA has expanded to support device-code phishing, using Trustifi click-tracking URLs and a multi-layered redirect chain to hijack Microsoft 365 accounts.TrustifiTycoon2FA has expanded to support device-code phishing, using Trustifi click-tracking URLs and a multi-layered redirect chain to hijack Microsoft 365 accounts.
Products
Cloudflare WorkersThe attack chain redirects victims through Cloudflare Workers and fake Microsoft pages.Entra#Tycoon2FAMicrosoft 365 Apps for EnterpriseTycoon2FA has expanded to support device-code phishing, using Trustifi click-tracking URLs and a multi-layered redirect chain to hijack Microsoft 365 accounts.TrustifiTycoon2FA has expanded to support device-code phishing, using Trustifi click-tracking URLs and a multi-layered redirect chain to hijack Microsoft 365 accounts.