Konni-Linked Operation Poseidon Uses Google Ads Redirects to Deliver EndRAT
Summary
Genians analyzes a Konni-attributed spear-phishing campaign that abuses advertising redirects and compromised WordPress sites to deliver EndRAT via LNK files and AutoIt scripts, and recommends behavior-based detection and layered defenses.
Key points
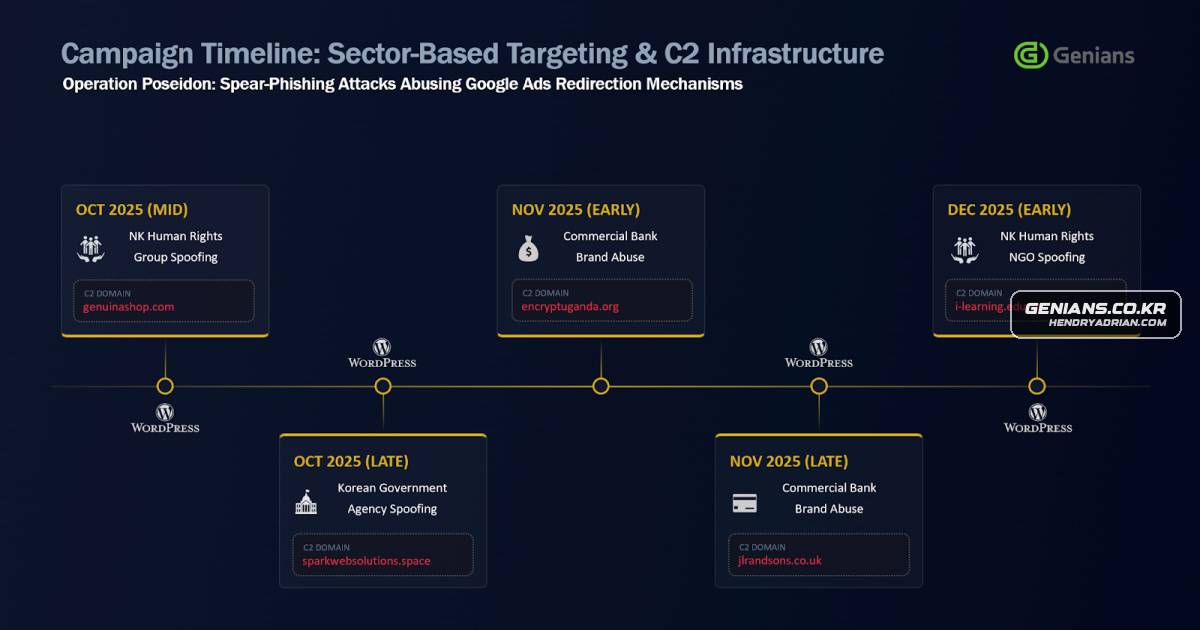
- The campaign used spear-phishing emails impersonating South Korean financial institutions and a North Korean human-rights organization.
- Attackers embedded malicious download destinations in Google advertising redirect URLs, with limited similar activity involving Naver ad tracking.
- ZIP archives contained LNK shortcuts that launched AutoIt scripts disguised as PDFs and loaded EndRAT malware into memory.
- Poorly secured WordPress sites served as malware distribution points and command-and-control infrastructure.
- Shared infrastructure, code patterns, and an exposed AutoIt build path supported attribution to Konni; the path also contained the internal name “Poseidon.”
- Email content padding and tracking pixels were used alongside sender impersonation to evade filtering and monitor recipient engagement.
- Genians recommends inspecting redirect destinations and anomalous downloads, restricting risky attachments, and using EDR behavioral detection and response.
Article Details
- Attack Vectors
- Spear-phishing emails impersonated South Korean financial institutions and human-rights organizations, using links disguised as legitimate Google or Naver advertising redirection URLs to deliver ZIP archives.
- ZIP archives contained LNK files disguised as legitimate documents; executing a shortcut launched an AutoIt script masquerading as a PDF.
- The AutoIt script downloaded and executed AutoIt3.exe and EndRAT-variant remote-access malware, including by loading malware directly into memory.
- Phishing emails used invisible, repeated English text to evade filtering and included a web beacon to track whether recipients opened the message.
- The operation used compromised WordPress websites for malware distribution and C2 infrastructure.
- Defensive Notes
- Quarantine or block unnecessary LNK attachments, including LNK files inside ZIP archives, and apply additional verification to emails impersonating financial institutions, public organizations, or human-rights groups.
- Detect suspicious post-click redirection and file downloads based on behavior and final destinations rather than blocking legitimate advertising domains outright.
- Use EDR behavior-based monitoring to identify abnormal process chains after LNK execution, including transitions to cmd.exe, powershell.exe, or AutoIt executables, and correlate process activity with network connections.
- Use EDR response capabilities to isolate suspected endpoints, collect evidence, remove malicious LNK files and ZIP archives, and scope related processes and network connections.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | aceeyl[.]com | Domain listed as C2 infrastructure for the threat activity. |
| DOMAIN | althouqroastery[.]com | Domain listed as C2 infrastructure for the threat activity. |
| DOMAIN | anupamaivf[.]com | Domain listed as C2 infrastructure for the threat activity. |
| DOMAIN | compromised-example[.]com | Shown as the malicious destination host for a sample malware-download URL. |
| DOMAIN | creativepackout[.]co | Domain listed as C2 infrastructure for the threat activity. |
| DOMAIN | encryptuganda[.]org | Domain listed as C2 infrastructure for the threat activity. |
| DOMAIN | genuinashop[.]com | Domain listed as C2 infrastructure for the threat activity. |
| DOMAIN | igamingroundtable[.]com | Domain listed as C2 infrastructure for the threat activity. |
| DOMAIN | jlrandsons[.]co[.]uk | C2 domain shared by the financial-themed and human-rights-themed attacks. |
| DOMAIN | kppe[.]pl | Threat-actor-controlled web-beacon server used to track email opens. |
| DOMAIN | kyowaind[.]co[.]jp | Domain listed as C2 infrastructure for the threat activity. |
| DOMAIN | nationalinterestparty[.]com | Domain listed as C2 infrastructure for the threat activity. |
| DOMAIN | optique-leclercq[.]be | Domain listed as C2 infrastructure for the threat activity. |
| DOMAIN | pomozzi[.]com | Domain listed as C2 infrastructure for the threat activity. |
| DOMAIN | sparkwebsolutions[.]space | Domain listed as C2 infrastructure for the threat activity. |
| DOMAIN | tatukikai[.]jp | Domain listed as C2 infrastructure for the threat activity. |
| DOMAIN | vintashmarket[.]com | Domain listed as C2 infrastructure for the threat activity. |
| HOSTNAME | appoitment[.]dotoit[.]media | Hostname listed as C2 infrastructure for the threat activity. |
| IPV4 | 109[.]234[.]36[.]135 | C2 address listed in the article's threat-indicator section. |
| IPV4 | 144[.]124[.]247[.]97 | C2 address listed in the article's threat-indicator section. |
| IPV4 | 77[.]246[.]101[.]72 | C2 address listed in the article's threat-indicator section. |
| IPV4 | 77[.]246[.]108[.]96 | C2 address listed in the article's threat-indicator section. |
| MD5 | 0171338d904381bbf3d1a909a48f4e92 | MD5 indicator listed for Operation Poseidon threat activity. |
| MD5 | 0777781dedd57f8016b7c627411bdf2c | MD5 indicator listed for Operation Poseidon threat activity. |
| MD5 | 303c5e4842613f7b9ee408e5c6721c00 | MD5 indicator listed for Operation Poseidon threat activity. |
| MD5 | 639b5489d2fb79bcb715905a046d4a54 | MD5 indicator listed for Operation Poseidon threat activity. |
| MD5 | 6a4c3256ff063f67d3251d6dd8229931 | MD5 indicator listed for Operation Poseidon threat activity. |
| MD5 | 8b8fa6c4298d83d78e11b52f22a79100 | MD5 indicator listed for Operation Poseidon threat activity. |
| MD5 | 908d074f69c0bf203ed225557b7827ec | MD5 indicator listed for Operation Poseidon threat activity. |
| MD5 | 94935397dce29684f384e57f85beeb0a | MD5 indicator listed for Operation Poseidon threat activity. |
| MD5 | a58ef1e53920a6e528dc31001f302c7b | MD5 indicator listed for Operation Poseidon threat activity. |
| MD5 | a9a52e2f2afe28778a8537f955ee1310 | MD5 indicator listed for Operation Poseidon threat activity. |
| MD5 | ad6273981cb53917cb8bda8e2f2e31a8 | MD5 indicator listed for Operation Poseidon threat activity. |
| MD5 | d4b06cb4ed834c295d0848b90a109f09 | MD5 indicator listed for Operation Poseidon threat activity. |
| MD5 | d6aa7e9ff0528425146e64d9472ffdbd | MD5 indicator listed for Operation Poseidon threat activity. |
| MD5 | f5842320e04c2c97d1f69cebfd47df3d | MD5 indicator listed for Operation Poseidon threat activity. |
MITRE ATT&CK
T1036.008 · Masquerade File TypeThe LNK and AutoIt script were disguised as legitimate financial documents or PDF files.T1059.010 · AutoHotKey & AutoITAn AutoIt script masquerading as a PDF was executed to load and run EndRAT-variant malware.T1105 · Ingress Tool TransferThe LNK-triggered activity downloaded AutoIt3.exe and a malicious AutoIt script from C2 infrastructure.T1204.002 · Malicious FileThe infection chain required a recipient to execute a downloaded LNK file from a ZIP archive.T1566.002 · Spearphishing LinkSpear-phishing emails delivered links that redirected through advertising URLs to malicious file downloads.T1584.004 · ServerThe article reports that the threat actor compromised poorly managed WordPress websites for malware distribution and C2.
Threat Actors
Malware
AutoItRATThe malicious script has been reported since around July 2025 and is classified as "EndRAT" or "AutoItRAT." It also includes a unique identifier string used during communication with the C2 server.EndRATThe EndRAT malware was loaded through the execution of an AutoIt script masquerading as a PDF file
Vendors
GeniansGenians Security Center conducted an in-depth analysis of Operation Poseidon, an attack campaign attributed to the Konni APT.GoogleGoogle announced its plan to acquire DoubleClick, an internet advertising technology company, in 2007 and completed the acquisition for approximately $3.1 billion in March 2008.NAVERMeanwhile, around May and July 2025, similar attack attempts exploiting the click-tracking domain of the NAVER advertising marketing platform (mkt.naver[.]com) were observed on a limited basis.
Products
Genian Insights EAgainst this attack flow, Genians’ integrated endpoint security platform 'Genian Insights E' can identify abnormal process trees in real time through endpoint behavior-based detection.Google AdsSince then, DoubleClick's ad click tracking and redirection technologies have been integrated into Google Ads and Google Marketing Platform (GMP), serving as core infrastructure for ad traffic delivery and performanceGoogle Marketing Platformad click tracking and redirection technologies have been integrated into Google Ads and Google Marketing Platform (GMP), serving as core infrastructure for ad traffic delivery and performance measurement.WordPressPoorly secured WordPress websites were abused as malware distribution points and C2 infrastructure