
Zimperium Details Rokarolla Android Banker’s Device-Control Capabilities
Summary
Zimperium researchers describe Rokarolla, an Android banking trojan spread via fake app sites. It abuses Accessibility and overlays to steal credentials and device data, intercept SMS and calls, and target 217 financial apps using 137 commands.
Key points
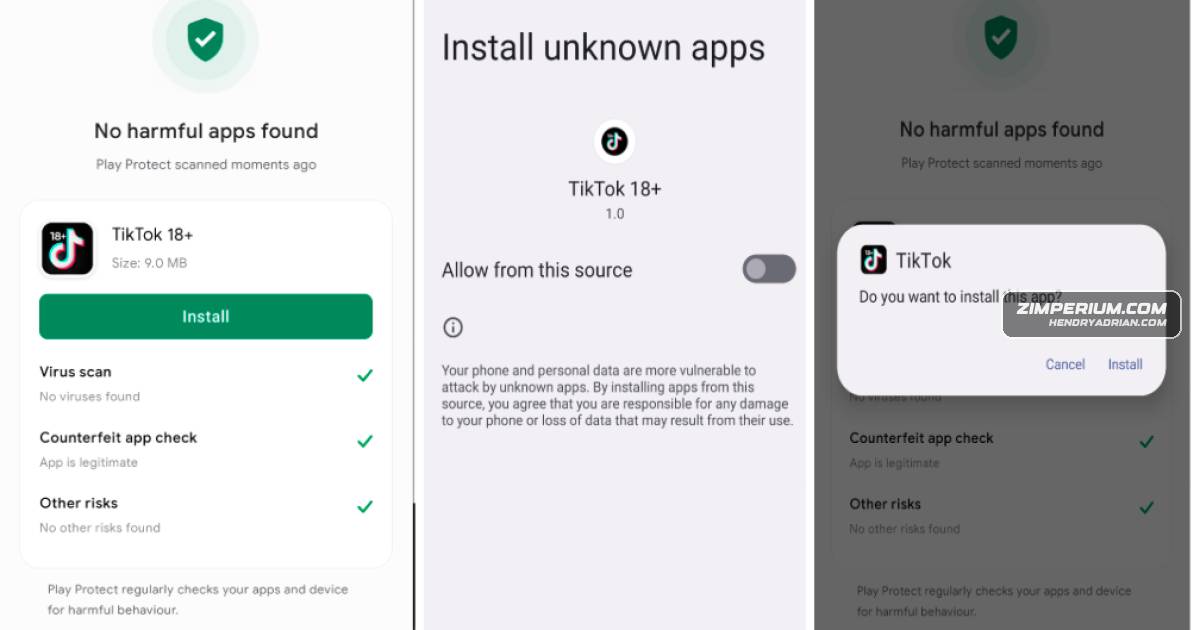
- Zimperium researchers report that malicious websites distribute a dropper that impersonates Google Play Protect and installs Rokarolla’s second-stage payload.
- The malware targets 217 banking and cryptocurrency apps, fetching HTML phishing overlays from its command-and-control server for selected apps.
- It uses fraudulent lock-screen and app overlays, keylogging, and Accessibility features to capture credentials, screen content, contacts, and clipboard data.
- Rokarolla can read and send SMS messages and block calls, potentially interfering with bank alerts and verification messages.
- The malware sends device telemetry over HTTPS and supports fallback command-and-control domains and remotely updated endpoints.
- The researchers report stealth and persistence features including hiding its app icon, attempting to disable Google Play Protect, suppressing audio, and keeping the screen awake.
Article Details
- Attack Vectors
- Malicious websites impersonate trusted apps, including TikTok and Google Chrome, to distribute a dropper that installs a second-stage Rokarolla payload.
- The malware uses deceptive overlays that imitate Android lock screens and targeted banking or cryptocurrency app login pages to capture credentials and payment information.
- Rokarolla abuses Accessibility services and requests SMS and notification access; it can capture keystrokes, screen content, clipboard data, SMS messages, and contacts.
- The malware communicates with C2 infrastructure over HTTPS, supports fallback domains, and can update its active endpoint through remote configuration.
- Defensive Notes
- The article says Zimperium MTD web protection blocks traffic to the reported malicious domains and phishing infrastructure.
- The article says zDefend detects activity such as screen sharing and Accessibility abuse; Zimperium also describes on-device detection of unauthorized Accessibility use and secondary-payload sideloading.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | abiorime[.]cfd | Fallback C2 domain listed in Rokarolla remote configuration. |
| DOMAIN | blestorians[.]cfd | Fallback C2 domain listed in Rokarolla remote configuration. |
| DOMAIN | morevoms[.]cfd | Additional C2 domain listed in Rokarolla remote configuration. |
| URL | hxxps[:]//beralisvc[.]info | Reported Rokarolla distribution site and C2 endpoint. |
| URL | hxxps[:]//infocontablidades[.]it[.]com/ | Malicious distribution site reported to deliver Rokarolla. |
MITRE ATT&CK
T1406.002The article reports that Rokarolla uses obfuscation and JSONPacker to conceal its code.T1414Rokarolla reads and overwrites clipboard contents, including to redirect cryptocurrency wallet addresses.T1417.001The malware uses keylogging commands to capture what victims type.T1417.002Rokarolla parses visible UI nodes and coordinates and captures on-screen content.T1513Rokarolla captures device screenshots and exfiltrates the images with timestamps.T1516Rokarolla displays deceptive lock-screen and banking-app overlays and can mimic user interaction with clicks and gestures.T1517The malware listens to notifications and monitors incoming SMS-related events.T1582Rokarolla can read and send SMS messages on behalf of the victim.T1616The malware can block and intercept phone calls using commands including disable_calls and calls_block.T1624.001The malware creates broadcast receivers to monitor SMS-related events.T1636.004Rokarolla exfiltrates SMS messages from infected devices.T1637The malware receives injected HTML payload endpoints dynamically from its server and can update its active C2 endpoint through remote configuration.T1646The article reports that Rokarolla sends stolen information to its C2 infrastructure.T1655.001The dropper impersonates Google Play Protect, and the malware also pretends to be a Google Play Update application.T1660Rokarolla is distributed through malicious websites that impersonate popular apps such as TikTok and Google Chrome.
Malware
Vendors
Products
AndroidRokarolla is a newly identified Android banking trojan that spreads through malicious websites, impersonates popular apps, and targets 217 banking and cryptocurrency applications.Google ChromeIt is spread via malicious websites that impersonate trusted apps such as TikTok and Google Chrome.Google Play ProtectThe trojan blocks calls, suppresses audio, hides its app icon, disables Google Play Protect, and keeps the screen awake to avoid detection.Mobile Runtime Protection (zDefend)However, Zimperium customers, utilizing both Mobile Threat Defense (MTD) and Runtime Application Protection (zDefend), remain protected against these evolving adversarial techniques.MTDHowever, Zimperium customers, utilizing both Mobile Threat Defense (MTD) and Runtime Application Protection (zDefend), remain protected against these evolving adversarial techniques.TikTok#RokarollaWhatsApp#Rokarolla
Industries
BankingRokarolla is a newly identified Android banking trojan that spreads through malicious websites, impersonates popular apps, and targets 217 banking and cryptocurrency applications.CryptocurrencyRokarolla is a newly identified Android banking trojan that spreads through malicious websites, impersonates popular apps, and targets 217 banking and cryptocurrency applications.