
FBI Warns Russian Intelligence-Linked Operators Are Targeting Signal Recovery Keys
Summary
FBI and CISA warn that Russian intelligence-linked operators are phishing for Signal Backup Recovery Keys to access backup messages and potentially take over accounts. They advise exposed users to generate a new key and remove unknown linked devices.
Key points
- The updated FBI and CISA advisory says operators now trick targets into sharing their Signal Backup Recovery Key, enabling access to backup message history and potential account takeover.
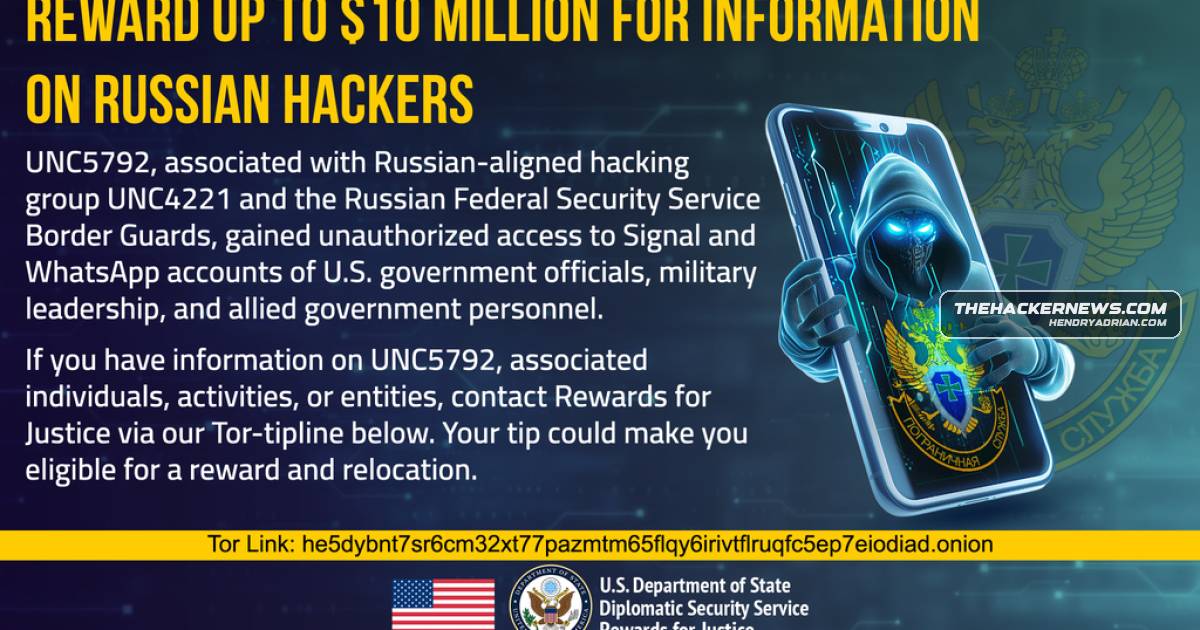
- The advisory identifies UNC5792 and UNC4221 and links the activity to Russian intelligence services.
- Targets include government officials, military personnel, political figures, journalists, and Ukraine-related officials; the broader campaign also targets WhatsApp accounts.
- Phishing messages impersonate Signal support and coach targets to enable backups and paste their recovery key into a chat.
- The agencies say the activity exploits individual accounts through social engineering; it does not break Signal's encryption or the app itself.
- Users should not share recovery keys, verification codes, or PINs; remove unknown linked devices and generate a new recovery key if exposed.
Article Details
- Event Type
- FBI and CISA updated an advisory about a Signal phishing campaign in which operators trick targets into sharing their Backup Recovery Key.
- Impact
- An exposed key can allow an attacker to restore backup message history and take over an account. The advisory says generating a new key prevents future backup downloads using the old key, but cannot recover data already accessed. The article reports that the broader campaign had compromised thousands of accounts worldwide.
Threat Actors
UNC4221Named in the updated advisory as a tracking name associated with the Russian intelligence-linked campaign; the FBI ties the activity to Russian intelligence services.UNC5792Named in the updated advisory as a tracking name associated with the Russian intelligence-linked campaign; the FBI ties the activity to Russian intelligence services. The State Department's Rewards for Justice program is offering up to $10 million for information on UNC5792.
Products
SignalThe FBI and CISA warn that Russian intelligence-linked operators have shifted their Signal phishing campaign to trick victims into revealing their Signal Backup Recovery Key, enabling access to backup message historyTelegramGoogle’s Threat Intelligence Group first documented UNC5792 abusing Signal’s linked-device feature in early 2025, and saw the same tradecraft turn up against WhatsApp and Telegram.WhatsAppThe campaign hits Signal and WhatsApp accounts; the new recovery-key tactic the advisory describes is specific to Signal.