
JA4 Primer Explains TLS Fingerprinting for Threat Analysis
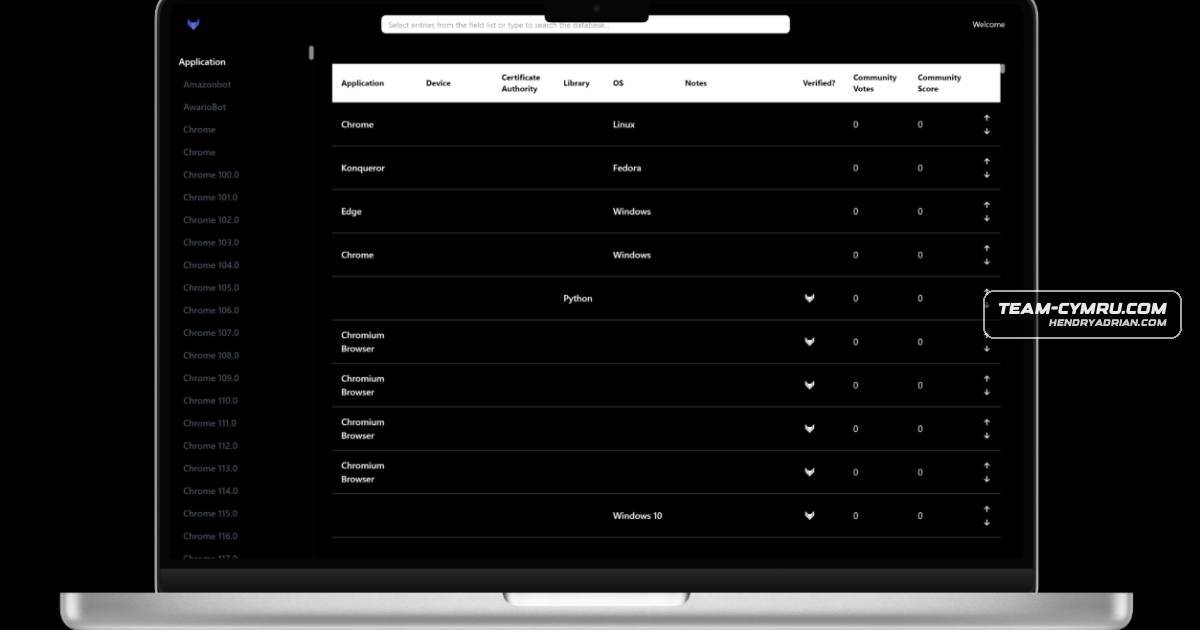
Summary
A primer explains how JA4 fingerprints TLS ClientHello attributes to help analysts identify applications and malware-related traffic, including in encrypted communications, and describes its differences from JA3 and use in threat hunting.
Key points
- JA4 fingerprints TLS clients using ClientHello attributes such as cipher suites, extensions and signature algorithms.
- The article says fingerprints can help identify applications or libraries used by malware in encrypted traffic, while noting JA4 may identify an underlying library rather than the malware itself.
- It describes combining up to seven JA4+ fingerprints per connection to improve identification and reduce false positives.
- Compared with JA3, JA4 is described as more granular, human- and machine-readable, and designed to support protocols including QUIC and DTLS.
- The primer suggests tracking a distinctive fingerprint across network traffic to investigate communications with a command-and-control server and identify related activity.
Article Details
- Topic
- JA4+ network fingerprinting for TLS and broader traffic analysis