
Using the PEB to Find Kernel32 in Memory
· 1:39 · Watch on YouTube ↗
Summary
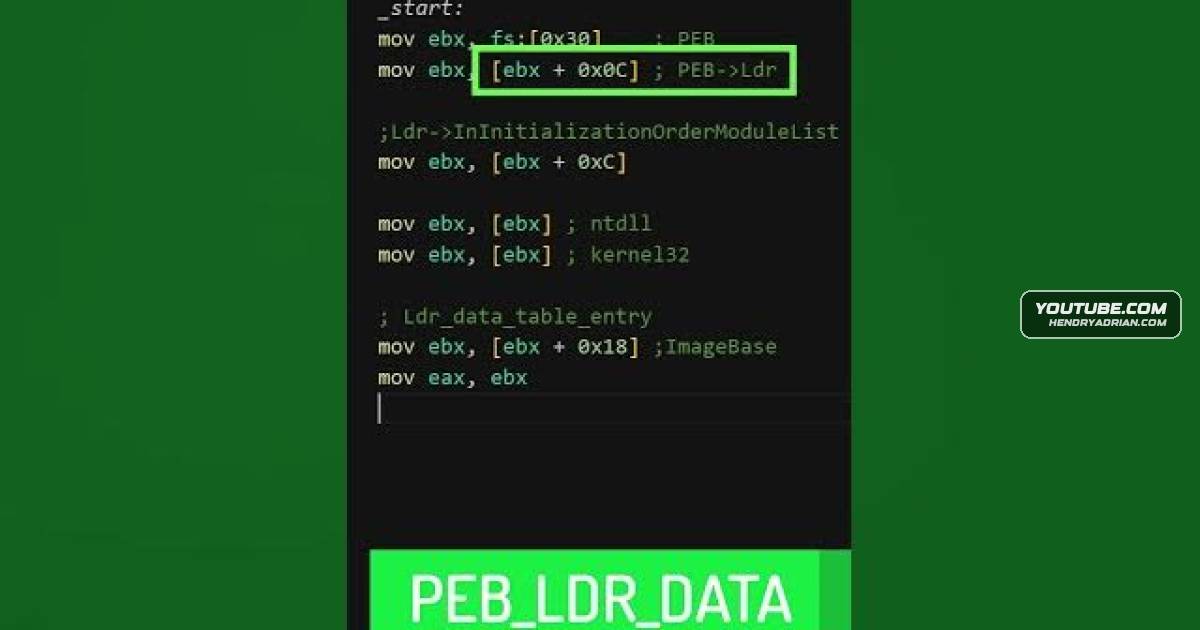
The video demonstrates using the Process Environment Block and its initialization-order module list to locate Kernel32’s in-memory base address, including the relevant offsets for 32-bit and 64-bit processes.
Key points
- The video describes finding a Windows library’s base address for shellcode or runtime linking.
- It gives the PEB offsets for 32-bit processes (FS: 0x30) and 64-bit processes (GS: 0x60).
- The PEB loader data contains linked lists tracking modules in load, memory, and initialization order.
- The video follows the initialization-order list and says Kernel32 is typically reached as the next node after the first entry.
- It identifies the image-base field at offset 0x18 in the LDR data table entry structure.