
Incransom Claims Attack on Policlinico Triestino in Italy
Incransom claims it encrypted critical systems at Italian healthcare network Policlinico Triestino and disrupted services. The monitoring post says the claim is unconfirmed.
Incransom claims it encrypted critical systems at Italian healthcare network Policlinico Triestino and disrupted services. The monitoring post says the claim is unconfirmed.

SilentRansomGroup reportedly targeted U.S. law firm Greenberg Traurig. The monitoring post attributes an operational-disruption claim to the group but says it cannot confirm the information.

A ransomware.live monitoring post records SilentRansomGroup’s claim targeting a redacted company, with a full data timer active. The post says the claim has not been independently confirmed.

SilentRansomGroup allegedly deployed ransomware against a company identified only as “G… …g.” A full-data timer is active. The claim was published on September 2, 2026, and the source says it cannot confirm its accuracy.
A ransomware.live monitoring post records Wallstreet's claim targeting Ormond Beach, Florida, and alleges service disruption and encrypted systems. The post says the claims are unconfirmed.
A ransomware.live monitoring post attributes an attack on PTT Oil and Retail Business in Thailand to direwolf, but says the group's claim could not be confirmed.
Ransomware group Dire Wolf claimed it targeted South Africa’s Cartrack Holdings and encrypted company data. The monitoring post says the claim is unconfirmed.
The incransom ransomware group claimed an attack on Mexican logistics firm Trucka, with disruption to its operations reported. The post says the claim’s accuracy could not be confirmed.
The ransomware group incransom claims an attack on Spanish asphalt and road-services company Asfalpasa, alleging disruption and data impact. The post says the claims are unverified.
A ransomware.live monitoring post attributes a ransomware incident affecting Proliance Surgeons to payoutsking and claims disruption to its surgical services. The post says the claim has not been confirmed.
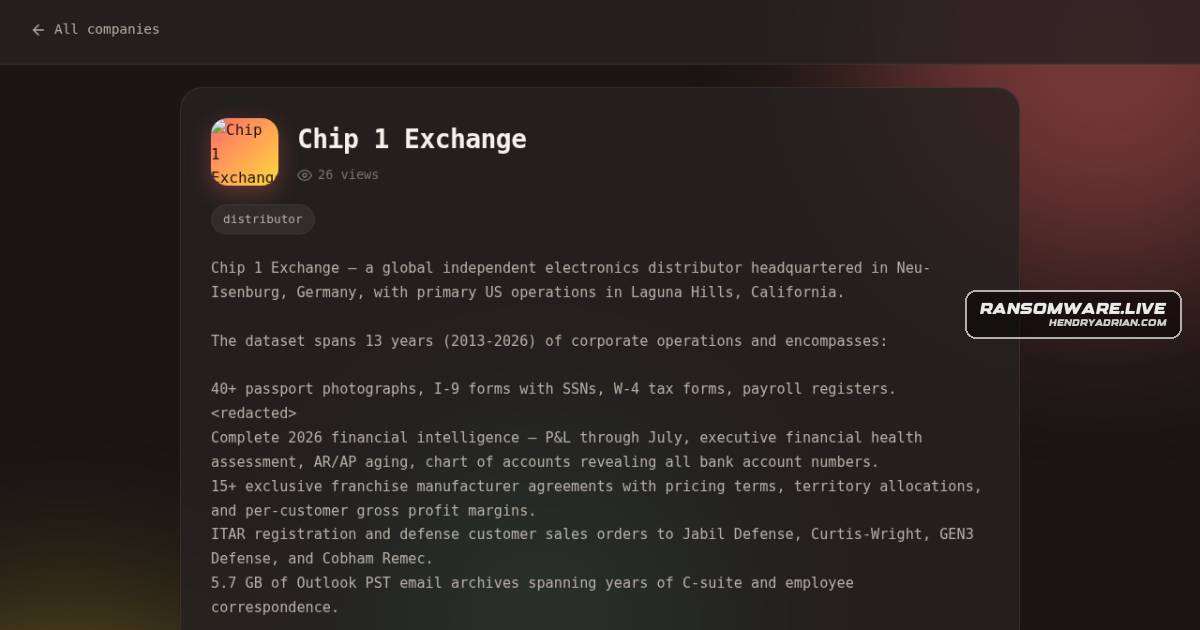
Ransomware.live reports that the aurora group claims to have compromised Singapore-based Chip 1 Exchange and exposed personnel, financial, defense-sales and email data. The claims are unverified.
Ransomware.live lists Grayson Rural Electric Cooperative as a Qilin target, alleging service disruption and data encryption. The claim was published Sept. 2, 2026, and has not been independently confirmed.
TheGentlemen claims CareerSource Palm Beach County’s systems were impacted by ransomware. The claim was published Aug. 31, 2026, and is unverified.
Ransomware.live reports a public Bravox claim targeting US-based SCHMIDT, which provides abrasive blasting systems and industrial engineering solutions. The claim remains unconfirmed, and no specific impact is reported.
Akira allegedly claimed it stole about 27GB of BYK Construction data, including employee and client information. The post warns of an impending release but says the claims could not be confirmed.
A monitoring entry names Holland & Knight in a SilentRansomGroup ransomware claim published September 1, 2026. The post says it cannot confirm the claim’s accuracy.
Ransomware.live reports that Global Secret Group listed US advertising-network company Quality Resource Pvt as a victim, claiming 60.1 GB of data across 170,436 files and 88,440 folders. The claim is unverified.
Akira claims it attacked desktop-as-a-service provider Flex1 and threatens to publish 402 GB of data. The group alleges the data includes employee and client records, financial information, and sensitive legal-client documents; the claims are unconfirmed.
A ransomware-group post attributed to Akira claims it will upload 35 GB of Congressional Iron Works data, allegedly including employee, client, financial, project, and NDA information. The claim is unverified.
A ransomware.live monitoring post attributes a ransomware incident affecting Honeycomb Programs Inc. to Direwolf and reports operational disruption and insurance involvement. The post says the group’s claims are unconfirmed.
A ransomware.live record attributes a claim that Direwolf targeted Brazil’s Oportunidados, encrypting files and causing data loss and service downtime. The report says the claims are unconfirmed.
A ransomware.live record attributes a claim of file encryption and service disruption at syc[.]es in Spain to BrainCipher. The post says the claim could not be independently confirmed.
BrainCipher claimed it targeted aeiconsultants[.]com, a US professional services organization, and compromised systems and encrypted data. The post cites the group's leak site and says the claim is unconfirmed.
A ransomware.live monitoring post reports BrainCipher's unverified claim that it targeted Spanish technology company icot[.]es, encrypted files, disrupted operations and threatened to leak or sell stolen data.