
Panzer Claims Ransomware Attack on Honda Peru
A ransomware.live record says Panzer targeted Honda Peru and claims the attack disrupted operations and data access. The post says the group’s claims are unconfirmed.
A ransomware.live record says Panzer targeted Honda Peru and claims the attack disrupted operations and data access. The post says the group’s claims are unconfirmed.
Qilin claimed it targeted US manufacturer Foremost Mfg; the monitoring post reports system and data disruption but says the claim could not be confirmed.
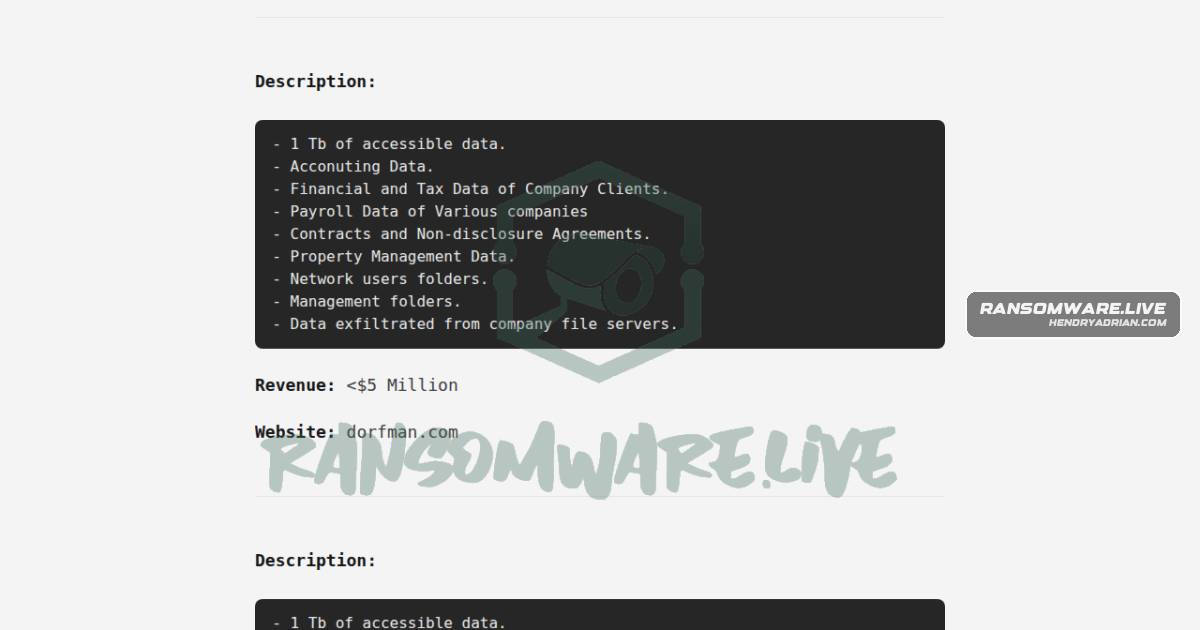
Ransomware.live recorded an unverified Genesis claim targeting US CPA firm Dorfman Abrams Music, P.C. The claim was published September 13, 2026, and discovered September 14.
The ransomware group unsafe claimed an attack on geekybunch[.]com and cited $5 million in lost revenue. The monitoring post says the claim is unconfirmed.
LockBit 5 claimed it disrupted operations and encrypted critical data at Taiwan technology company tpi.tw. The claim was published on September 14, 2026, and has not been confirmed.
A ransomware.live monitoring post attributes an attack disrupting Rosello et Fils' regional distribution operations to Eclipse, but says the group's public claim is unconfirmed.
Eclipse claimed to have targeted Dublin City Schools GA. The ransomware.live post lists September 14, 2026, as the discovery date and says the claim could not be confirmed.
A ransomware.live post records an unverified AuditTeam claim targeting Russian technology organization Ne***ox, with the incident discovered and published on September 14, 2026.

A ransomware-monitoring post attributes a claim of 37 GB of stolen law practice data from Mestechkin Law Group P.C. to the Booba Project. The post says the claim is unconfirmed.
Ransomware.live reports that Qilin claimed an attack on Argentina’s Vitar Group, but says it cannot confirm the claim’s accuracy.
A ransomware.live monitoring post attributes a reported attack on Brazilian transportation company Alicotrans to Qilin. The post says systems were disrupted and encrypted but notes the group’s claim is unconfirmed.
A ransomware.live post lists Peruvian manufacturer Cerámicas Kantu as a Panzer ransomware victim. The post cites the group’s public claim and says it cannot confirm the information.
Ransomware group unsafe claimed watchops.com as a victim. The post lists the US technology company and $1.3 million in revenue, but the report says the claims could not be confirmed.
A ransomware.live post says Vexy Ransomware targeted UK-based Strad Solutions. The claim is unconfirmed; the post says the company’s hosting, IT, cybersecurity and disaster recovery services were impacted.
A ransomware.live monitoring post reports that shinyhunters allegedly gave Kimberly-Clark until September 16, 2026, to respond or face data leakage. The claim is unconfirmed.
A post monitored by ransomware[.]live says Vexy Ransomware targeted Indian IT provider i2k2 Networks. The claim is unconfirmed, and no source is listed.
Rhysida claimed a ransomware attack on German electronics company Axdia International, allegedly disrupting operations and involving a payment demand. The article says the claims are unconfirmed.
Barracuda claims it exfiltrated 693 GB from i2i-systems, including source code and customer data tied to a Turk Telekom project. The monitoring post says the data is listed for $300,000; the claims are unconfirmed.
A ransomware.live post says Qilin targeted UK-based Gilco Scaffolding. The claim is based on the group’s public post and has not been independently confirmed.
A ransomware.live monitoring post reports AuditTeam’s unverified claim that it targeted Indian transportation victim vi***in, encrypting files and disrupting service. The post says the claim’s accuracy is unconfirmed.
A ransomware claim attributed to krybit names Kashkha, a UAE-based fashion brand. The claim was recorded on September 13, 2026, but the source says it could not verify the information.
The ransomware group emperador claims to have obtained 223.2 MB of Navitrans data, including pricing, financing and operational information. The monitoring post says the claim has not been independently confirmed.
AuditTeam allegedly compromised and encrypted systems and data belonging to victim FDC699DE3A112669 in Germany. The monitoring post says the claim is unverified.
A ransomware.live post records a Qilin claim involving French agricultural company CARIDRO VAL DE LOIRE, published September 13, 2026. The post says the claim is unverified.