
AuditTeam Claims Ransomware Attack on Indian Transportation Victim vi***in
Summary
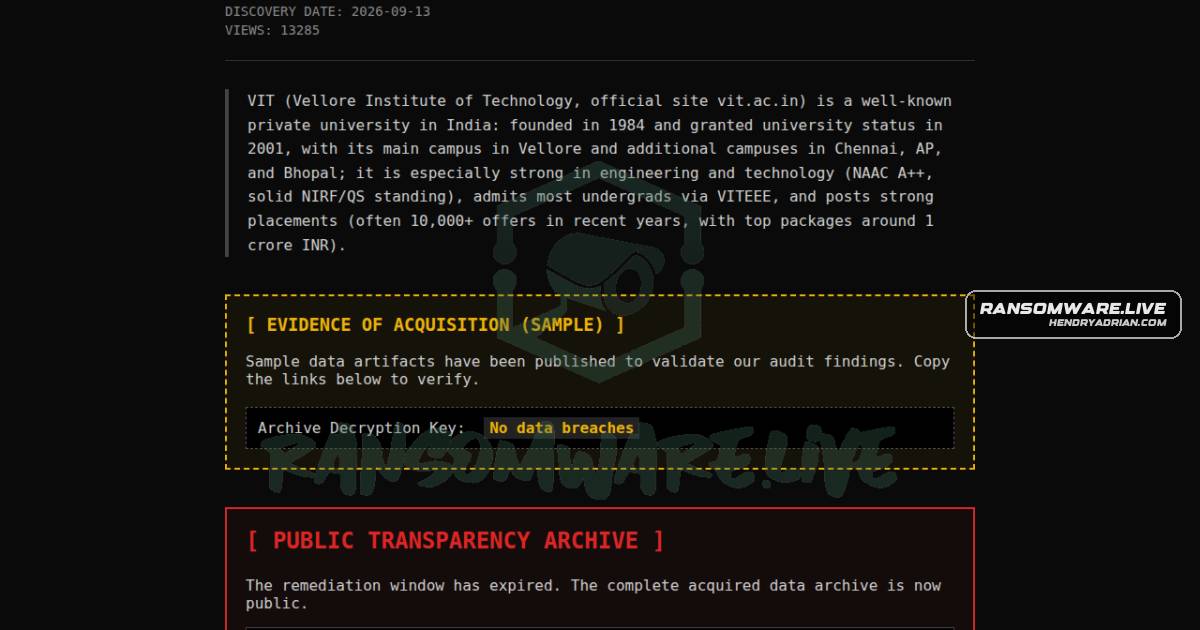
A ransomware.live monitoring post reports AuditTeam’s unverified claim that it targeted Indian transportation victim vi***in, encrypting files and disrupting service. The post says the claim’s accuracy is unconfirmed.
Key points
- The post attributes the ransomware claim to AuditTeam and identifies the victim as vi***in in India’s transportation sector.
- The claim alleges files were encrypted, payment was demanded to restore access, and service was disrupted.
- The post says the accuracy of the ransomware group’s claim could not be confirmed.
- The incident was listed as discovered on 2026-09-13 and published on 2026-09-13.
Article Details
- Victim
- vi***in
- Claim Date
- 2026-09-13
- Encryption Status
- The article alleges files were encrypted, but the claim is unverified and the victim has not confirmed it.
- Exfiltration Status
- Unknown; no exfiltration is reported.
- Ransom Demand
- The article alleges that payment was demanded to restore access; no amount is provided, and the claim is unverified.
- Leak Status
- AuditTeam's claim is reported, but no data leak or publication is reported; the incident is unconfirmed.