cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · fieldeffect.com

Fortinet Reports Active Exploitation of FortiMail File-Write Vulnerability

Fortinet reported active exploitation of CVE-2026-104286, an unauthenticated FortiMail file-write flaw that may enable code execution. Patches were pending for affected 7.4, 7.6, and 8.0 deployments; Fortinet published indicators and mitigations.
Oct 2, 2026
Vulnerability & Exploit · darkreading.com

Critical SConnect Flaw Enables Drive-By Remote Code Execution

Researchers say CVE-2026-18397 lets malicious webpages exploit Thales’ SConnect authentication software for remote code execution. Thales patched Chrome and Apple versions and removed the Edge app; SConnect is end of life.

Oct 2, 2026
Vulnerability & Exploit · bleepingcomputer.com

Kiteworks Patches Critical Email Gateway Flaw Allowing Unauthenticated Root Takeover

Kiteworks patched 126 vulnerabilities, including CVE-2026-54154, which could let unauthenticated attackers take over Email Protection Gateway appliances. The flaw affects versions before 9.4.1; the company reported no evidence of compromise.

Oct 1, 2026
Vulnerability & Exploit · cisa.gov

CISA Adds Actively Exploited Fortinet FortiMail Path Traversal to KEV Catalog

CISA added CVE-2026-104286, an actively exploited Fortinet FortiMail path traversal vulnerability, to its KEV Catalog and urges organizations to prioritize remediation.

Oct 1, 2026
Vulnerability & Exploit · helpnetsecurity.com

Cisco SD-WAN Manager Zero-Day Exploited in Attacks; Fixes Released

Cisco says attackers are exploiting an authentication bypass in Catalyst SD-WAN Manager that can grant admin-level API access. Fixes are available, and CISA has ordered US federal agencies to remediate by October 3, 2026.

Oct 1, 2026
Vulnerability & Exploit · securityweek.com

Cisco Patches Actively Exploited Catalyst SD-WAN Authentication Bypass

Cisco patched CVE-2026-76504, a critical authentication bypass actively exploited in Catalyst SD-WAN Manager. All deployments are affected; Cisco urges immediate upgrades, and CISA added the flaw to its KEV catalog.

Oct 1, 2026
Vulnerability & Exploit · fieldeffect.com

Actively Exploited SharePoint Flaw Enables Remote Code Execution

CVE-2026-65660 enables remote code execution on vulnerable on-premises SharePoint servers. Exploitation attempts followed public PoC release; Microsoft updates address the flaw, and researchers demonstrated a separate chain that can remove the authentication requirement

Oct 1, 2026
Vulnerability & Exploit · thehackernews.com

Cisco Warns of Active Exploitation of Critical SD-WAN Manager Zero-Day

Cisco says attackers are exploiting CVE-2026-76504, a critical authentication bypass in SD-WAN Manager that can grant unauthenticated admin API access. Fixed releases are available; Cisco advises restricting access, upgrading, and checking logs.

Sep 30, 2026
Vulnerability & Exploit · bleepingcomputer.com

Cisco Patches Actively Exploited Catalyst SD-WAN Authentication Bypass Zero-Day

Cisco says attackers are exploiting CVE-2026-76504 to bypass authentication and gain admin access to Catalyst SD-WAN Manager. The flaw affects all deployments; Cisco urges customers to upgrade and check logs for compromise.

Sep 30, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Warns of Critical Pre-Auth Code-Execution Flaw in MikroTik RouterOS

CISA warns that CVE-2026-84411 can let unauthenticated attackers execute code as root or cause denial of service on affected MikroTik RouterOS versions. No active exploitation is known; version guidance remains unclear.

Sep 30, 2026
Vulnerability & Exploit · rapid7.com

Critical Cisco SD-WAN Manager Authentication Bypass Actively Exploited

Cisco says attackers are exploiting CVE-2026-76504, a critical unauthenticated API bypass in Catalyst SD-WAN Manager. Fixed releases are available; Cisco and Rapid7 urge emergency upgrades and compromise checks.

Sep 30, 2026
Vulnerability & Exploit · helpnetsecurity.com

Attackers Exploit Two Citrix NetScaler Zero-Days, Reaching Root Access

Mandiant and GTIG report exploitation of two Citrix NetScaler zero-days since early September, affecting dozens of organizations. Attackers used web shells, configuration changes and SLAPSHOT tunneling; patching alone may not remove access or address stolen credentials.

Sep 30, 2026
Vulnerability & Exploit · bleepingcomputer.com

TeamViewer Urges Users to Patch Five High-Severity Flaws

TeamViewer urged users of its Windows, Linux, and macOS Full Client and Host software to update to version 15.82, which fixes five high-severity vulnerabilities. The company reported no known public exploits or active exploitation.

Sep 30, 2026
Vulnerability & Exploit · securityweek.com

WatchGuard Patches Critical Fireware OS Code-Injection Flaw

WatchGuard patched 15 Fireware OS vulnerabilities, including a critical code-injection flaw that could let an attacker controlling a remote VPN server execute commands as root on a connecting Firebox. The company reports no known exploitation.

Sep 30, 2026
Vulnerability & Exploit · cisa.gov

CISA Adds Actively Exploited Cisco SD-WAN Manager Vulnerability to KEV Catalog

CISA added Cisco Catalyst SD-WAN Manager vulnerability CVE-2026-76504 to its Known Exploited Vulnerabilities Catalog based on evidence of active exploitation and urged organizations to prioritize remediation.

Sep 30, 2026
Vulnerability & Exploit · securityweek.com

OpenSSL and WolfSSL Patch High-Severity Vulnerabilities

OpenSSL fixed 14 vulnerabilities, including a high-severity DTLS flaw that could expose heap data or crash applications. WolfSSL 5.9.4 patches 11 flaws, including three high-severity authentication-bypass vulnerabilities.

Sep 30, 2026
Vulnerability & Exploit · fieldeffect.com

Cisco Confirms Active Exploitation of Critical SD-WAN Manager Flaw

Cisco says attackers are exploiting CVE-2026-76504, a critical authentication bypass in Cisco Catalyst SD-WAN Manager that can grant administrator-level API access. On-premises users should apply the update; Cisco-managed cloud users have received the fix.

Sep 30, 2026
Vulnerability & Exploit · bleepingcomputer.com

BTR Spectre v2 Variant Can Leak Linux Root Password Hashes in Minutes

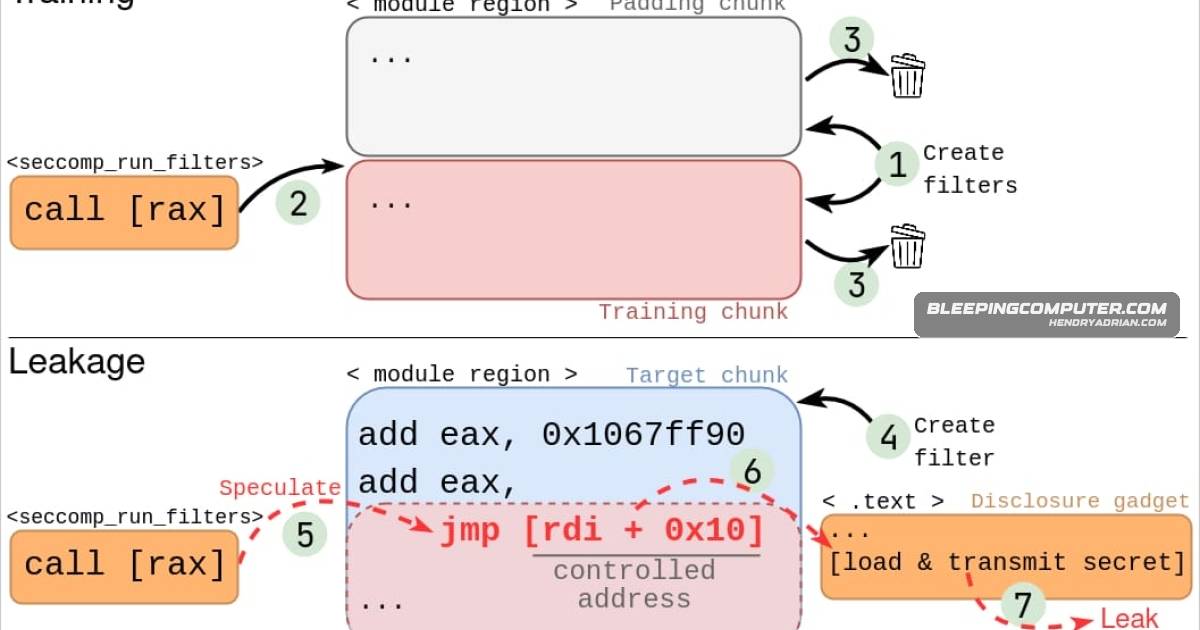
Researchers say BTR, a Spectre v2 variant, recovered a Linux root password hash in 3–5 minutes in tests on Intel CPUs. Linux kernel fixes have been merged for CVE-2026-64507 and CVE-2026-64508.

Sep 29, 2026
Vulnerability & Exploit · arcticwolf.com

Citrix NetScaler Flaws Reportedly Exploited as Zero-Days

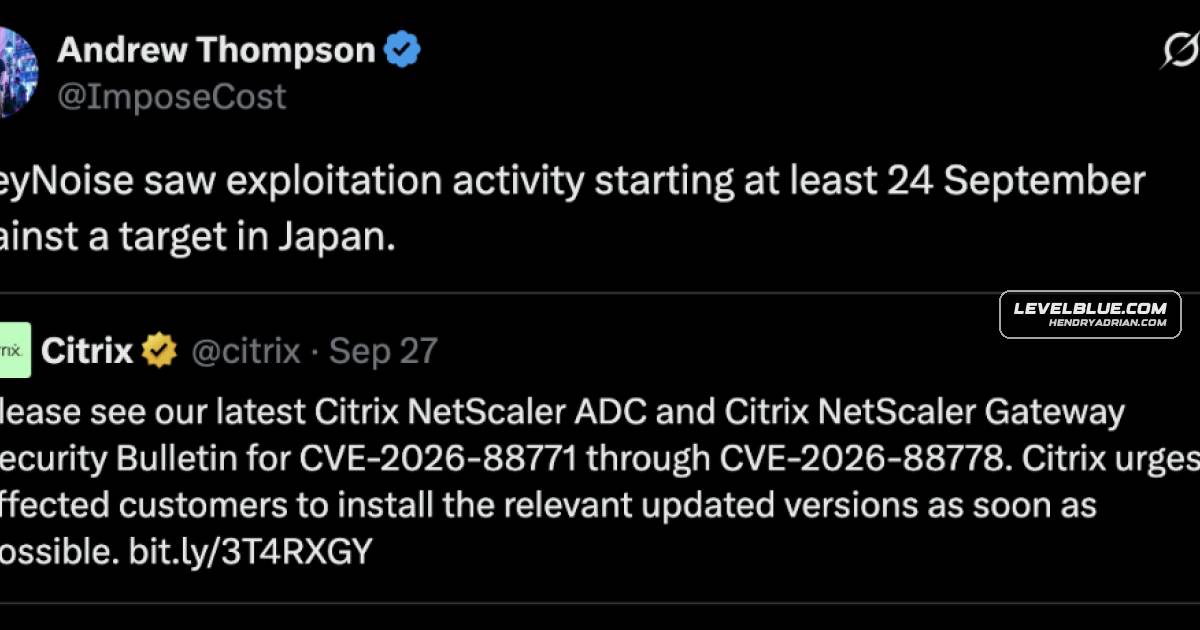
Arctic Wolf reports that CVE-2026-88771 and CVE-2026-88772 were exploited as zero-days in NetScaler devices. Citrix confirmed exploitation and urged customers to install fixed releases.

Sep 29, 2026
Vulnerability & Exploit · levelblue.com

Citrix NetScaler Zero-Days Exploited Globally; Patches Available

Citrix patched two critical NetScaler vulnerabilities that CISA says are being actively exploited globally. Affected organizations should upgrade; one flaw affects all deployments, while the other requires DTLS to be enabled.

Sep 29, 2026
Vulnerability & Exploit · cisa.gov

CISA Adds Actively Exploited Apple Vulnerability to KEV Catalog

CISA added Apple vulnerability CVE-2026-86950 to its Known Exploited Vulnerabilities Catalog based on evidence of active exploitation and urged organizations to prioritize risk-based remediation.

Sep 29, 2026
Vulnerability & Exploit · helpnetsecurity.com

Apple patches actively exploited Core Graphics zero-day

Apple patched CVE-2026-86950, an actively exploited out-of-bounds write in Core Graphics that could allow code execution via a malicious file. Apple says attacks may have targeted specific individuals; fixes are available for listed iOS, iPadOS, and macOS versions.

Sep 29, 2026
Vulnerability & Exploit · malwarebytes.com

Apple Patches CoreGraphics Flaw Reportedly Used in Targeted iPhone Attacks

Apple patched CVE-2026-86950, an out-of-bounds write in CoreGraphics that could allow code execution from a malicious file. Apple says it may have been exploited in highly targeted attacks against iPhones running iOS versions before iOS 27.

Sep 29, 2026
Vulnerability & Exploit · bleepingcomputer.com

Apple Patches CoreGraphics Zero-Day Reportedly Used in Targeted Attacks

Apple patched CVE-2026-20700, an out-of-bounds write in CoreGraphics that may have been exploited in sophisticated targeted attacks. Malicious files could trigger arbitrary code execution; Apple released updates for affected iPhones, iPads, and Macs.

Sep 29, 2026
PreviousPage 26 of 65 Next
© 2026 cyber.hendryadrian.com