Citrix NetScaler Zero-Days Exploited Globally; Patches Available
Summary
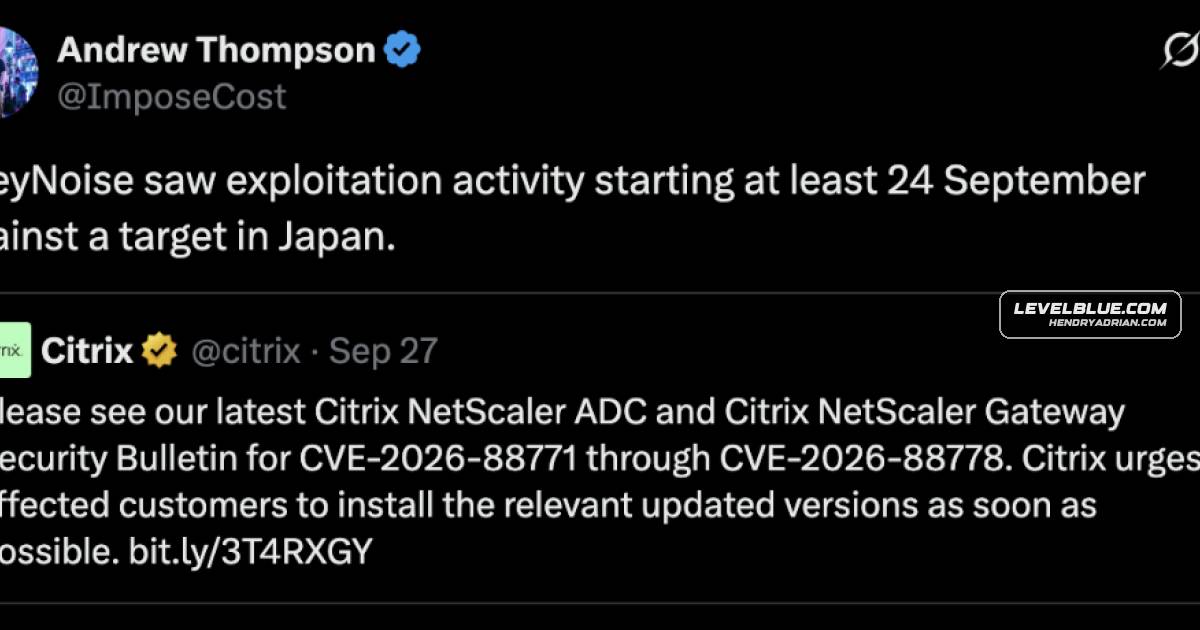
Citrix patched two critical NetScaler vulnerabilities that CISA says are being actively exploited globally. Affected organizations should upgrade; one flaw affects all deployments, while the other requires DTLS to be enabled.
Key points
- CVE-2026-88771 and CVE-2026-88772 each have a CVSS score of 9.5 and are listed in CISA’s Known Exploited Vulnerabilities catalog.
- CVE-2026-88771 affects all NetScaler ADC and Gateway deployments and could let an unauthenticated attacker execute commands.
- CVE-2026-88772 can enable remote code execution or denial of service; it requires DTLS, enabled by default on VPN virtual servers.
- Supported affected versions include ADC and Gateway 14.1 before 14.1-73.37 and 13.1 before 13.1-64.23, plus specified FIPS and NDcPP versions.
- Citrix patches are available, and the vendor recommends upgrading affected systems as soon as possible.
- The article describes exploitation involving malformed HTTP streams and TLS traffic; reports that attacks began as early as Sept. 24 are unconfirmed.
Article Details
- Vulnerability Types
- Improper input validation allowing unauthenticated arbitrary command execution
- Memory buffer bounds violation and buffer overflow allowing remote code execution or denial of service
- Severity
- Critical; CVSS 9.5 for each vulnerability.
- Affected Versions
- NetScaler ADC and NetScaler Gateway 14.1 before 14.1-73.37
- NetScaler ADC and NetScaler Gateway 13.1 before 13.1-64.23
- NetScaler ADC FIPS before 14.1-73.37 FIPS
- NetScaler ADC FIPS and NDcPP before 13.1-37.279
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Use access controls to isolate NetScaler systems.
- Revoke unused user accounts and reset authentication for active accounts.
MITRE ATT&CK
CVE
CVE-2026-88771CVE-2026-88771 (CVSS score: 9.5) - An improper input validation vulnerability that could allow an unauthenticated attacker to execute arbitrary commands.CVE-2026-88772CVE-2026-88772 (CVSS score: 9.5) - An improper restriction of operations within the bounds of a memory buffer vulnerability that could allow for remote code execution (RCE) or denial-of-service.