cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · socradar.io

Critical SAP Cloud SDK SSRF Could Expose OAuth2 Client Credentials

CVE-2026-89111 lets attacker-controlled tenant subdomains redirect SAP Cloud SDK OAuth2 requests, potentially exposing client credentials. SAP patched the flaw; independently reported validation gaps affect versions 0.53.0–0.55.0. No confirmed exploitation was reported.
Oct 14, 2026
Vulnerability & Exploit · rapid7.com

Rapid7 Discloses Critical Unauthenticated SQL Injection in WebAlliance eCommerce

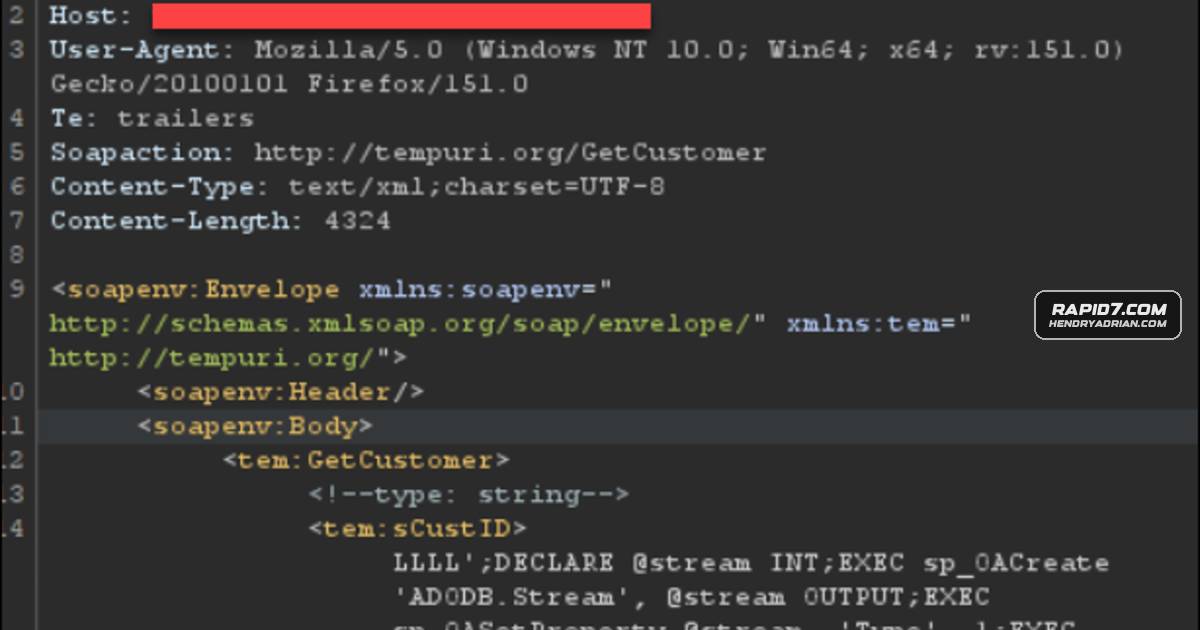
Rapid7 disclosed CVE-2026-108065, an unauthenticated SQL injection in Channel Software WebAlliance eCommerce. It may expose database information and, with elevated database privileges, enable server commands; Rapid7 advises blocking /preapproval.asmx.

Oct 14, 2026
Vulnerability & Exploit · socradar.io

10 RCE Vulnerabilities Defenders Should Prioritize, Including Exploited Zero-Days

A roundup ranks 10 RCE vulnerabilities across products including Citrix, Cisco, WordPress, and Splunk, detailing exploitation, KEV status, fixes, and mitigation guidance. Several were exploited before fixes were available.

Oct 14, 2026
Vulnerability & Exploit · thehackernews.com

CISA Urges Immediate Ivanti Connect Secure Patching After Active Exploitation

CISA urges immediate patching of actively exploited Ivanti Connect Secure authentication-bypass flaw CVE-2026-104935. Reports describe credential theft and data exfiltration; honeypots recorded 105 exploit attempts by October 14.

Oct 14, 2026
Vulnerability & Exploit · thehackernews.com

curl Fixes HTTP/2 Upload Flaw That Can Enable Client-Side Code Execution

A use-after-free in curl and libcurl 8.12.0–8.22.0 can let a malicious HTTP/2 server corrupt an uploading client’s memory and potentially execute code. curl fixed the flaw in 8.23.0; no attacks are reported.

Oct 14, 2026
Vulnerability & Exploit · cisa.gov

CISA Adds Four Actively Exploited Vulnerabilities to KEV Catalog

CISA added four vulnerabilities affecting Palo Alto Networks PAN-OS, Cisco Secure Email Gateway, and AhsayCBS to its KEV Catalog based on evidence of active exploitation, urging organizations to prioritize remediation.

Oct 14, 2026
Vulnerability & Exploit · socradar.io

Ivanti Patches Exploited Connect Secure Zero-Day, but Privilege-Escalation Flaw Remains

Attackers tracked as UTA0576 chained three flaws to gain root access on Ivanti Connect Secure appliances. Ivanti patched two flaws in CVE-2026-104935; the privilege-escalation flaw remains unpatched, and the Integrity Checker may miss the in-memory attack.

Oct 14, 2026
Vulnerability & Exploit · thehackernews.com

AI-Assisted Research Finds Linux Kernel Flaw Enabling Root Access and VM Escape

CVE-2026-74580 affects Linux kernels 4.11 to 7.2-rc4, enabling local users to gain root and, in a specific configuration, guests to attack the host. Fixes are available; restrict vhost device access until patched.

Oct 14, 2026
Vulnerability & Exploit · securityweek.com

Chrome and Firefox Updates Patch 114 Vulnerabilities as Mozilla Launches Firefox Enterprise

Google and Mozilla released Chrome and Firefox updates fixing 114 security flaws. Mozilla also introduced Firefox Enterprise, with a management console for organizations to control browser policies, access, data transfers, and AI use.

Oct 14, 2026
Vulnerability & Exploit · securityweek.com

Citrix, Fortinet and Ivanti Patch 29 Vulnerabilities, Including an Exploited Zero-Day

Citrix, Fortinet and Ivanti released updates addressing 29 vulnerabilities across their products, including critical flaws and an exploited Ivanti Connect Secure zero-day.

Oct 14, 2026
Vulnerability & Exploit · securityweek.com

Microsoft Fixes Record 1,413 Vulnerabilities, Including Exploited Windows Zero-Day

Microsoft's October 2026 updates fix 1,413 vulnerabilities, including an exploited Windows flaw that bypasses Mark of the Web protections. CISA added the zero-day to its KEV catalog and set an October 16 deadline for federal agencies.

Oct 14, 2026
Vulnerability & Exploit · securityweek.com

SAP Patches Critical NetWeaver, S/4HANA and Other Vulnerabilities

SAP released 22 new and updated security notes, including four critical vulnerabilities affecting Cloud SDK for Python, NetWeaver Visual Composer, S/4HANA and Manufacturing Integration and Intelligence. No exploitation in the wild was reported.

Oct 14, 2026
Vulnerability & Exploit · thehackernews.com

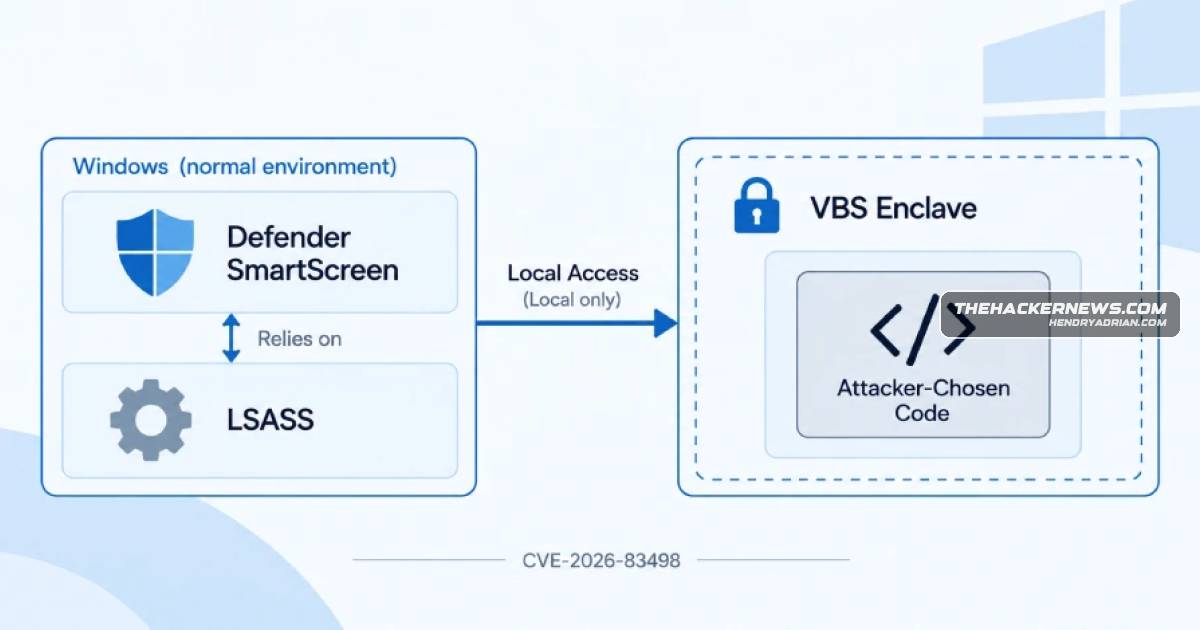
Windows SmartScreen Enclave Flaw Let Researchers Run Code in Its Protected Environment

Researchers demonstrated local code execution inside Windows’ SmartScreen enclave via CVE-2026-83498. Microsoft patched the flaw in its September 8, 2026 update; the proof of concept was not seen in real attacks.

Oct 14, 2026
Vulnerability & Exploit · thehackernews.com

Microsoft Patches 1,413 Vulnerabilities, Including Actively Exploited Windows Shell Flaw

Microsoft patched 1,413 vulnerabilities, including an actively exploited Windows flaw that evades Mark of the Web defenses. Other updates address a publicly known WDAC bypass and a critical Raw Image Extension vulnerability.

Oct 14, 2026
Vulnerability & Exploit · krebsonsecurity.com

Microsoft Patches More Than 1,400 Security Flaws, Including an Exploited Zero-Day

Microsoft issued fixes for more than 1,400 vulnerabilities, including one exploited zero-day and at least 78 critical flaws. A .NET Framework security bypass had also been publicly disclosed before the updates.

Oct 14, 2026
Vulnerability & Exploit · bleepingcomputer.com

Palo Alto Networks Patches PAN-OS RCE Flaw Exploited in Attacks

Palo Alto Networks says attackers have exploited CVE-2026-0322, an authenticated PAN-OS management-interface RCE flaw. Fixes are available for affected versions, and CISA added it to its Known Exploited Vulnerabilities catalog.

Oct 14, 2026
Vulnerability & Exploit · darkreading.com

Claude Code Desktop Flaw Let Malicious Previews Steal Developer Credentials

Noma researchers found that chained flaws in Claude Code Desktop’s preview pane could let a malicious HTML file silently exfiltrate developer credentials. Anthropic patched the issue after researchers bypassed an initial fix.

Oct 14, 2026
Vulnerability & Exploit · darkreading.com

Attackers Exploit Ivanti Connect Secure Zero-Day Before Fix Reached All Supported Versions

Attackers exploited CVE-2026-104935 in Ivanti Connect Secure appliances. Ivanti had patched part of the flaw in one release but was still backporting fixes; CISA added it to KEV, and researchers warned its integrity tool may miss exploitation.

Oct 14, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Urges Immediate Patching of Ivanti Connect Secure Zero-Day Exploited in Attacks

CISA urged immediate patching of Ivanti Connect Secure flaw CVE-2026-104935, exploited since at least October 1. Ivanti released fixes; defenders should investigate for compromise and follow CISA’s recovery steps.

Oct 14, 2026
Vulnerability & Exploit · bleepingcomputer.com

Cisco patches actively exploited Secure Email Gateway zero-day enabling root command execution

Cisco patched CVE-2026-76519, an actively exploited Secure Email Gateway flaw that can let unauthenticated attackers execute commands as root via a crafted email attachment. The company advises checking for compromise and upgrading affected systems.

Oct 14, 2026
Vulnerability & Exploit · securityweek.com

Ivanti Zero-Day Chain Enabled Root Access to Fully Patched VPN Appliances

Ivanti says attackers exploited a zero-day chain in Connect Secure VPN appliances for root-level access. Patches address two flaws; a third remains unpatched. Attackers stole credentials and limited Active Directory metadata.

Oct 13, 2026
Vulnerability & Exploit · thehackernews.com

Docker Fixes Critical Hub Flaw That Let Users Push Images as Others

A Docker Hub flaw let users’ personal access tokens act as another user’s, enabling registry access to their images. Docker fixed it on September 30, found no evidence of exploitation, and deactivated identified transferred tokens.

Oct 13, 2026
Vulnerability & Exploit · thehackernews.com

Ivanti Connect Secure Zero-Day Chain Enables Unauthenticated Root Access; Third Fix Pending

Volexity reports an attacker chained three Ivanti Connect Secure zero-days for unauthenticated root access. Ivanti says exploitation is limited; fixes are available for two flaws, while the third remains unpatched.

Oct 13, 2026
Vulnerability & Exploit · thehackernews.com

SAP Cloud SDK for Python Flaw Could Expose OAuth2 Credentials

SAP disclosed a CVSS 10.0 SSRF flaw in its Cloud SDK for Python that could send OAuth2 client credentials to an attacker-controlled server. SAP fixed it, but later releases reportedly omitted the check; the advisory does not clarify their CVE status.

Oct 13, 2026
PreviousPage 21 of 65 Next
© 2026 cyber.hendryadrian.com