cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3799 articles

Security News · threatfabric.com

IPTV-Themed Ads Spread Mobile Malware in Four Countries

Threat Fabric reports IPTV-themed campaigns in Portugal, Italy, Turkey and India that use social media ads and unofficial streaming apps to deliver mobile malware, including Antidot, Medusa and BTMOB.
Jun 25, 2026
Security News · thehackernews.com

Operation Endgame Disrupts Amadey and StealC Infrastructure, 27 Million Credentials Recovered

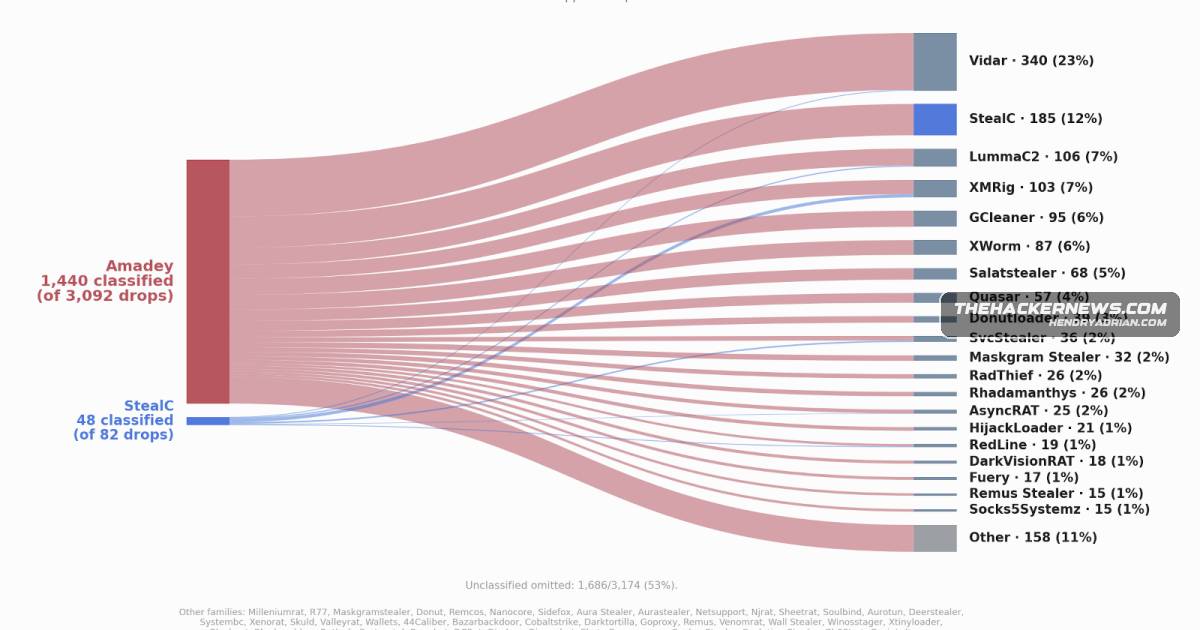
Operation Endgame partners disrupted Amadey and StealC infrastructure, dismantling 326 servers and 142 domains. Authorities say they recovered 27 million stolen credentials and restricted more than $47 million in criminal crypto assets.

Jun 24, 2026
Security News · bleepingcomputer.com

Operation Endgame Disrupts Amadey, StealC and SocGholish Infrastructure

Microsoft, Europol and partners disrupted infrastructure linked to Amadey, StealC and SocGholish. Europol reported 326 servers and 142 domains disrupted; the operation also recovered stolen credentials and identified cryptocurrency linked to criminal activity.

Jun 24, 2026
Security News · securityweek.com

Microsoft and Partners Disrupt Shared Amadey and StealC Infrastructure

Microsoft, Europol, law enforcement and security firms targeted hundreds of servers and domains in an Operation Endgame action against infrastructure shared by Amadey and StealC. Europol reported seized credentials, secured computers and flagged crypto assets.

Jun 24, 2026
Security News · cyberscoop.com

Microsoft and Law Enforcement Target Amadey and StealC in Joint Takedown

Microsoft and law enforcement used a court-authorized operation to target more than 200 command-and-control servers shared by Amadey and StealC. Microsoft said the tools were linked to over 140,000 infected computers in one week.

Jun 24, 2026
Security News · securityweek.com

Proposed AIVEX Model Adds Safety Context to AI Vulnerability Triage

Devashri Datta proposes SRIL and AIVEX to add operational and safety context to AI vulnerability triage. She says Flexera has adopted SRIL, Anchore is working on it, and the CycloneDX working group is considering AIVEX.

Jun 24, 2026
Security News · bleepingcomputer.com

Mistic Backdoor Linked to Ransomware Access Broker KongTuke

Symantec and Zscaler report that Mistic, also tracked as MTLBackdoor, has been used in financially motivated intrusions. The stealthy backdoor is linked to KongTuke/Woodgnat and supports persistence, in-memory execution, and Beacon Object Files.

Jun 24, 2026
Security News · cybersecuritypulse.net

Security roundup: Klue breach exposes SaaS OAuth tokens, OpenAI expands patching initiative

The newsletter covers a Klue breach in which stolen OAuth tokens were used to access connected customer environments, alongside OpenAI remediation efforts, Accenture’s OT security acquisitions, and other security industry news.

Jun 24, 2026
Security News · securityweek.com

Third Defendant in DraftKings Credential-Stuffing Case Sentenced to 18 Months

Nathan Austad was sentenced to 18 months in prison for his role in a 2022 credential-stuffing attack matching the DOJ’s description of the DraftKings case. The DOJ says Austad and accomplices stole about $600,000 from 1,600 accounts.

Jun 24, 2026
Security News · cyberscoop.com

Open-Source Security Efforts Face Growing Pressure as U.S. Initiatives Stall

Experts warn that rising supply-chain compromises and AI-driven vulnerability discovery are straining open-source security. U.S. efforts have lost momentum, while Europe is advancing regulations and grants.

Jun 24, 2026
Security News · thehackernews.com

DOJ Seizes HuiOne-Linked Cloud Account as Treasury Sanctions Prince Group Network

The DOJ seized a cloud account used by HuiOne Group subsidiaries, including the operator of a Telegram-based criminal marketplace. Treasury announced sanctions against nine individuals and 26 entities linked to Prince Group.

Jun 24, 2026
Security News · thehackernews.com

U.S. Executive Order Sets 2030–31 Deadlines for Federal Post-Quantum Cryptography Migration

A June 22 executive order sets federal post-quantum cryptography deadlines of 2030 for key establishment and 2031 for digital signatures, with agency inventories and migration plans intended to address “harvest now, decrypt later” risks.

Jun 24, 2026
Security News · thehackernews.com

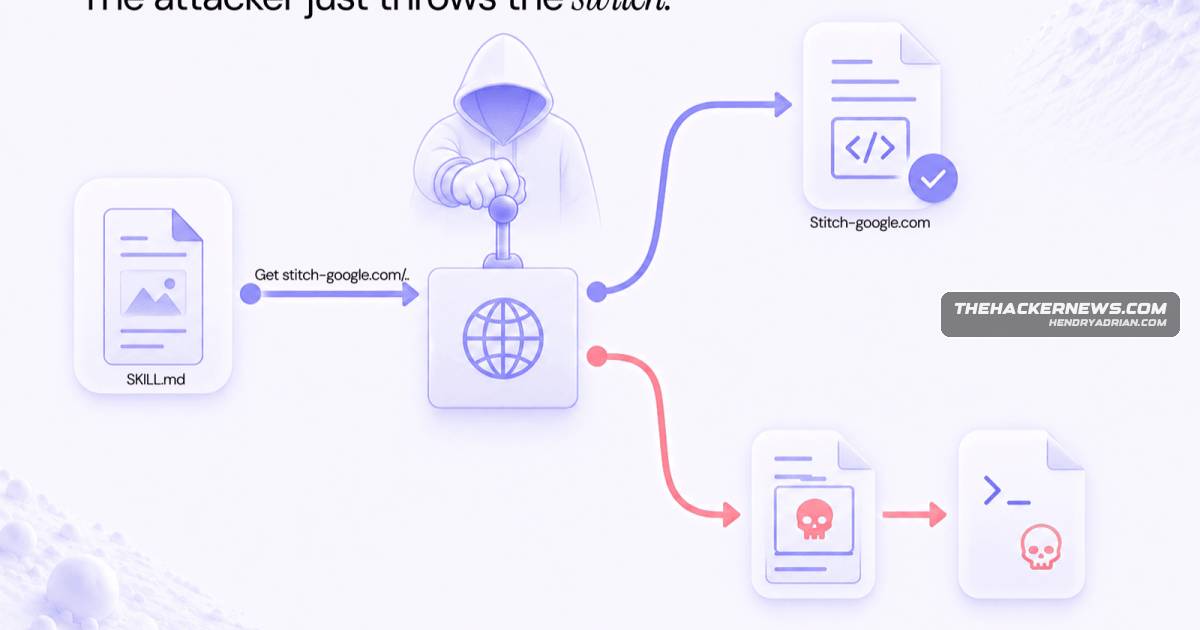
AIR Says Fake AI Agent Skill Reached 26,000 Agents After Evading Scanners

AIR says its harmless fake AI skill reached about 26,000 agents after scanners cleared a package whose mutable external link later served a script. The figure is the firm’s claim and is not independently confirmed.

Jun 24, 2026
Security News · securityweek.com

Anthropic’s Mythos Found Vulnerabilities in Classified U.S. Systems, Official Says

An anonymous U.S. official told the AP that Anthropic’s Mythos found vulnerabilities in sensitive government systems during testing, but said this did not show the model could exploit them. The testing and model restrictions drew industry debate.

Jun 24, 2026
Security News · cyberscoop.com

Algerian Man Charged Over Alleged Phishing and Stolen-Credential Marketplaces

Abdellah Belmili was extradited from Spain and charged with conspiracy to commit bank fraud. Investigators say he ran marketplaces selling phishing kits and stolen credentials, and linked the operation to about 5,600 victims.

Jun 23, 2026
Security News · cyberscoop.com

U.S. Seizes Huione-Linked Cloud Infrastructure and Expands Sanctions

The DOJ seized cloud infrastructure used by Huione Guarantee. U.S. officials allege the marketplace helped move and conceal billions in fraud proceeds; Treasury also expanded sanctions on Huione-linked firms and Prince Group affiliates.

Jun 23, 2026
Security News · bleepingcomputer.com

macOS ClickFix Campaign Uses Silently Mounted DMGs to Install AMOS Stealer

Palo Alto Networks Unit 42 reports a macOS ClickFix campaign that tricks users into running Terminal commands to download and mount a DMG installing AMOS, which targets credentials, wallet data, Keychain files, messages, and documents.

Jun 23, 2026
Security News · securityweek.com

Dragos Launches EmberAI for OT Cybersecurity

Dragos says EmberAI uses its OT cybersecurity Intelligence Fabric to answer plain-language queries, correlate threat, asset, vulnerability, and network data, and provide customer-contextualized recommendations. The module is generally available.

Jun 23, 2026
Security News · darkreading.com

Fake Reputation Network Promoted Crypto-Stealing Clipboard Malware

Check Point reports a campaign using fake tools and coordinated promotion on trusted platforms to distribute a Rust-based clipboard hijacker targeting Windows and macOS users and cryptocurrency.

Jun 23, 2026
Security News · securityweek.com

Algerian Man Extradited to US Over Alleged Cybercrime Marketplaces

Abdellah Belmili was extradited from Spain to the US and charged with conspiracy to commit bank fraud. Authorities allege he ran cybercrime marketplaces, including one offering bulk SMS services for phishing campaigns.

Jun 23, 2026
Security News · securityweek.com

OpenAI Expands Cybersecurity Efforts With Tools and Open-Source Patching Program

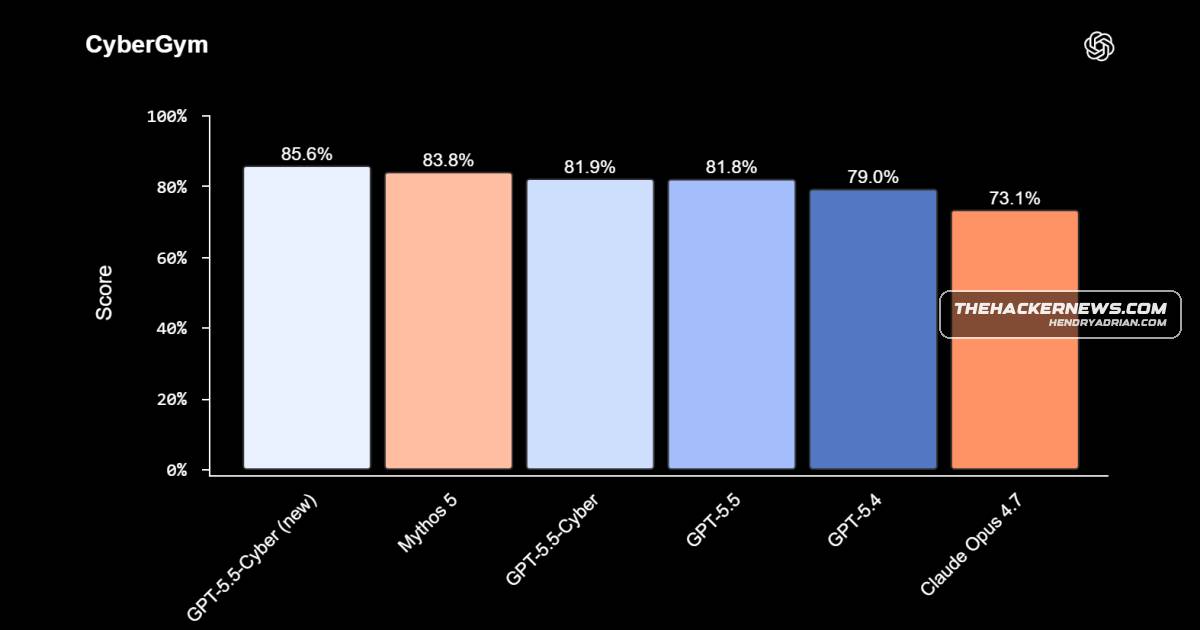
OpenAI announced Codex Security updates, the full release of GPT-5.5-Cyber, and Patch the Planet, a program to help open-source maintainers validate and patch vulnerabilities with security researchers.

Jun 23, 2026
Security News · securityweek.com

SOCRadar Reports FortiBleed Campaign Targeting 430,000 FortiGate Firewalls

SOCRadar reports that FortiBleed targets FortiGate and other systems to harvest credentials and sell access. It says more than 19,000 identified targets remain actively monitored and attributes a defense contractor compromise to the campaign.

Jun 23, 2026
Security News · thehackernews.com

OpenAI Expands GPT-5.5-Cyber and Launches Open-Source Security Initiative

OpenAI says its updated GPT-5.5-Cyber model and Codex Security plugin will help trusted defenders find, validate and patch vulnerabilities; its Patch the Planet initiative with Trail of Bits will support open-source projects amid concerns AI is accelerating exploitation

Jun 23, 2026
Security News · bleepingcomputer.com

WhatsApp Phishing Campaign Uses Fake Business Documents to Install Remote-Access Software

Kaspersky reports that compromised WhatsApp accounts are spreading disguised VBScript files. On Windows, the files launch scripts that install ManageEngine Endpoint Central configured for attacker-controlled remote access; links to ValleyRAT and Gh0st RAT infrastructure

Jun 23, 2026
PreviousPage 86 of 159 Next
© 2026 cyber.hendryadrian.com