
Operation Endgame Disrupts Amadey and StealC Infrastructure, 27 Million Credentials Recovered
Summary
Operation Endgame partners disrupted Amadey and StealC infrastructure, dismantling 326 servers and 142 domains. Authorities say they recovered 27 million stolen credentials and restricted more than $47 million in criminal crypto assets.
Key points
- The June 15–19, 2026 operation involved law enforcement and judicial authorities from eight countries, with support from Bitdefender, Bitsight, ESET, and Microsoft.
- Authorities dismantled 326 servers and 142 domains; Microsoft said it flagged 200 malicious Amadey and StealC C2 domains and IP addresses.
- The operation recovered 27 million stolen login credentials and identified, flagged, and restricted more than $47 million in criminal crypto assets.
- Microsoft linked Amadey and StealC to more than 140,000 infected computers globally in the first two weeks of May 2026; it said it identified over 18,000 victim computers and severed criminal control of those devices.
- Amadey acts as a loader for additional malware, while StealC steals information such as credentials, cookies, and browser data; both are offered under a malware-as-a-service model.
- The article describes Amadey and StealC as components of a cybercrime pipeline used to deliver payloads, steal sensitive information, and support further criminal activity.
Article Details
- Event Type
- Coordinated international law-enforcement and private-sector operation disrupting infrastructure used by the Amadey and StealC malware ecosystems.
- Impact
- Authorities dismantled 326 servers and 142 domains and recovered 27 million stolen login credentials. More than $47 million in criminal cryptocurrency assets was identified, flagged, and restricted. Microsoft linked Amadey and StealC to over 140,000 infected computers globally in the first two weeks of May 2026 and said it had identified over 18,000 victim computers and severed criminal control of those devices. Microsoft also reported that 200 malicious C2 domains and IP addresses had been shut down.
MITRE ATT&CK
T1059.003 · Windows Command ShellAmadey supports running commands using cmd.exe.T1105 · Ingress Tool TransferAmadey and StealC can download additional payloads, including executable and script files.T1113 · Screen CaptureAmadey and StealC can capture screenshots.T1189 · Drive-by CompromiseThe article reports that SocGholish is disseminated using compromised WordPress sites.T1539 · Steal Web Session CookieStealC collects session cookies.T1555.003 · Credentials from Web BrowsersStealC harvests credentials from Chromium browsers and other applications.T1566 · PhishingThe article reports phishing campaigns as a means of disseminating Amadey.
People
Alex CosoiBitdefender chief security strategist who commented on the takedown and the role of public-private collaboration.Jakub TomanekESET researcher who described and compared the Amadey and StealC affiliate operating models.Tomáš ProcházkaESET researcher who described and compared the Amadey and StealC affiliate operating models.
Threat Actors
Malware
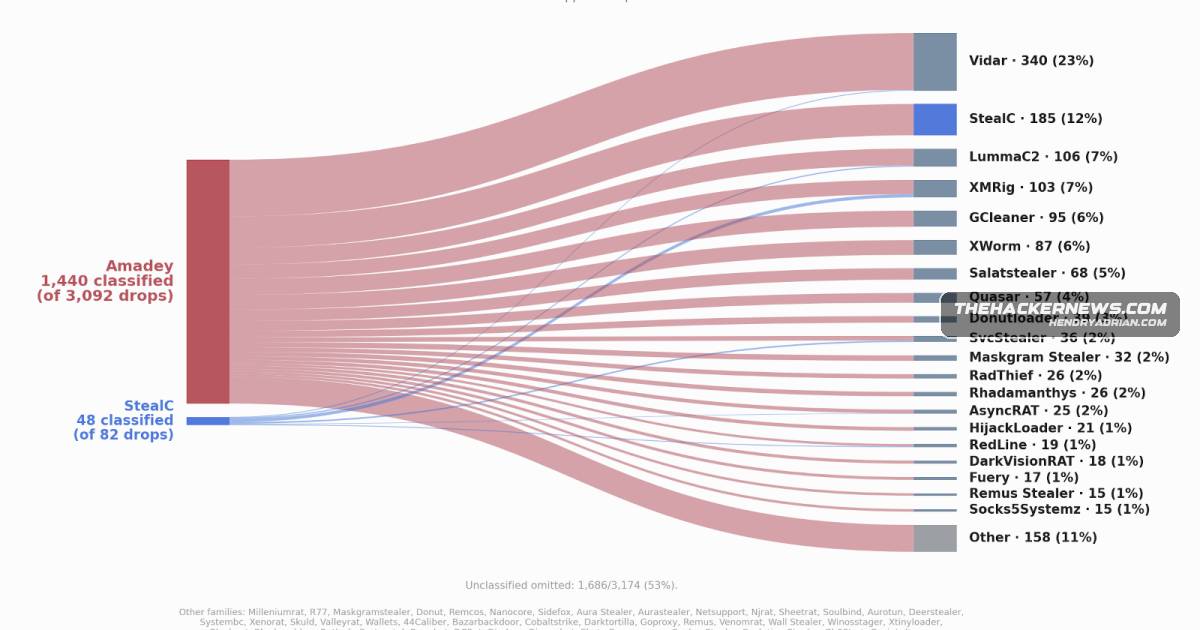
Agent Teslabotnet cluster distributing payloads like Lumma Stealer, Vidar Stealer, StealC, Rugmi, PureCrypter, Agent Tesla, Rhadmanthys Stealer, RedLine Stealer, SmokeLoader, XWorm, and AsyncRAT.Amadeyoperation with support from Bitdefender, Bitsight, ESET, and Microsoft dismantled infrastructure used by Amadey and StealC, disrupting the malware supply chain behind credential theft, fraud, and ransomware attacks.EmmenhtalAmadey has also been propagated via other loaders like Emmenhtal and SmokeLoader.Lumma Stealerhave been inside the Amadey ecosystem, with the largest botnet cluster distributing payloads like Lumma Stealer, Vidar Stealer, StealC, Rugmi, PureCrypter, Agent Tesla, Rhadmanthys Stealer, RedLine Stealer,PureCrypterthe largest botnet cluster distributing payloads like Lumma Stealer, Vidar Stealer, StealC, Rugmi, PureCrypter, Agent Tesla, Rhadmanthys Stealer, RedLine Stealer, SmokeLoader, XWorm, and AsyncRAT.Rugmiwith the largest botnet cluster distributing payloads like Lumma Stealer, Vidar Stealer, StealC, Rugmi, PureCrypter, Agent Tesla, Rhadmanthys Stealer, RedLine Stealer, SmokeLoader, XWorm, and AsyncRAT.SmokeLoaderAmadey has also been propagated via other loaders like Emmenhtal and SmokeLoader.SocGholishdisrupted malicious infrastructure associated with SocGholish and cleaned up nearly 15,000 infected WordPress websites.StealCwith support from Bitdefender, Bitsight, ESET, and Microsoft dismantled infrastructure used by Amadey and StealC, disrupting the malware supply chain behind credential theft, fraud, and ransomware attacks.Vidarthe Amadey ecosystem, with the largest botnet cluster distributing payloads like Lumma Stealer, Vidar Stealer, StealC, Rugmi, PureCrypter, Agent Tesla, Rhadmanthys Stealer, RedLine Stealer, SmokeLoader, XWorm,
Vendors
BitdefenderA coordinated international law enforcement operation with support from Bitdefender, Bitsight, ESET, and Microsoft dismantled infrastructure used by Amadey and StealC, disrupting the malware supply chain behindBitsightA coordinated international law enforcement operation with support from Bitdefender, Bitsight, ESET, and Microsoft dismantled infrastructure used by Amadey and StealC, disrupting the malware supply chain behindCyberArkEarlier this January, CyberArk disclosed a cross-site scripting (XSS) vulnerability in the web-based control panel by the StealC operators that made it possible to glean insights into the MaaS operation, including oneESETA coordinated international law enforcement operation with support from Bitdefender, Bitsight, ESET, and Microsoft dismantled infrastructure used by Amadey and StealC, disrupting the malware supply chain behindIBMIBM X-Force and Proofpoint also noted that multiple security flaws were identified in the C2 panel, one of which was a directory traversal bug that made it possible to upload a web shell to the StealC C2 server.MicrosoftA coordinated international law enforcement operation with support from Bitdefender, Bitsight, ESET, and Microsoft dismantled infrastructure used by Amadey and StealC, disrupting the malware supply chain behindProofpointIBM X-Force and Proofpoint also noted that multiple security flaws were identified in the C2 panel, one of which was a directory traversal bug that made it possible to upload a web shell to the StealC C2 server.
Countries
BelgiumIt involved judicial authorities and law enforcement from Belgium, Canada, Denmark, France, Germany, the Netherlands, the U.K., and the U.S.CanadaThe development comes days after authorities from the Netherlands, Canada, Germany, and the U.S.DenmarkIt involved judicial authorities and law enforcement from Belgium, Canada, Denmark, France, Germany, the Netherlands, the U.K., and the U.S.FranceIt involved judicial authorities and law enforcement from Belgium, Canada, Denmark, France, Germany, the Netherlands, the U.K., and the U.S.GermanyThe development comes days after authorities from the Netherlands, Canada, Germany, and the U.S.ItalyThe highest infection concentrations have been reported in the U.S., Poland, and Italy.PolandThe highest infection concentrations have been reported in the U.S., Poland, and Italy.the NetherlandsThe development comes days after authorities from the Netherlands, Canada, Germany, and the U.S.the U.K.It involved judicial authorities and law enforcement from Belgium, Canada, Denmark, France, Germany, the Netherlands, the U.K., and the U.S.the U.S.The development comes days after authorities from the Netherlands, Canada, Germany, and the U.S.