cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3793 articles

Security News · cyberscoop.com

Former DigitalMint Negotiator Sentenced for Colluding With BlackCat Affiliates

Angelo John Martino III was sentenced to 70 months after pleading guilty to conspiring with BlackCat affiliates and using confidential client information to help extort $75.3 million from five U.S. companies.
Jul 10, 2026
Security News · thehackernews.com

npm 12 Makes Install Scripts and Git/Remote Dependencies Opt-In

npm 12 disables lifecycle scripts and Git and remote URL dependencies by default, requiring approval. GitHub also announced limits on 2FA-bypass tokens, while pnpm 11.10 adds registry-bound authentication configuration.

Jul 10, 2026
Security News · thehackernews.com

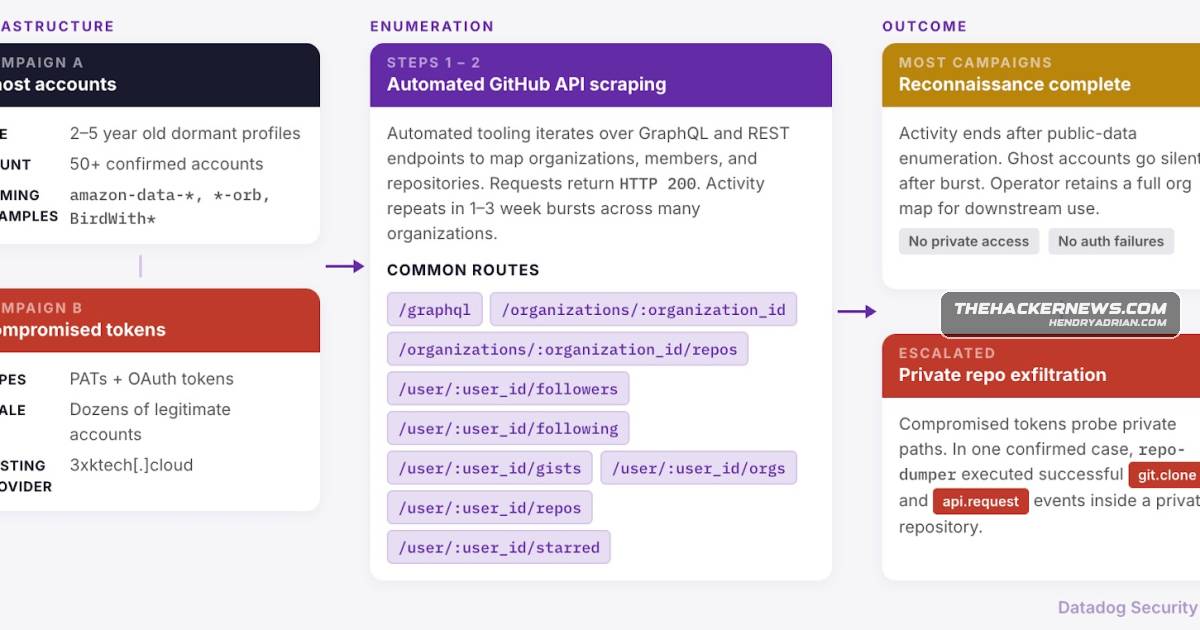
Dormant GitHub Accounts Used to Map Organizations and Clone a Private Repository

Datadog Security Labs reports overlapping campaigns using dormant GitHub accounts and compromised tokens to enumerate organizations and users. In some cases, the activity reportedly went beyond public data and cloned a private repository.

Jul 10, 2026
Security News · enisa.europa.eu

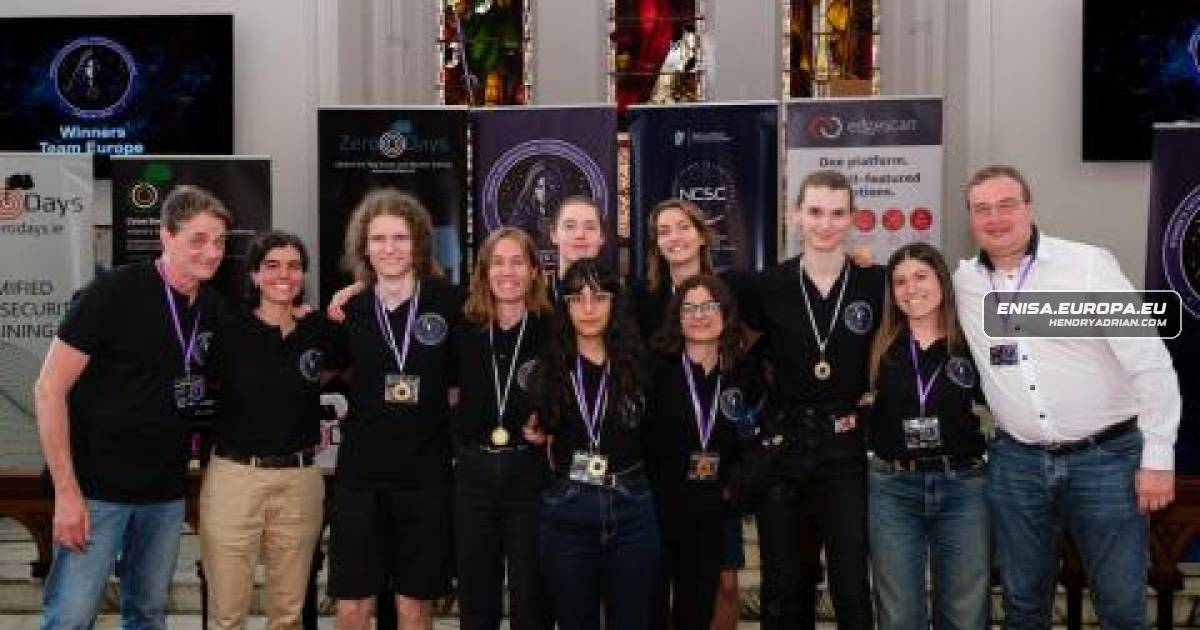
Team Europe Wins First International Cybersecurity Challenge for Women

Team Europe won the first Women International Cybersecurity Challenge in Dublin. Nine regional teams competed in technical challenges including cryptography, forensics, exploitation, hardware security, and attack and defence.

Jul 10, 2026
Security News · opensourcemalware.com

Podcast Covers PolinRider’s Spread, Malicious npm Packages and Open VSX Security

The episode discusses PolinRider’s spread into Go and PHP, malicious npm packages attributed to a cybersecurity startup, a lawsuit over an allegedly false IOC, and Open VSX’s security controls.

Jul 9, 2026
Security News · bleepingcomputer.com

Microsoft Expects More Windows Security Updates as AI Finds Flaws

Microsoft says AI-assisted vulnerability discovery may increase Windows security updates. Its MDASH system scans critical binaries and validates findings; Microsoft is also updating its Secure Development Lifecycle for AI-enabled threats.

Jul 9, 2026
Security News · bleepingcomputer.com

ReliaQuest Details Helix SharePoint Data-Extortion Tactics

ReliaQuest says Helix uses vishing, device-code phishing and MFA abuse to access SharePoint, add an authenticator for persistence and bulk-download files for extortion. It sees possible links to ShinyHunters and BlackFile and recommends disabling device-code login.

Jul 9, 2026
Security News · cyberscoop.com

764 Offshoot Leader Sentenced to 40 Years for Child Exploitation

Alexis Aldair Chavez, leader of the 764 offshoot 8884, was sentenced to 40 years in federal prison for sexually exploiting children. Prosecutors said he and co-conspirators used online services to groom and coerce victims.

Jul 9, 2026
Security News · cyberscoop.com

Interpol Operation Arrests More Than 5,800 in Cybercrime Crackdown Across 97 Countries

Interpol said Operation First Light led to more than 5,800 arrests, $293 million seized and over 142,000 victims identified across 97 countries while targeting social-engineering scams and money laundering.

Jul 9, 2026
Security News · bleepingcomputer.com

INTERPOL-Led Operation Arrests 5,811 Suspects in Global Fraud Crackdown

INTERPOL says Operation First Light 2026 led to 5,811 arrests and $293 million in asset seizures across 97 countries. Investigators identified over 142,000 victims and blocked 31,014 bank accounts.

Jul 9, 2026
Security News · bleepingcomputer.com

Microsoft Plans to Remove OWA Light From Exchange Server

Microsoft plans to disable and remove OWA Light in an Exchange Server update estimated for August 2026. Admins can already block the legacy client using Exchange PowerShell commands.

Jul 9, 2026
Security News · securityweek.com

QIZ Security Raises $17 Million for Cryptographic Governance Platform

Israeli startup QIZ Security raised $17 million in seed funding to grow its platform for discovering and managing cryptographic assets, identifying weaknesses, and prioritizing remediation across on-premises, cloud, and hybrid environments.

Jul 9, 2026
Security News · securityweek.com

UK Unveils Cyber Shield AI Defense Plan and Cyber Resilience Pledge

The UK’s NCSC outlined Cyber Shield, a proposed national agentic-AI cyber defense effort, while the government launched a voluntary Cyber Resilience Pledge with 60 founding signatories and three commitments for organizations.

Jul 9, 2026
Security News · securityweek.com

8Layers Raises $1.1 Million, Bringing Early-Stage Funding to $2.9 Million

Spanish startup 8Layers raised a $1.1 million pre-seed extension, bringing its early-stage funding to $2.9 million. Its identity security platform connects to identity providers to assess risks, detect threats and support compliance.

Jul 9, 2026
Security News · sysdig.com

June 2026 Security Briefing Highlights Tchap Compromise and Emerging Threats

Sysdig’s June 2026 briefing covers the confirmed compromise of France’s Tchap app, Novo Nordisk’s reported unauthorized access and FulcrumSec’s exfiltration claim, plus cloud attacks, AI misuse, GitHub workflow abuse and exploited vulnerabilities.

Jul 9, 2026
Security News · okta.com

Vishing Campaign Targets Microsoft 365 Passkey Enrollment, Okta Says

Okta reports that O-UNC-066, also known as Pink, has used vishing and a phishing kit to trick Microsoft 365 users into authorizing fraudulent passkeys. The activity has been observed across industries; no direct Microsoft account compromise was observed.

Jul 9, 2026
Security News · therecord.media

Taiwan Charges Two Businessmen Over Alleged China-Linked Espionage Campaign

Taiwan charged two businessmen accused of leasing LINE accounts to China-linked operators who impersonated journalists and used fake encrypted-communications software to deliver malware. The case adds official backing to earlier ICIJ and Citizen Lab findings.

Jul 9, 2026
Security News · therecord.media

Block to Pay $45 Million to Settle Cash App Security Allegations

Block agreed to pay $45 million to settle allegations from 46 states that Cash App misled users about security and left them vulnerable to fraud. The agreement requires 24-hour live support, including coverage by a real person.

Jul 9, 2026
Security News · therecord.media

Greek Predator Spyware Victims Sue Intellexa for €7.6 Million

Eight Greek victims whose devices had confirmed Predator spyware traces are suing Intellexa and 13 associated individuals, seeking about €7.6 million. Their trial is scheduled for April 2027.

Jul 9, 2026
Security News · recordedfuture.com

Recorded Future and Mastercard Discuss Using Cyber Intelligence to Get Ahead of Payment Fraud

At RiskX Singapore 2026, Recorded Future and Mastercard discussed connecting cyber and payment-fraud signals to detect scams, compromised cards, and Magecart infections before criminals monetize them.

Jul 9, 2026
Security News · cyberscoop.com

Paris Peace Forum Launches INTAiC to Assess AI Cyber Threats

The Paris Peace Forum is launching INTAiC, an international initiative to assess AI-related threats to internet infrastructure, maintain a threat resource for defenders and support independent evaluations of frontier model cyber capabilities.

Jul 8, 2026
Security News · bleepingcomputer.com

Suspected China-Aligned Cluster Targets University Roundcube Servers

Proofpoint reports UNK_MassTraction has targeted U.S. and Canadian universities via malicious emails exploiting Roundcube flaws CVE-2024-42009 and CVE-2025-49113 to steal credentials and deploy backdoors. China alignment is a low-confidence assessment.

Jul 8, 2026
Security News · bleepingcomputer.com

Fake Paysafe, Skrill and Neteller SDKs on npm and PyPI Steal Secrets

Socket researchers say at least 17 fake payment SDK packages on npm and PyPI stole credentials and tokens, sending data to an AWS-hosted server. They recommend removing the packages, rotating secrets and checking CI logs.

Jul 8, 2026
Security News · bleepingcomputer.com

Vishing Campaign Uses Fake Entra Passkey Enrollment to Target Microsoft 365 Users

Okta says O-UNC-066, linked to the Pink extortion operation, has used vishing and fake Entra passkey pages to capture Microsoft 365 credentials and MFA responses and register attacker-controlled passkeys.

Jul 8, 2026
PreviousPage 79 of 159 Next
© 2026 cyber.hendryadrian.com