
Dormant GitHub Accounts Used to Map Organizations and Clone a Private Repository
Summary
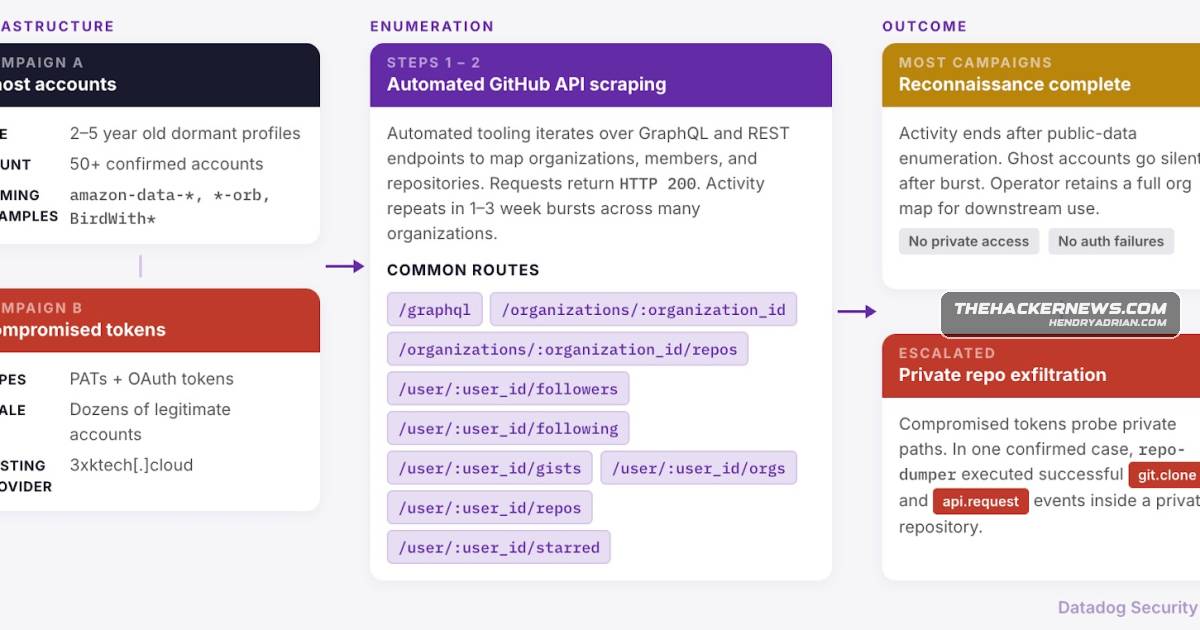
Datadog Security Labs reports overlapping campaigns using dormant GitHub accounts and compromised tokens to enumerate organizations and users. In some cases, the activity reportedly went beyond public data and cloned a private repository.
Key points
- Datadog Security Labs reports several overlapping campaigns systematically enumerating GitHub organizations, repositories, and user accounts through the API.
- The activity used automated scraping tools with custom or legitimate-sounding user agents.
- Operators reportedly used more than 50 dormant accounts, created two to five years earlier, alongside legitimate accounts with exposed or compromised personal access tokens.
- Queries mapped public repositories, followers, memberships, gists, starred repositories, and project activity.
- While most activity targeted public data, Datadog says attackers cloned a private repository belonging to one organization.
Article Details
- Event Type
- GitHub API reconnaissance and private repository access
- Impact
- Datadog Security Labs reports that multiple campaigns enumerated GitHub organizations, repositories, and user accounts, using dormant accounts and exposed or compromised tokens to blend in. In some instances, attackers successfully cloned a private repository belonging to one organization.