cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3793 articles

Security News · thehackernews.com

Microsoft Patches Record 622 CVEs, Including Two Actively Exploited Zero-Days

Microsoft's July Patch Tuesday addresses 622 CVEs. The company flags two privilege-escalation flaws in SharePoint Server and AD FS as exploited; the release also completes Kerberos RC4 hardening and includes a SharePoint authentication-bypass fix.
Jul 14, 2026
Security News · cyberscoop.com

Microsoft patches 622 vulnerabilities, including two exploited zero-days

Microsoft’s Patch Tuesday addressed a record 622 vulnerabilities, including two actively exploited zero-days in Active Directory Federation Services and SharePoint Server. SAP also patched critical flaws in NetWeaver Application Server and Approuter.

Jul 14, 2026
Security News · securityweek.com

Microsoft Patches 622 Vulnerabilities, Including Two Exploited Zero-Days

Microsoft's July 2026 Patch Tuesday fixes 622 vulnerabilities, including two reported as exploited zero-days affecting AD FS and SharePoint Server. The roundup also highlights critical flaws across Windows and other products.

Jul 14, 2026
Security News · bleepingcomputer.com

Fake Security Alerts Target LastPass and Bitwarden Users

Fake security emails targeting LastPass and Bitwarden users lead to counterfeit DocuSign pages. LastPass says its systems were not compromised; the malicious site prompted downloads and was later taken offline.

Jul 14, 2026
Security News · bleepingcomputer.com

Microsoft Releases July 2026 Windows 11 Updates Addressing 571 Vulnerabilities

Microsoft released July 2026 cumulative updates KB5101650 and KB5099414 for Windows 11 versions 25H2, 24H2, and 23H2, addressing 571 vulnerabilities and delivering numerous reliability, accessibility, and feature updates.

Jul 14, 2026
Security News · bleepingcomputer.com

Microsoft July 2026 Patch Tuesday Fixes 570 Flaws, Including Three Zero-Days

Microsoft’s July 2026 Patch Tuesday addresses 570 vulnerabilities, including two actively exploited privilege-escalation flaws and a publicly disclosed BitLocker bypass.

Jul 14, 2026
Security News · securityonline.info

Researcher Says Grok Build Privacy Mode Did Not Block Repository Uploads

A researcher reported that Grok Build could upload full local repositories to Google cloud storage through a separate server-controlled mechanism, unaffected by /privacy. The article says uploads were later disabled server-side.

Jul 14, 2026
Security News · cyberscoop.com

U.S. Sanctions First VPN Services and Two Alleged Ransomware Enablers

The U.S. Treasury sanctioned First VPN Services (1VPNS), its alleged administrator Dmytro Rashevskyi, and Yegeniy Vladimirovich Silayev over alleged support for ransomware operations, including infrastructure and malware-disguising tools.

Jul 14, 2026
Security News · chainalysis.com

US, UK and EU Sanction Trickbot Figure “Stern” and Other Cybercrime Enablers

The US, UK and EU announced sanctions against cybercriminals and enablers, including Trickbot administrator Vitaly Kovalev (“Stern”), whose associated wallets received over $300 million in ransom payments.

Jul 14, 2026
Security News · bleepingcomputer.com

SAP patches 16 flaws in July updates, including three critical vulnerabilities

SAP’s July 2026 security updates fix 16 vulnerabilities, including three critical flaws in NetWeaver, Approuter, and Commerce Cloud. SAP says it has no evidence the flaws have been exploited.

Jul 14, 2026
Security News · bleepingcomputer.com

Jalisco and OmegaLord Phishing Kits Target Microsoft 365, Aim to Bypass MFA

ReliaQuest says Jalisco uses OAuth device-code phishing and OmegaLord imitates a PDF Reader login to target Microsoft 365 accounts and work around MFA. It recommends restricting device registration and blocking device-code authentication.

Jul 14, 2026
Security News · bleepingcomputer.com

Microsoft Entra ID to Make Passkeys Default, Retire SMS and Voice Authentication

Microsoft will make passkeys the Entra ID default starting September 2026 and retire SMS and voice authentication on February 1, 2027. Users relying on phone-based MFA will be prompted to register passkeys.

Jul 14, 2026
Security News · bleepingcomputer.com

U.S. Sanctions 1VPNS VPN Service and Cryptor Seller Over Ransomware Support

The U.S. sanctioned 1VPNS, its administrator Dmytro Rashevskyi, and cryptor seller Yegeniy Silayev for supporting ransomware attacks. A multinational operation dismantled 1VPNS and seized 33 servers across 27 countries.

Jul 14, 2026
Security News · securityweek.com

US and Allies Warn Russian APTs Are Targeting Critical Infrastructure Routers

A joint advisory says Russian FSB Center 16 actors target poorly secured routers at critical infrastructure organizations, using SNMP to copy device configurations and exploiting known Cisco flaws. Agencies recommend hardening network-device access and updating firmware

Jul 14, 2026
Security News · securityweek.com

Valarian Raises $50 Million for Kubernetes Security Control Platform

Valarian raised $50 million in Series A funding to expand its ACRA platform, which the company says governs AI models and other Kubernetes workloads with per-workload policies, isolation and runtime controls.

Jul 14, 2026
Security News · securityweek.com

Pentagon Suspends CMMC Phase Two for 60-Day Review

The Pentagon suspended CMMC phase two, which was due to require Level 2 third-party assessments for new contracts from November 2026, while a task force reviews the program. Phase one requirements remain in force.

Jul 14, 2026
Security News · stepsecurity.io

StepSecurity Launches Policy Enforcement for VS Code Extensions

StepSecurity’s Device Policy lets teams approve or block VS Code extensions and versions across developer devices, with policy deployment through MDM or its agent on macOS, Windows, and Linux.

Jul 14, 2026
Security News · enisa.europa.eu

ENISA Launches Podcast Series With First Episode on Frontier AI and Cybersecurity

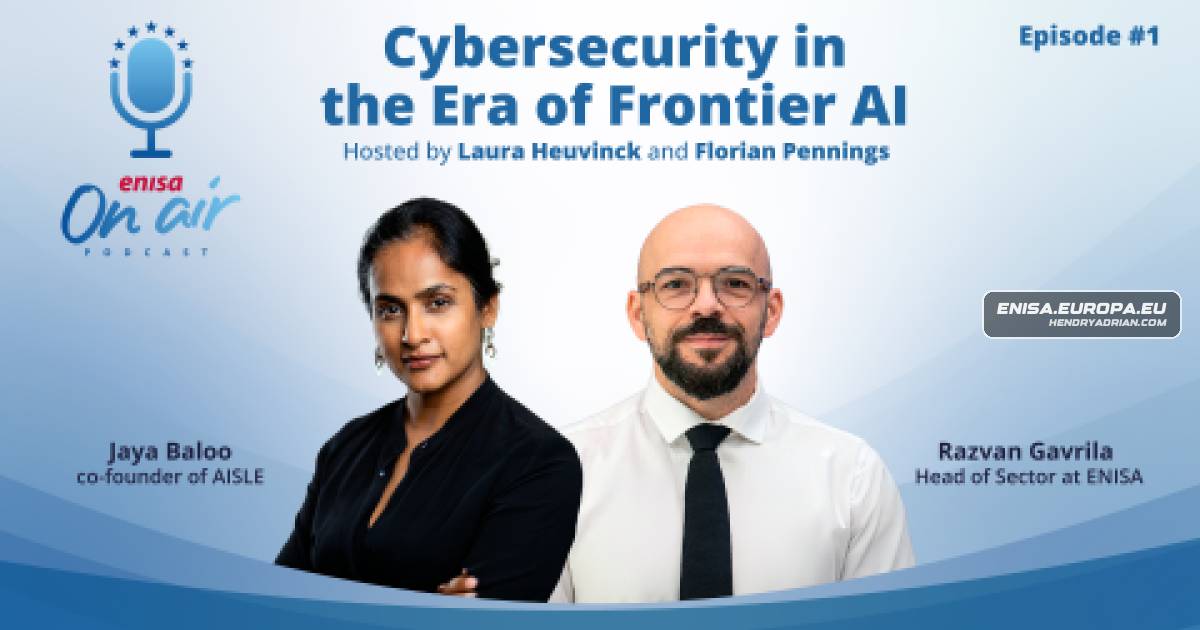
ENISA has launched a podcast series on cybersecurity topics. Its first episode explores Frontier AI’s impact on cybersecurity and discusses ENISA recommendations for building capabilities to address machine-speed threats.

Jul 14, 2026
Security News · recordedfuture.com

Permit-fee Scammers Use 53 Verified Mule Accounts in One Campaign, Researchers Say

CYBERA says it traced a permit-fee impersonation ring to 53 verified US mule accounts across 23 email campaigns. The scammers target property owners using public records and seek payment by wire or other fast-moving payment rails.

Jul 14, 2026
Security News · cyberscoop.com

States build election security networks amid reduced federal support

The firing of two EAC commissioners and DOJ threats of prosecution over voter-registration and ballot issues have heightened election-security concerns. Oregon and Arizona are building local support and ballot-tracking efforts as officials report reduced federal help.

Jul 13, 2026
Security News · bleepingcomputer.com

Malicious Jscrambler npm Releases Delivered an Infostealer

Jscrambler says malicious releases of its npm package were downloaded 1,479 times before removal. The package ran an infostealer during installation; the company revoked publishing credentials and released safe version 8.22.

Jul 13, 2026
Security News · cyberscoop.com

US and 12 Allies Warn of Russian FSB-Linked Attacks on Network Devices

A joint advisory from the U.S. and 12 partner countries says FSB Center 16 is targeting network devices with weak credentials and old Cisco flaws, and urges defenders to disable Smart Install, strengthen authentication and monitor suspicious logins.

Jul 13, 2026
Security News · cyberscoop.com

EU and UK Sanction Russian Entities Over Alleged Turla Espionage and Cyberattacks

The EU and UK imposed sanctions on Russian individuals and entities over alleged cyberespionage and destructive attacks, including activity attributed to Turla. The EU cited a 2010-onward campaign; the UK also targeted figures linked to GRU activity and Lumma Stealer.

Jul 13, 2026
Security News · asec.ahnlab.com

Phishing Emails Use Project Proposals to Deliver SnakeKeylogger

ASEC reports phishing emails posing as project proposals that deliver JavaScript malware. The script runs PowerShell to decrypt and load SnakeKeylogger in memory, which steals browser data, system information, and keystrokes and exfiltrates them via SMTP or Telegram.

Jul 13, 2026
PreviousPage 77 of 159 Next
© 2026 cyber.hendryadrian.com