cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3802 articles

Security News · therecord.media

UK Plans 48-Hour Takedown Rule for Nonconsensual Intimate Images

The U.K. plans to require platforms to remove reported nonconsensual intimate images within 48 hours, with cross-platform takedowns and penalties. Proposed measures include hash matching to block reuploads.
Feb 19, 2026
Security News · securityweek.com

Venice Security Emerges From Stealth With $33 Million for Privileged Access Platform

Venice Security emerged from stealth with $33 million in funding, including a $25 million Series A led by IVP. Its platform provides just-in-time access across cloud, on-premises and SaaS systems, with adaptive policies and no agents or proxies.

Feb 19, 2026
Security News · bleepingcomputer.com

Massiv Android Banking Malware Disguises Itself as an IPTV App

ThreatFabric researchers report that Massiv, an Android banking malware disguised as an IPTV app, targeted a Portuguese government app linked to Chave Móvel Digital. It uses overlays, keylogging and remote-control features to steal data and access accounts.

Feb 19, 2026
Security News · bleepingcomputer.com

INTERPOL-Led Operation Red Card 2.0 Leads to 651 Arrests Across 16 Countries

Operation Red Card 2.0 led to 651 arrests across 16 countries, with more than $4.3 million recovered. INTERPOL said the crackdown identified 1,247 victims and targeted activity linked to over $45 million in losses.

Feb 19, 2026
Security News · darkwebinformer.com

Broker Claims Auction of Domain Admin Access to Peruvian Logistics Firm

An initial access broker using the handle Big-Bro claims to auction domain administrator access to an unidentified Peruvian logistics and business services company, citing a compromised Fortinet VPN appliance.

Feb 19, 2026
Security News · thehackernews.com

Citizen Lab Finds Cellebrite Used on Kenyan Activist’s Phone in Police Custody

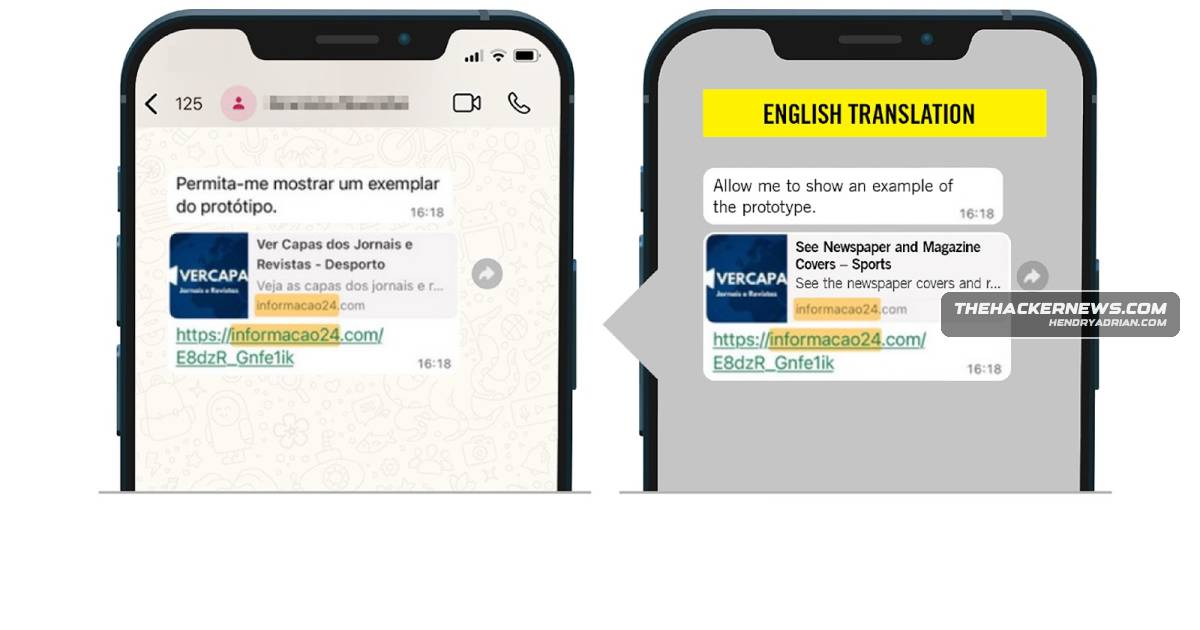
Citizen Lab found high-confidence indicators Kenyan authorities used Cellebrite on activist Boniface Mwangi’s phone in custody. Amnesty separately confirmed Predator infected Angolan journalist Teixeira Cândido’s iPhone via a WhatsApp link.

Feb 18, 2026
Security News · therecord.media

Kaspersky Finds Keenadu Backdoor in Android Tablet Firmware

Kaspersky found the Keenadu backdoor in Android tablet firmware, with over 13,700 users encountering it or related modules. The malware was primarily used for ad fraud and may require clean firmware or device replacement to remove.

Feb 18, 2026
Security News · bleepingcomputer.com

Microsoft Fixes Copilot Bug That Summarized Confidential Emails Despite DLP Controls

Microsoft says a code error let Microsoft 365 Copilot summarize labeled emails in users’ Sent Items and Drafts despite DLP policies. A fix rollout began in early February; the impact scope and full remediation timeline remain unknown.

Feb 18, 2026
Security News · bleepingcomputer.com

Microsoft Says Faulty Phishing Detection Blocked Legitimate Exchange and Teams Links

Microsoft says a logic error caused Exchange Online and Teams to block legitimate URLs and messages from February 5 to 12. The issue, tracked as EX1227432, triggered false alerts; Microsoft plans a final report.

Feb 18, 2026
Security News · therecord.media

Texas Sues TP-Link Over Alleged Security Claims and China-Linked Hacking Risks

Texas Attorney General Ken Paxton sued TP-Link, alleging deceptive security and privacy marketing and citing research on Camaro Dragon campaigns exploiting TP-Link firmware flaws. TP-Link denies the claims; experts describe a broader consumer-protection enforcement###

Feb 18, 2026
Security News · thecyberexpress.com

India AI Summit Panel Urges Red Teaming and Cyber Readiness as AI Scales

At the India AI Impact Summit 2026, panelists called for stronger AI governance and continuous security testing. Cyble’s Beenu Arora cited deepfake-call activity and financial losses as examples of emerging risks.

Feb 18, 2026
Security News · securityweek.com

Kaspersky Finds Keenadu Android Malware in Firmware and Fake Apps

Kaspersky reports Keenadu in Android firmware and fake camera apps, with detections on roughly 13,000 devices. The malware enables remote control and appears mainly used for ad fraud; researchers also found a connection to BadBox.

Feb 18, 2026
Security News · securityweek.com

Cogent Security Raises $42 Million to Develop AI Agents for Vulnerability Remediation

Cogent Security raised $42 million in Series A funding to develop autonomous AI agents for vulnerability remediation. Its platform connects vulnerability data, prioritizes risks using business context, and generates remediation plans.

Feb 18, 2026
Security News · thecyberexpress.com

OpenAI Adds Lockdown Mode and Elevated Risk Labels to ChatGPT

OpenAI introduced Lockdown Mode for high-risk ChatGPT users, restricting network access and some features, plus Elevated Risk labels for network-related capabilities. The company says the controls address prompt-injection risks.

Feb 18, 2026
Security News · securityweek.com

Palo Alto Networks to Acquire Koi in Deal Reportedly Valued at $400 Million

Palo Alto Networks agreed to acquire endpoint security firm Koi. The companies did not disclose financial terms; Israeli publications reported a $400 million valuation. Palo Alto said Koi’s technology will enhance its AI and endpoint security offerings.

Feb 18, 2026
Security News · thehackernews.com

Researchers Show Copilot and Grok Can Be Abused as Malware C2 Proxies

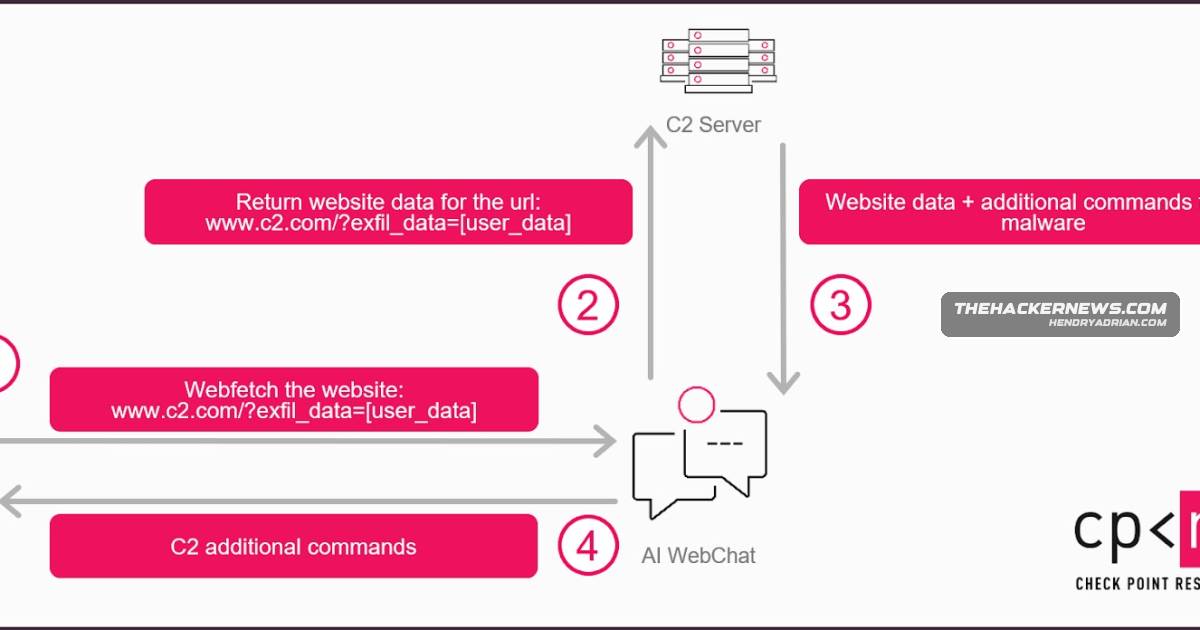
Check Point demonstrated that Microsoft Copilot and xAI Grok browsing features can relay attacker commands and victim data as C2 traffic. The technique requires an already-compromised host and installed malware, but no API key or registered account.

Feb 18, 2026
Security News · securityonline.info

UNC6201 Exploits Dell RecoverPoint Zero-Day to Deploy GRIMBOLT

Mandiant and Google GTIG report that suspected PRC-nexus cluster UNC6201 has exploited CVE-2026-22769 in Dell RecoverPoint for Virtual Machines since at least mid-2024, using Ghost NICs and stealthy persistence and adding GRIMBOLT in 2025.

Feb 18, 2026
Security News · securityonline.info

CRESCENTHARVEST Campaign Uses Protest-Themed Lures to Target Iranian Dissidents

Acronis TRU reports that CRESCENTHARVEST uses protest-themed .LNK lures and DLL sideloading through a signed Google executable to deploy a RAT capable of command execution, keylogging and data theft against Iranian dissidents and supporters.

Feb 18, 2026
Security News · cofense.com

Cofense Reports Phishing Campaigns Using Fake Microsoft and Google Calendar Invites

Cofense observed spoofed Microsoft and Google Calendar invites with links to fake login pages that harvest credentials. It recommends checking sender details and URLs and using phishing defenses.

Feb 17, 2026
Security News · bleepingcomputer.com

Notepad++ 8.9.2 Adds Dual Verification to Secure Updates

Notepad++ 8.9.2 verifies GitHub-signed installers and XMLDSig-signed update metadata, hardening updates after a six-month compromise attributed to Lotus Blossom that used the Chrysalis backdoor.

Feb 17, 2026
Security News · bleepingcomputer.com

UNC6201 Used Dell RecoverPoint Zero-Day Since Mid-2024, Researchers Say

Mandiant and Google Threat Intelligence Group say suspected China-backed UNC6201 exploited a hardcoded-credential flaw in Dell RecoverPoint for Virtual Machines since mid-2024, deploying Grimbolt and using Ghost NICs to move through VMware environments.

Feb 17, 2026
Security News · therecord.media

Polish Police Arrest Man Allegedly Linked to Phobos Ransomware Operation

Polish police arrested an unnamed 47-year-old allegedly linked to Phobos after finding encrypted messages on his computer. The arrest comes amid Operation Aether actions against Phobos and 8Base, including arrests and more than 100 server takedowns.

Feb 17, 2026
Security News · securityweek.com

VulnCheck Raises $25 Million in Series B Funding

VulnCheck raised $25 million in a Series B round to expand product development and growth. Its platform tracks vulnerability lifecycles, exploit availability, proof-of-concept code and weaponized payloads to help teams prioritize patching.

Feb 17, 2026
Security News · feeds.feedblitz.com

Shai-Hulud Detector’s Test Files Contained Executable Malware

G DATA found that test files for a Shai-Hulud detection tool contained real malware capable of deleting user directories and uploading data. The maintainer later neutralized the files.

Feb 17, 2026
PreviousPage 142 of 159 Next
© 2026 cyber.hendryadrian.com