
m3rx Claims Theft of 120 GB From dmschweiz.ch
m3rx claims it stole 120 GB, comprising about 100,000 files, from dmschweiz[.]ch. The group also advertises catalogs of pre-installed devices and customizable installations. The claim is unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2834 articles
m3rx claims it stole 120 GB, comprising about 100,000 files, from dmschweiz[.]ch. The group also advertises catalogs of pre-installed devices and customizable installations. The claim is unconfirmed.
LockBit5 claims it encrypted systems at St. Luke Lutheran Community and threatens to leak data unless a ransom is paid. The claim is unconfirmed and was attributed to the actor’s leak-site post.
LockBit5 claims it encrypted Instapack[.]es systems and exfiltrated sensitive data, demanding ransom and threatening publication or auction. The monitoring post says the claims are unconfirmed.
LockBit5 is named in a ransomware claim against Pricon Microelectronics, Inc. in the Philippines. The post attributes the claim to the group's leak site and says it is unconfirmed; compromise, encryption, or exfiltration is not independently established.
LockBit5 claims it compromised Planet Sport, an online sports store in Morocco, and threatens to encrypt data and leak sensitive information. The claim concerning planetsport[.]ma is unconfirmed.
Ransomware.live lists an unverified LockBit 5 claim naming defcon5italy[.]com; the post says the information is based on the group's public claim and has not been confirmed.
A leak-site claim attributed to Qilin names Construction Sciences as a ransomware victim. ransomware[.]live records the claim; the article says it cannot confirm its accuracy.
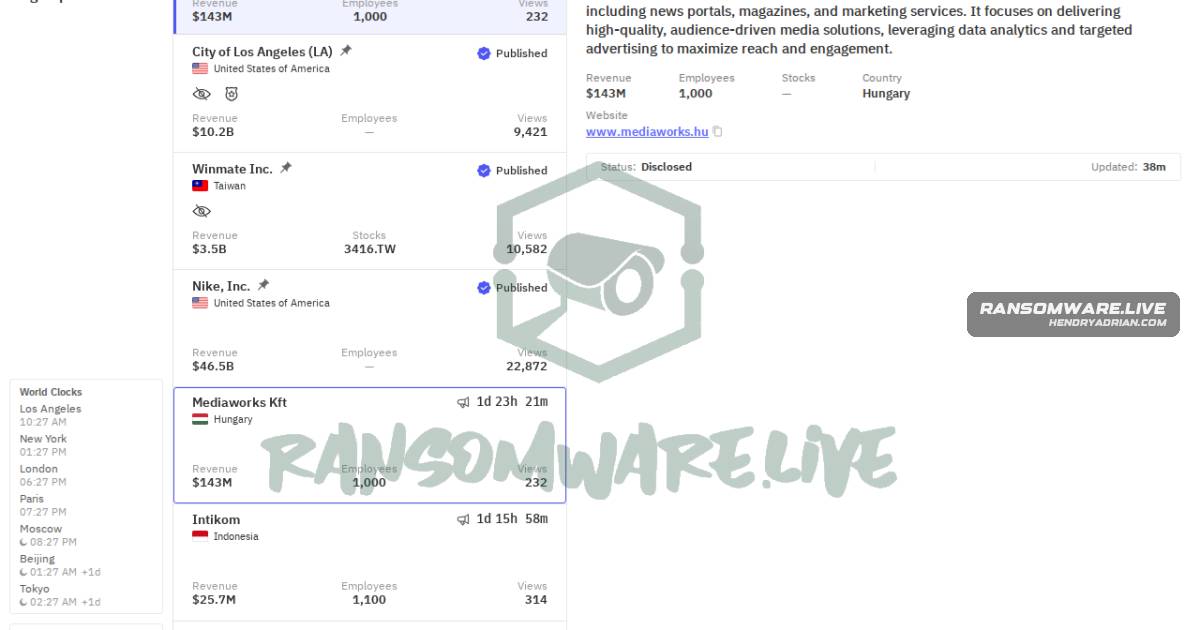
A ransomware claim attributed to worldleaks lists Hungary-based Mediaworks Kft as a victim. The post cites the group’s leak site and says the claim is unconfirmed; no further incident details are available.
A ransomware claim attributed to Qilin lists KarmaData, a US technology company, as a victim. The post was recorded on April 28, 2026; the claim is unconfirmed, and methods and impact are not provided.
A monitoring post says incransom listed North Bay Distribution as a ransomware victim. The post says the claim is unconfirmed and provides no verified impact details.
Incransom claims to have exfiltrated 2 TB of Fulcrum RE data. The claim is unverified; the post says it is based on the group’s public claim and invites an official response.
A leak-site post attributed to Chaos threatens to publish an alleged 400 GB of Cadence Petroleum files in 48 hours unless an agreement is reached. The claim is unconfirmed.
A ransomware.live monitoring record attributes a ransomware claim against Indonesia’s Customs Analytics Platform to Everest. The post says the claim is unconfirmed; possible operational disruption is alleged.
Ransomware.live reports that Qilin listed UK technology company Silicon Alley in a ransomware claim. The claim is unconfirmed; the post provides no details about a ransom or leaked data.
Insomnia claims it encrypted patient records at Nephrology Associates, PA, across seven locations and threatens to leak or sell sensitive information if the ransom is not paid. The claim is unconfirmed.
WorldLeaks claims it targeted Mexico-based Carma Packaging, alleging encrypted files and a ransom demand. The claim is attributed to the group's leak site and monitored by ransomware[.]live; the publisher says it cannot confirm the information.

A ransomware claim attributed to SilentRansomGroup names Floyd Skeren Manukian Langevin, LLP as a victim. The post says encryption and data exposure were alleged; the claims are unconfirmed.
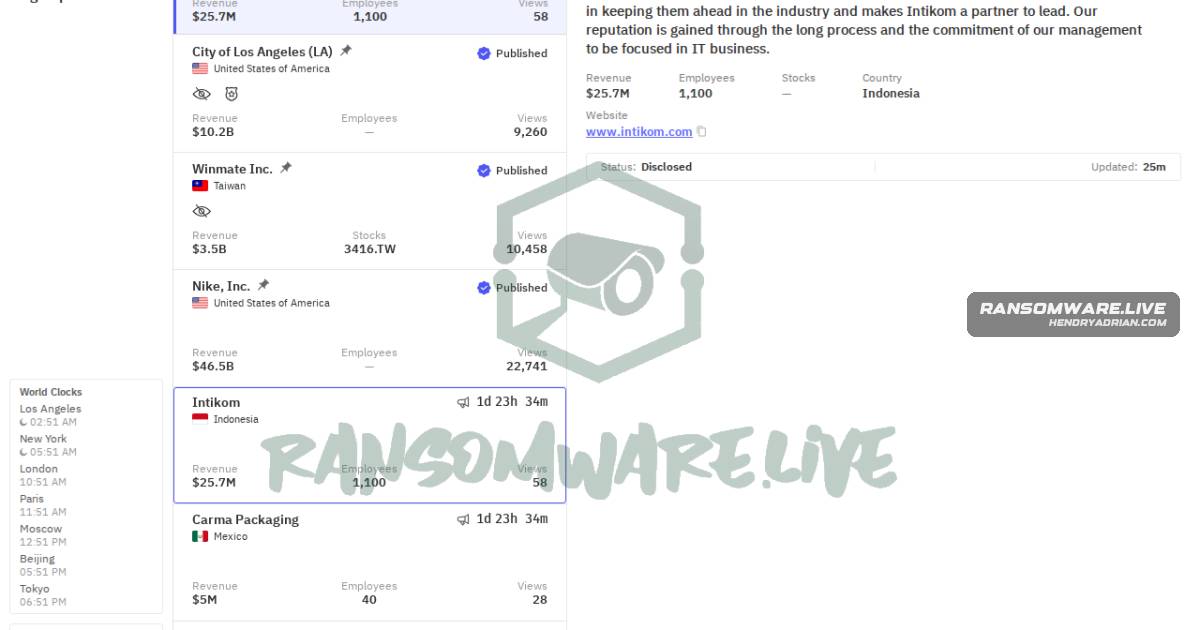
WorldLeaks claims it targeted Indonesian IT provider Intikom, alleging system encryption and potential data theft. The article says the claim is unconfirmed.
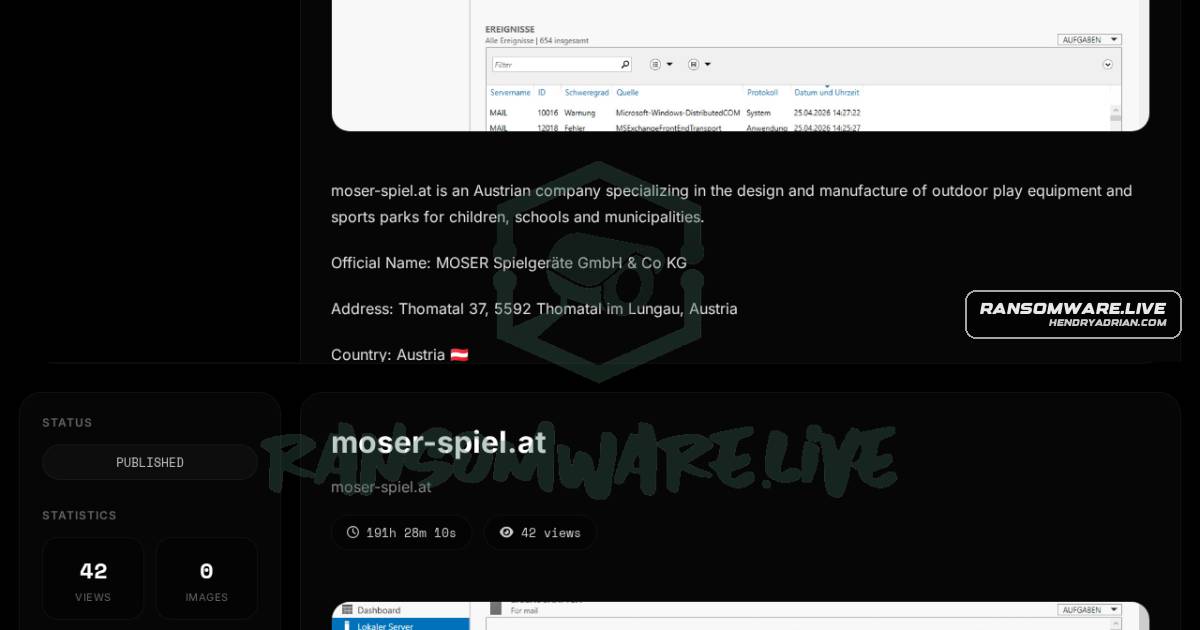
Ransomware.live reports an unverified Krybit claim targeting Austrian outdoor-play equipment maker Moser-Spiel (moser-spiel[.]at); the post alleges encryption, possible data exfiltration and operational disruption, none independently confirmed.
Qilin claims Lifeline PCS in the US as a ransomware victim, alleging file encryption and potential data exfiltration. The claim is attributed to the group, but independent verification is unavailable.
A ransomware.live monitoring record says Everest claimed to target Super AI, encrypt files and demand payment for decryption. The claimed impact is not independently verified.
A Ransomware.live record attributes a ransomware attack claim against Super AI to Everest and cites the actor’s leak-site post. The claim is unconfirmed.
ShinyHunters claims Vimeo, Inc.’s Snowflake and BigQuery data was compromised via Anodot[.]com and demands payment, threatening to leak the data after an April 30, 2026 deadline. The claim is unconfirmed.
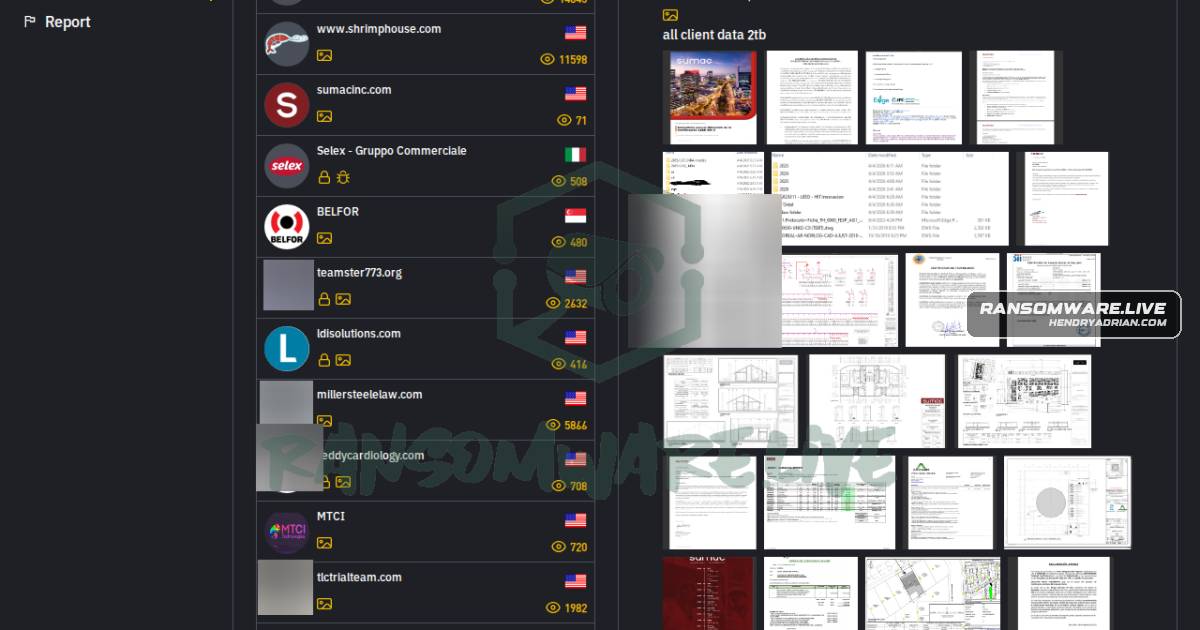
The incransom ransomware group claims it breached sumacinc[.]com and accessed 2 TB of client data. The claim is unverified and attributed to its leak-site post, as tracked by ransomware[.]live.