
LockBit5 Claims Ransomware Attack on St. Luke Lutheran Community
Summary
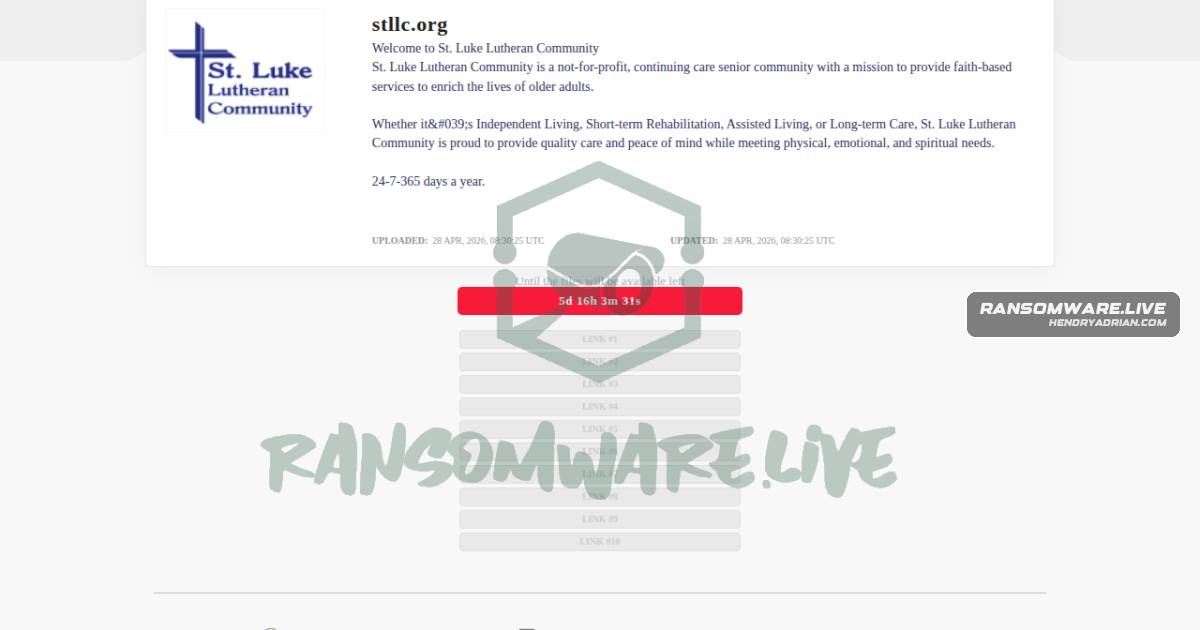
LockBit5 claims it encrypted systems at St. Luke Lutheran Community and threatens to leak data unless a ransom is paid. The claim is unconfirmed and was attributed to the actor’s leak-site post.
Key points
- The monitored record names St. Luke Lutheran Community, a US-based not-for-profit, as the claimed victim.
- LockBit5 claims it encrypted the organization’s systems and threatens data leakage unless a ransom is paid.
- The claim is attributed to a LockBit5 leak-site post; the article says it cannot confirm the claim’s accuracy.
Article Details
- Victim
- St. Luke Lutheran Community
- Victim Domain
- stllc.org
- Claim Date
- 2026-04-28
- Encryption Status
- LockBit5 claims systems were encrypted; this is unverified.
- Exfiltration Status
- Not reported; the actor threatens data leakage, but no exfiltration is confirmed.
- Ransom Demand
- An unspecified ransom is implied by the threat to leak data unless ransom is paid; no amount is reported.
- Leak Status
- Leakage was threatened; no leak or publication is reported.