
Qilin Claims Johnson Carter Architects as a Ransomware Victim
A ransomware.live record attributes a ransomware claim involving Johnson Carter Architects to Qilin and provides a Qilin leak-site source. The article says the claim is unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2832 articles
A ransomware.live record attributes a ransomware claim involving Johnson Carter Architects to Qilin and provides a Qilin leak-site source. The article says the claim is unconfirmed.
A monitoring record says Qilin claimed a ransomware attack on LTJ Industrial Services, alleging operational disruption and data access. The claim is unconfirmed.

A ransomware claim attributed to cmdorganization names Ira & Larry Goldberg Coins & Collectibles. The claim is unconfirmed; the post says it is monitored by ransomware[.]live.
A ransomware.live monitoring post attributes a claim against Canadian company Brand X Hydrovac Services to Qilin. The post reports alleged disruption and encrypted or inaccessible data, but says the group's claims are unconfirmed.
Stormous claims it has financial backups, email archives, staff folders, customer databases, and shipment records from vspsolutions.com.au. The claim is unconfirmed and monitored by ransomware[.]live.
Ransomware.live lists an unconfirmed KillSec ransomware claim against dsdlawfirm[.]com in the US, discovered May 14, 2026. The listing shows an undisclosed ransom price and 0/1 disclosures.
Stormous allegedly claims to have stolen 5 TB of data from Vietnam-based TTT Company (ttt[.]vn) and demanded $900,000. The post says the claim is unconfirmed and monitored by ransomware[.]live.
Ransomware.live lists Bluize in Australia as a Qilin ransomware claim, discovered and published May 13, 2026. The post says the claim is unconfirmed; disruption is not independently verified.
Incransom claimed it leaked more than 450 GB of Silergy Corp data, including financial records, contracts, passports, and customer and partner information. The claim is unconfirmed.
A ransomware.live monitoring post attributes a ransomware claim naming Mayer in the US to Qilin. The post says the claim appeared on the group's leak site but notes that it could not confirm the information.
A ransomware.live monitoring post attributes a ransomware claim naming US-based Spirit Medical Transport to Qilin. The post says the claim is unconfirmed and invites an official statement from the organization.
A ransomware.live record attributes to Akira a claim of data theft from France-based Allele Diagnostics, including employee and patient information. The claim is unconfirmed.
A ransomware claim attributed to coinbasecartel names Argentina-based Buenos Aires Software. The post alleges encrypted systems and service disruption but says the claims are unconfirmed.
Akira claims it will publish 55 GB of the Institute of Private Enterprise Development’s data, allegedly including client and employee personal and financial information. The claim is unconfirmed.
A ransomware.live monitoring record attributes a claim against Ukrainian public-sector organization SHERIFF to Qilin. The group reportedly claims encryption and data exfiltration; the information is unverified.

Anubis claims A.R.Ge.Co., an Italian accounting firm, was targeted. The monitored claim is unconfirmed; the post says it cannot verify the group's assertions.
ransomware[.]live reports that SilentRansomGroup claimed it offered Marshall Dennehey $100,000 to prevent data publication. The post says it cannot confirm the claim.
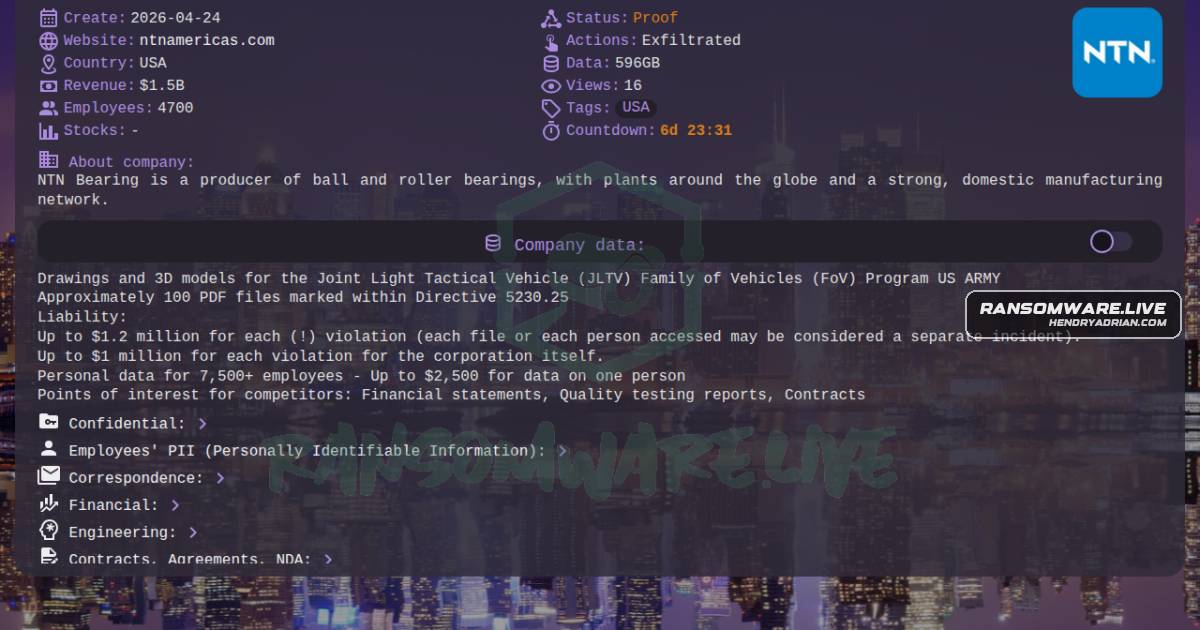
A ransomware-monitoring post attributes a claim against NTN Bearing Corporation of America to Payoutsking. U.S. operational impact is alleged; the post says the claim is unconfirmed.
A ransomware.live monitoring post attributes a ransomware claim targeting US law firm Porter Wright to SilentRansomGroup. The post says the claim is unconfirmed.
Ransomware.live lists The Gravity Group as a Qilin ransomware-claim victim. The post alleges an incident but says it cannot verify the group’s claims.
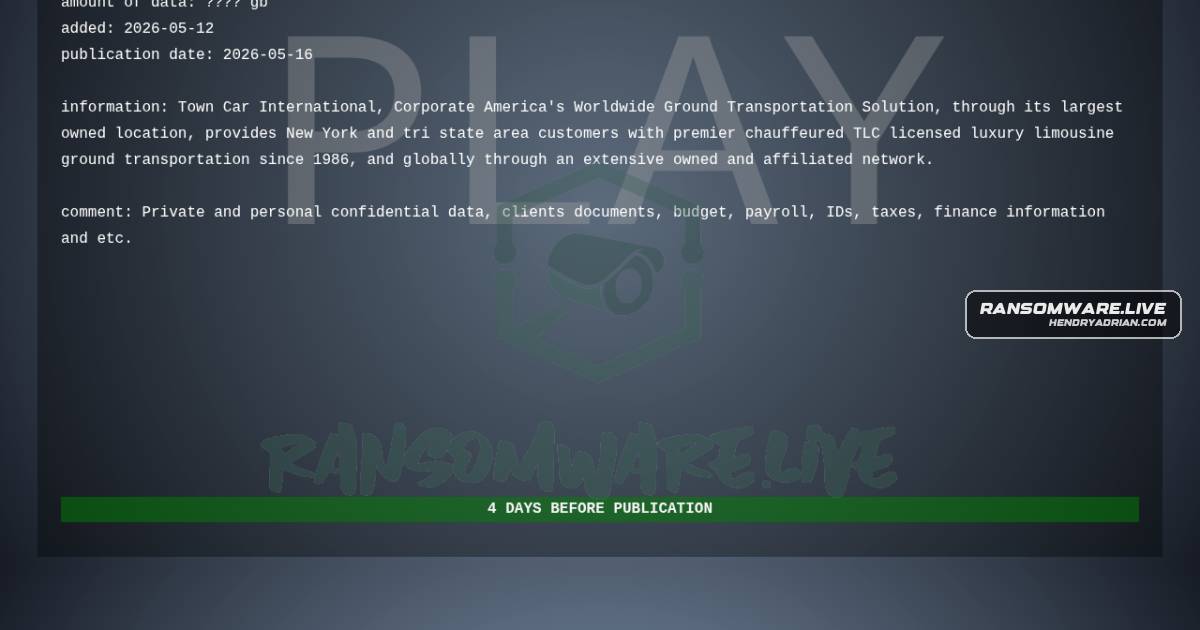
Ransomware.live records an unconfirmed Play ransomware claim targeting Town Car International in the US. The post alleges encrypted systems and business disruption but says it cannot confirm the claim.
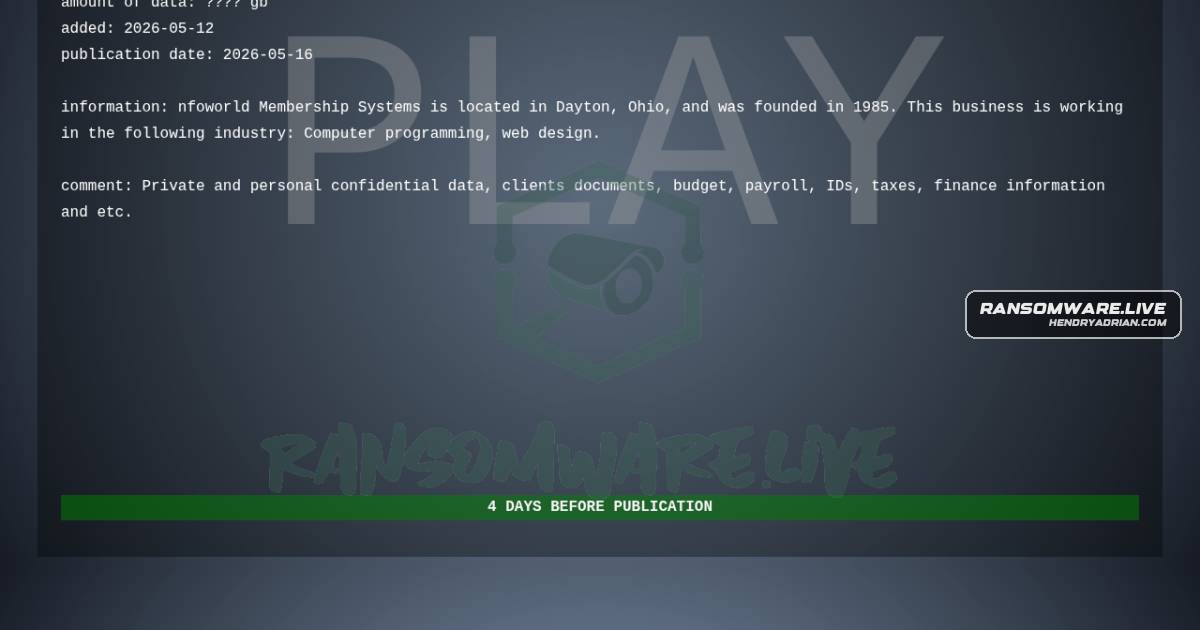
Ransomware.live lists an unverified Play ransomware group claim targeting Infoworld Membership Systems in the United States. The post says files were encrypted and access to critical systems disrupted; those impacts are not independently confirmed.
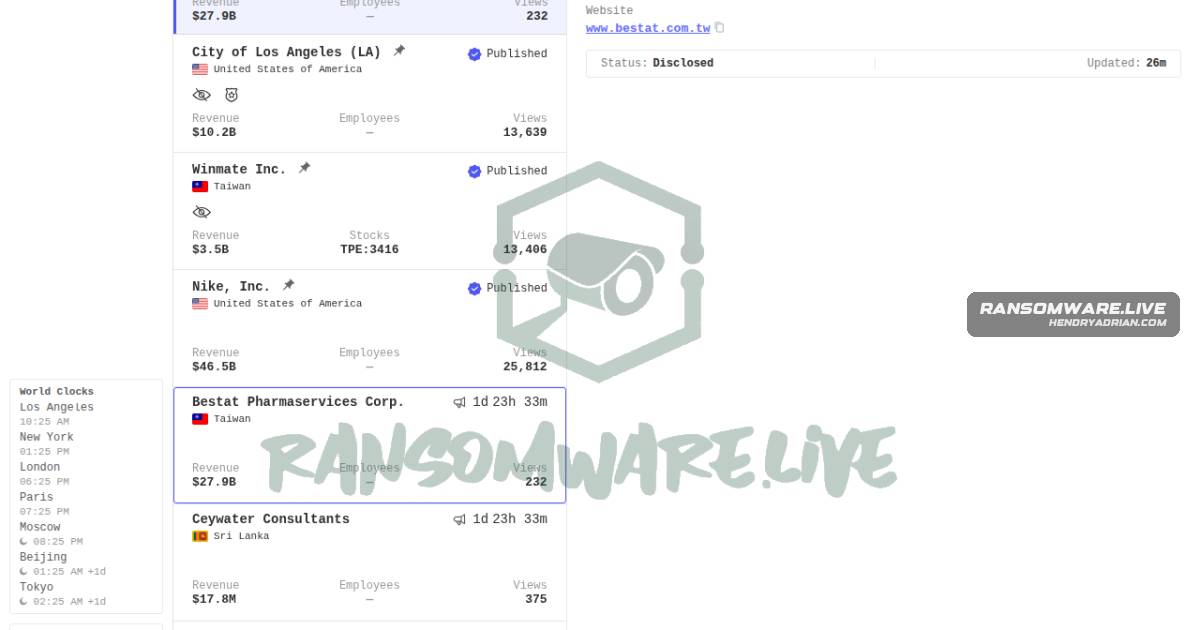
Ransomware.live lists Bestat Pharmaservices Corp. in Taiwan as a Worldleaks claim dated May 12, 2026. The post says the claim is unconfirmed; encryption, disruption and possible data exposure are not independently verified.
Akira claims it will leak 45 GB of Kaplan Companies data, including personal documents, financial records, contracts and project files. The claim is unverified; the post says it is monitored by ransomware[.]live.