
Play ransomware group claims attack on Infoworld Membership Systems
Summary
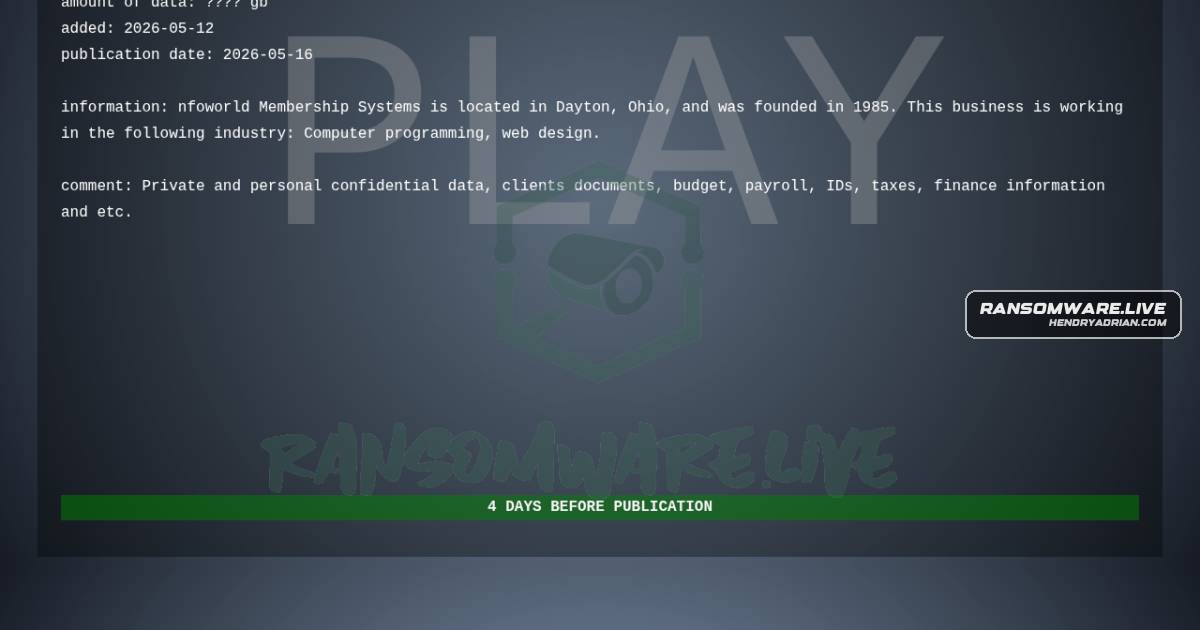
Ransomware.live lists an unverified Play ransomware group claim targeting Infoworld Membership Systems in the United States. The post says files were encrypted and access to critical systems disrupted; those impacts are not independently confirmed.
Key points
- The named victim is Infoworld Membership Systems, identified as a United States technology organization.
- The post attributes the ransomware claim to the Play group and cites a leak-site source.
- The post alleges encrypted files and disruption of access to critical systems; these claims are unverified.
- The claim was listed and discovered on May 12, 2026, and monitored by ransomware.live.
Article Details
- Victim
- Infoworld Membership Systems
- Encryption Status
- Claimed; unverified. The article reports encrypted files but says the information is based on the ransomware group’s public claims and cannot be confirmed.
- Encrypted Size
- Unknown
- Exfiltration Status
- Unknown
- Exfiltrated Data
- Unknown
- Exfiltrated Size
- Unknown
- Ransom Demand
- Not disclosed
- Leak Status
- Unknown; the article does not report whether victim data was leaked or published.