
Krybit Claims Ransomware Attack on MotoFrenos
Ransomware.live lists MotoFrenos (motofrenos[.]com) as a Krybit victim, claiming file encryption and operational disruption; the post says the claims are unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2828 articles
Ransomware.live lists MotoFrenos (motofrenos[.]com) as a Krybit victim, claiming file encryption and operational disruption; the post says the claims are unconfirmed.
Ransomware.live lists US construction company Roofing Solutions as a Qilin victim. The post attributes the claim to the group’s leak site and says it cannot verify the incident.
ransomware.live monitored a Qilin claim naming Shocco Springs in the US as a ransomware target. The post says system access was disrupted and data may have been encrypted, but the claims are unconfirmed.
Ransomware[.]live lists Mainstreet Organization of REALTORS as a Qilin ransomware victim, citing the group’s leak-site post. The entry alleges file encryption and disruption, but the article says the claims are unconfirmed.

ransomware.live lists a DragonForce claim targeting WaypointSolutions[.]com and alleging disruption to customer IT services through Dell partnerships. The post says the claim is unconfirmed.

Ransomware.live attributes a claim concerning ERH’s UK traffic management operations to DragonForce. The group allegedly caused service disruption and compromised data; the article says these claims are unconfirmed.

Ransomware.live lists a DragonForce claim targeting fabbricausa[.]com, identified as Fabbrica LLC. The post cites the group's leak site and says the claim's accuracy is unconfirmed.

A ransomware claim-monitoring post attributes a claimed incident affecting Berlin housing cooperative WG Neukölln eG to DragonForce. The post says the claim is unconfirmed.

Ransomware.live reports that DragonForce claimed Delbrook Capital Advisors as a victim. The post alleges operational disruption, but says the claim is unconfirmed.

DragonForce allegedly claimed ransomware activity involving Greenway Technologies in Germany. The claim was recorded by ransomware.live, which says it could not confirm the information.
Ransomware group spacebears claims it compromised more than 1.6 TB of Ridge Law Firm data, including medical and financial records. The claim is unconfirmed.
Ransomware.live reports that spacebears claims to have attacked Gestordes in Spain, exposing passports, IDs, financial documents and more than 200,000 files. The claim is unconfirmed.
Nova claims it targeted Textile Testing Services of America, identifying sandox[.]info as an initial access point and linking data to ttsamexico[.]com. The group says it provided data samples to the company; the claims are unverified.
A ransomware.live record attributes a data-theft and extortion claim against Eriell to Nova. The claim appears on Nova’s leak site; the post says it has not been independently confirmed.
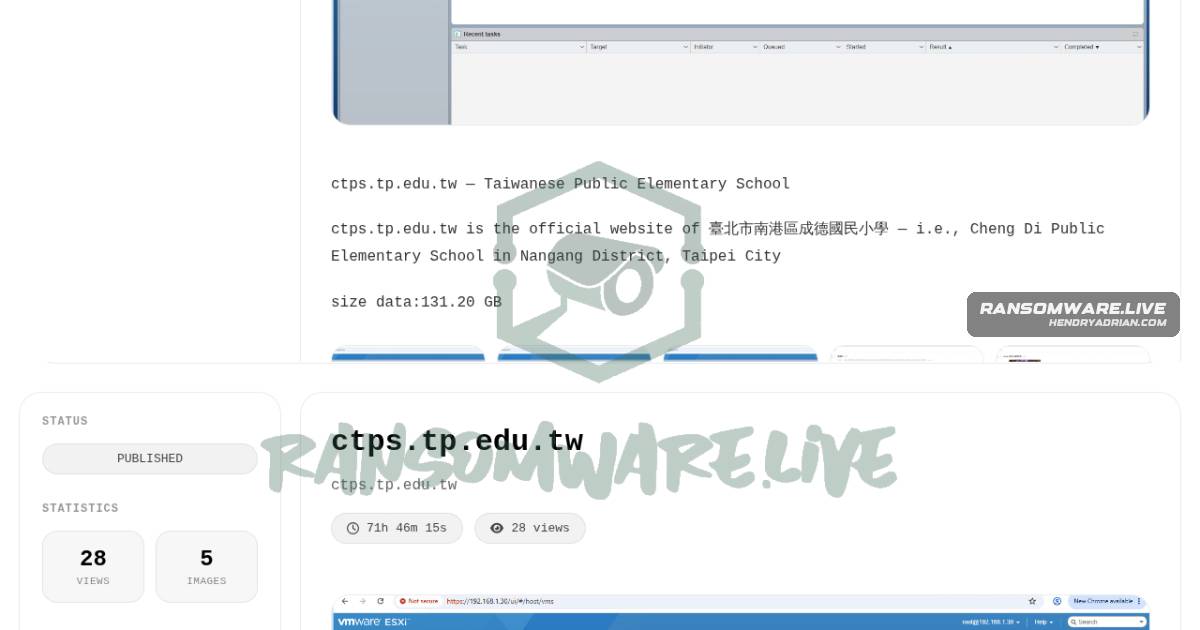
Ransomware.live reports that krybit claimed a ransomware incident involving ctps[.]tp[.]edu[.]tw, the official website of a Taiwanese public elementary school. The claim is unconfirmed.
ransomware.live reports an unverified Nova ransomware claim targeting Sandox[.]info. The post says the site went down afterward and that Nova offered stolen-data samples and a directory tree; available OSINT is limited.

Akira claims to have obtained 13GB of data from Sunrise, Toscana Country Club and Andalusia Country Club. The alleged material includes personal, financial and client information; the claims are unconfirmed.
ransomware.live reports that Qilin listed Hamister Group as a victim. The group allegedly encrypted data and disrupted systems; the claims are unconfirmed.
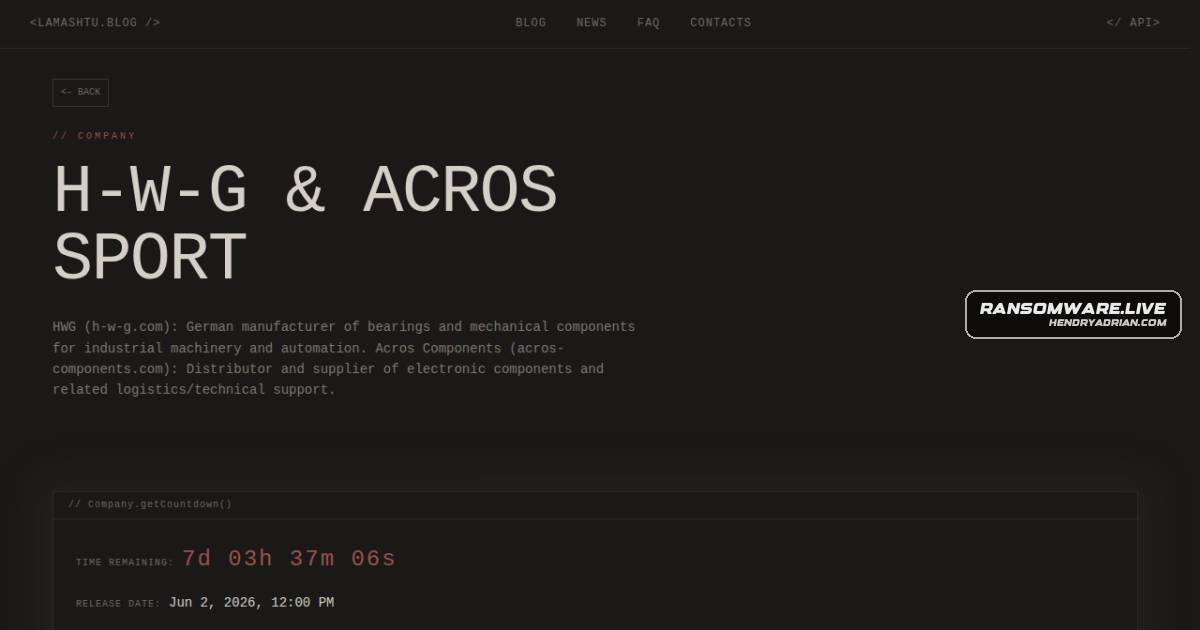
Ransomware.live records an unverified lamashtu claim naming H-W-G & Acros Sport, published May 26, 2026. The post attributes the information to the group’s public claim; the publisher says it cannot confirm its accuracy.
The spacebears ransomware group claims it stole and encrypted confidential and personal employee and client information, financial documents, and other files from Italy-based BASE S.p.A. The claim is unconfirmed.
SpaceBears claims Hunter exposed employee and client information, databases, financial documents, and other files. The post attributes the claim to the group's leak site and says it could not confirm its accuracy.
The Spacebears ransomware group reportedly claims Filabé, a Switzerland-based skincare company, had employee and client information, financial documents and other files encrypted or exfiltrated. The claim is unconfirmed.
ransomware.live reports that the Play ransomware group claimed to target De Waard Transport in the Netherlands. The post says access to systems and data was disrupted, but the claim is unconfirmed.
Ransomware.live lists Open Door Health Center, an Illinois healthcare provider, as targeted by Incransom. The post attributes the claim to the group's disclosure page but says it cannot confirm the information.